
Submitted:
15 September 2026
Posted:
16 September 2026
You are already at the latest version
Abstract
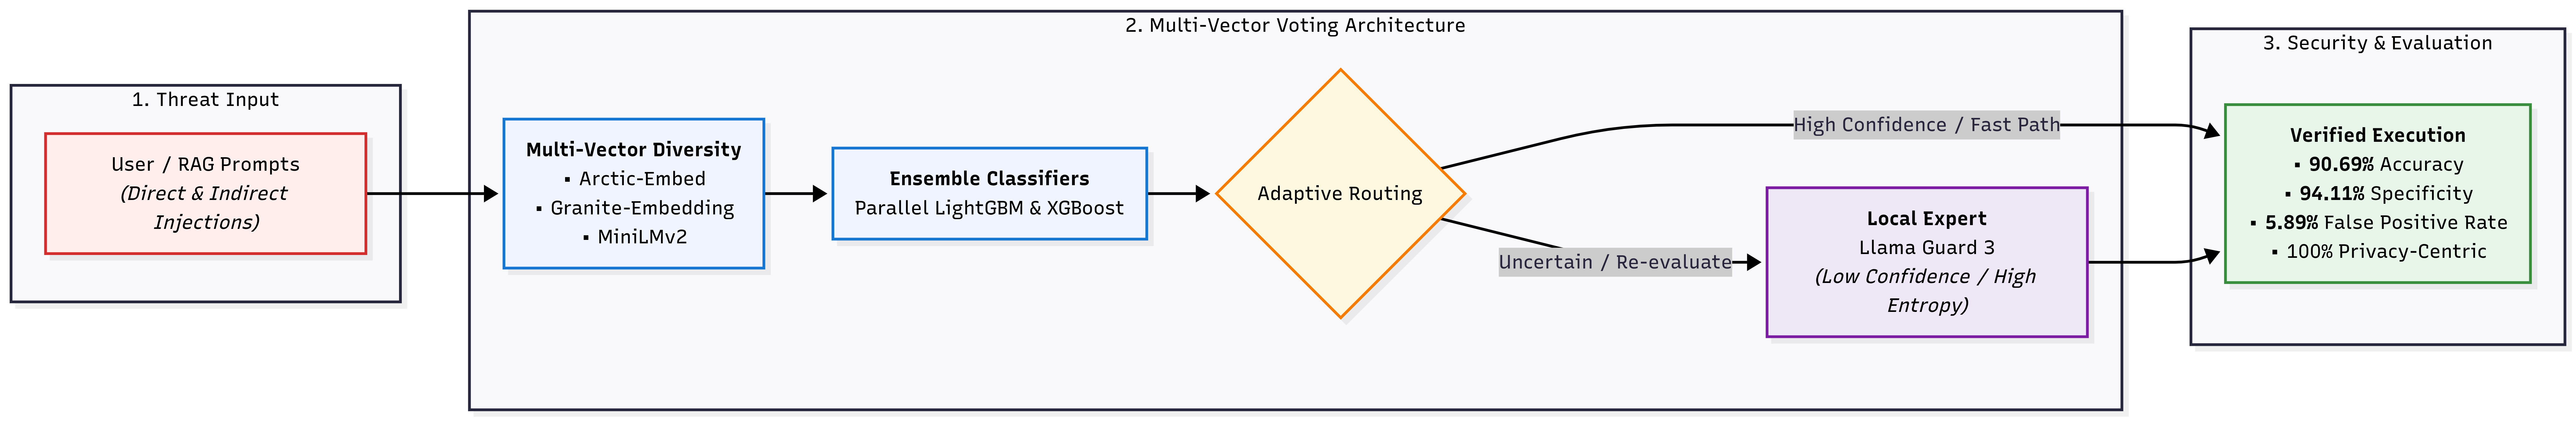
Large Language Models (LLMs) suffer from the problem of prompt injection vulnerability, but typical one-step defenses generally fail at the task by having a high amount of false positives. We introduce an innovative two-sided defense architecture that applies semantic multi-vector diversification and ensemble modeling to provide LLM protection without the need for closed black-box solutions. In our framework, we use three different semantic spaces mapping via publicly available embedding algorithms, where each is then scored by parallel classifiers based on gradient boosting machines. The inputs go through an adaptive voting-based routing process; those that receive low entropy ratings are classified normally, while high entropy items are sent through a secondary classifier – a local LLM expert, the Llama Guard 3, that handles the input. Importantly, this solution uses a two-way protection method, which checks the generated outputs and catches late execution and context manipulation vectors. Our experiments on a 93K dataset show that the ensemble approach performed better than any individual sub-model, reaching 90.69 % accuracy and 94.11 % specificity, minimizing any user experience disturbances. The multi-vector layer demonstrated high empirical resilience to tokenization errors, while the output layer filtered out many bypassed malicious items.
Keywords:
prompt injection attacks
; ensemble learning
; Large Language Models
; semantic diversity
Copyright: This open access article is published under a Creative Commons CC BY 4.0 license, which permit the free download, distribution, and reuse, provided that the author and preprint are cited in any reuse.