

Submitted:
30 January 2024
Posted:
31 January 2024
You are already at the latest version
Abstract
The Internet of Medical Things(IoMT) has powerful cloud computing ability and efficient data collection ability, which can improve the accuracy and convenience of medical work. As most communications are over open networks, data should encrypted before uploading to ensure the confidentiality of sensitive user data. Searching for encrypted data has become a challenging problem. Public key Encryption with Keyword Search (PEKS) supports the search of encrypted data and provides data privacy protection. PEKS has become a trendy technology, but PEKS still has the following problems: 1. The cloud server, as a semi-honest but curious third party, is likely to return some wrong search results to save computing and bandwidth resources. 2. The single keyword search inevitably produces irrelevant results, wasting computing and bandwidth resources. 3. Most PEKS schemes use bilinear pairing, so the computational efficiency is relatively low. 4. PEKS schemes based on Public Key Infrastructure (PKI) or identity-based cryptography inevitably face problems with certificate management or key escrow. 5. Most PEKS schemes face serious security threats such as Keyword Guessing Attacks (KGA) and File Injection Attacks (FIA). To solve the above problems, we propose a new certificateless verifiable bilinear pair-free conjunctive keyword search encryption scheme(CLVPFCKS) for IoMT using multi-signature.
Keywords:
Internet of medical things (IoMT)
; certificateless encyption with keyword search
; standard model
; keyword guessing attack
; file injection attack
; security
; privacy
0.Introduction
Internet of Things is a network that connects any item to the Internet and uses information sensing devices such as radio frequency identification, infrared sensors, global positioning systems, and laser scanners to exchange and communicate information according to agreed protocols, achieving intelligent identification, positioning, tracking, monitoring, and management [1,2]. The Internet of Medical Things (IoMT) conveniently connects communication technology, medical staff, patients, various medical devices, and intelligent facilities, thus completing brilliant medical care and innovative item management. The Internet of Medical Things system can achieve real-time feedback on the health status of patients, improve medical response speed, provide 24-hour medical care, significantly reduce the work pressure of medical personnel, improve the accuracy and convenience of medical work, improve clinical medical quality, control costs, reduce efficiency, and save lives.
Electronic Medical Record (EMR) is crucial in IoMT systems. It electronically manages personal health status and healthcare information involving patient information collection, storage, transmission, processing, and utilization.The volume of medical data will inevitably surge as medical data is collected through various channels digitally. How to effectively store and manage the increasing number of electronic medical records has become an unprecedented challenge. In response to this problem, cloud computing can be a supplementary tool. With cloud computing, hospitals, and medical organizations outsource EMR to cloud servers for storage to save local data management and system maintenance costs while also achieving resource sharing with data recipients. Figure 1 shows a typical architecture of IoMT for medical IoT.
EHRs involve patients’ privacy, and are often encrypted to protect patients’ privacy and security. However, this causes great inconvenience for users to search for EMRs containing specific keywords. A simple solution to this problem is for users to download all ciphertext data fully, decrypt it, and further search locally. However, this leads to high computational and communication costs, making them impractical. To solve this problem, researchers have proposed searchable encryption (SE) [7] technology. It is an encryption primitive that enables users to search for keywords on ciphertext in a privacy-protected manner. In 2004, Boneh et al. [8] proposed the concept of public key encryption with keyword search (PEKS) to solve the problem of searching data encrypted using public key cryptosystems.
1. Related work
The initial PEKS scheme had many areas for improvement regarding efficiency and safety. Firstly, review the efforts made by numerous researchers in improving the efficiency of PEKS. Baek [9] pointed out the inefficiency of the PEKS [8] scheme due to the use of secure channels. To eliminate the requirement for security channels, Baek et al. proposed the concept of secure channel-free PEKS (SCF-PEKS), also known as PEKS, with designated servers/testers (dPEKS) [10]. The efficiency of SCF-PEKS is improved. However, the PEKS (SCF-PEKS) schemes are built based on PKI or identity-based cryptosystem and encounter certificate management issues and key escrow issues in system deployment. To avoid the problems associated with certificate and key escrow, Peng et al. [11] proposed a certificateless keyword searchable encryption scheme (CLKS) without secure channels. Subsequently, much literature has studied certificateless searchable encryption schemes with keywords, such as [12–15]. Most PEKS schemes focus on searching for a single keyword, but single keyword search inevitably produces many irrelevant results, leading to bandwidth and computational resource waste. Golle et al. [16] proposed the first conjunctive keyword searchable encryption scheme to avoid resource waste. After this, many searchable encryption schemes, such as [17–19], support conjunctive keyword search.
Because the computational complexity of bilinear pairs is much higher than that of scalar multiplication on elliptic curve groups, designing searchable encryption schemes without bilinear pair operations can significantly improve the scheme’s efficiency. However, currently, there are not many searchable encryption schemes without bilinear [11,15,20–27], and they are not perfect enough. In 2019, Lu et al. [28] proposed a pairing-free certificateless searchable public key encryption scheme, proving that this scheme achieves indistinguishability of keyword ciphertext against adaptive keyword selection attacks under the complexity assumption of computing Diffie-Hellman problems in a random oracle model. However, Ma et al. [30] found that the scheme proposed in [28] is not secure against user simulation attacks and offered a new cloud-based IIoT pairing-free dual server CLPEKS scheme. Recently, [25], [26], and [27] respectively proposed secure and effective pairing-free CLPEKS schemes, but they are all single keyword searches.
Cryptography researchers place a high value on security. Next, let’s look at what researchers have done to improve the security of PEKS. The existing SCF-PEKS scheme is susceptible to keyword guessing attacks (KGA) [28] and file injection attacks (FIA) [29]. To avoid keyword guessing attacks and file injection attacks, Hwang et al. [30] embedded random keys in the keyword ciphertext of the PKSE scheme and claim that the scheme can resist the above attacks. However Yang [40] proved Hwang et al.’s SCF-PEKS scheme [30] is insecure under external online keyword attacks. The main reason for being vulnerable to external online keyword attacks is that opponents can generate legitimate ciphertext for the keyword. In addition to being attacked by external attackers, the PEKS scheme is also vulnerable to attacks from internal attackers (usually referring to malicious cloud servers). Jeong et al. [41] demonstrated that the PEKS framework is susceptible to offline keyword attacks (i.e., internal offline keyword attacks) by malicious data storage servers. Later, Shao and Yang [37] proposed a universal attack demonstrating the inability to construct an SCF-PEKS scheme to defend against malicious internal servers. They pointed out that because malicious servers can run keyword encryption and testing algorithms, SCF-PEKS is inherently vulnerable to offline keyword-guessing attacks from malicious insider servers.
In addition, a cloud server is a semi-honest but curious third party that may perform only a small portion of search operations and return a small amount of incorrect search results to save its computing and bandwidth resources. Therefore, the PEKS scheme should be equipped with a verification mechanism to ensure the correctness of search results without decrypting the ciphertext. Reference [31] proposed the first symmetric and verifiable encryption scheme for keyword search. Subsequently, many literature studies have investigated verifiable keyword searchable encryption schemes [32–35]. In reference [34], a verifiable conjunctive keyword search scheme (VCKSM) over mobile e-health cloud in shared multi-owner settings was proposed, and it was secure against keyword guessing attacks under the standard model; In reference [35], an identity-based certificateless verifiable conjunctive keyword searchable encryption scheme (VMKS) was constructed, which avoids certificate management or key escrow restrictions and achieves indistinguishability of ciphertext and unforgeability of signatures.
1.1. Our contribution
We construct a certificateless verifiable bilinear pair-free conjunctive keyword search encryption scheme (CLVPFCKS), and it has been proven under the standard model that it can resist keyword guessing attacks (KGA), file injection attacks (FIA), and choose keyword attacks (CKA). Specifically, the main contributions are as follows:
- Search results validation: The scheme allows the signature to be attached to each file to verify the accuracy of the search results.
- No bilinear pairing: The calculation of bilinear pairing needs more time, and the scheme’s efficiency will significantly improve without bilinear pairing.
- We prove that the new scheme can resist offline keyword guessing attacks, file injection attacks, and choose keyword attacks (CKA) under the standard model.
1.2. Organization
The following is the framework for the rest of this article. We summarize some related work in section 1. We discuss preparatory knowledge in section 2. We give the scheme’s construction and security analysis (including the security model and proof) in section 3. We show the details of the CLVPFCKS scheme in section 4. We discuss the security of the CLVPFCKS scheme in section 5. We analyze the effectiveness of CLVPFCKS in section 6. Finally, we summarize this paper in section 7.
2. Preliminaries
Let be a large prime, be a prime field, and the elliptic curve E over the field must satisfy the equation
Which and. All points on E and the infinite point O form a cyclic group. ECC (elliptic curve cryptosystem) has the following difficulties:
- Elliptic curve discrete logarithm problem (ECDLP): given , where P is the generator of the group, and Q is the element in . It is difficult to calculate the integer k such that , where .
- Elliptic curve Computational Diffie-Hellman problem (ECDCHP): for any given in , it is difficult to calculate , where .
- Elliptic curve Decisional Diffie-Hellman problem (ECDDDH): Given where unknown. The DDH (Decisional Diffie-Hellman) problem is to decide whether X equals or a random element in G.
3. The System Model and Attack Model of CLVPFCKS
3.1. System model
There exist five entities in the proposed CLVPFCKS scheme for KGC: multiple data owners (patient and his doctors), Cloud Service Provider (CSP), data user (other authorized doctors or healthcare center), and Private Audit Server (PAS), as shown in Figure 2.
KGC: It is a trusted third party, and it is responsible for generating system parameters and producing data owners, Cloud Service Providers (CSP), and data user’s partial private keys.
Multiple data owners: In reality, the cloud search system supports more shared scenarios of multiple data owners, especially in the electronic medical system. For example, one patient and several hospital staff (i.e., surgeons, physicians, etc.) share an electronic medical record jointly, and each staff member is responsible for the content of a specific part (i.e., block). If each block is an independent record, it will inevitably encounter multiple indexes, thus greatly expanding the computational and spatial overhead. Otherwise, the many data owners must have the same random elements, which is not feasible in practice. On the contrary, the scheme designed for shared multi-owner settings only requires a single index of the entire record, saving considerable time and space.
For each EHR jointly owned by the patient and its doctor, each data owner generates a signature on this record. All data users entrust user to establish an index based on the keywords of each EHR, and then the index and signature are sent to CSP. Note that the detailed algorithm for encrypting each EHR is beyond the discussion, and any public key encryption algorithm can be applied.
CSP: It is a semi-trusted entity. It has professional knowledge and can provide data storage and retrieval services for authorized cloud clients. After receiving a trapdoor from the data user, it returns the corresponding documents. But CSP is a semi-honest but curious third party, which many only perform a small part of the search operation and provide a small portion of the wrong search results to save its computing and bandwidth resources.
Data users: Data users obtain a partial private key from KGC generate the trapdoor of a keyword they wish to search, and then send it to the cloud server.
PAS: This fully trusted server is responsible for verifying the correctness of search results.
The CSP is assumed to be semi-honest but curious. It performs a fraction of search operations honestly but is interested in spying out the sensitive information valuable for the CSP. Furthermore, it may return false search results to save computing resources. On the other hand, the PAS is fully trusted and can guarantee the correctness of search results. Besides, the authorized data user can issue search queries without leaking valuable information to CSP.
3.2. Design Goals
We plan to achieve the following goals:
Multiple keyword search :The proposed scheme allows specific data users to send multiple keyword searches without increasing the trapdoor size and ciphertext search size, which improves the user search experience.
Search results validation: The scheme verifies the accuracy of search results by attaching a signature to each file.
Certificateless: The scheme is based on the certificateless cryptosystem to eliminate the limitations of certificate management and key escrow in existing searchable encryption schemes.
Pairing free: It takes more time to compute bilinear pairing. The efficiency will improve if it does not use bilinear pairing operations.
Free secure channel: It is necessary to eliminate the security channel in practice to reduce the costs of the system.
Supporting safe goals: We have demonstrated under the standard model that our scheme can resist keyword guessing attacks (KGA), file injection attacks (FIA), and chosen keyword attacks (CKA).
3.3. Solution Framework
Set integer k as security level, as EHR file and keyword set. Definition1 (Our proposed CLVPFCKS scheme) Our scheme is a tuple of six algorithms, as follows:
(1)SetUp():Given the security parameter k, KGC outputs the public parameters and the public/secret key pair for the traditional public key algorithm.
(2)KeyGen :For the data owner set O , data user set U and cloud server, KGC generates the public/secret key pairs {} , {} and {}, respectively .
a)Set-Secret-Value:After inputting the public parameters , this probabilistic algorithm outputs Data owners, Data users, and CSP’s Secret-Value.
b)Partial-Private-Key-Extract:The KGC executes this algorithm, which accepts the identity of the data owner, data user, and CSP, then uses them in combination with the master key to generate a partial private key for the data owner, data user, and CSP.
c)Set-private-Key:Set the full secret keys of the data owner, data user, and CSP.
d)Set-Public-Key:Set the full public keys of the data owner, data user, and CSP.
(3):Data owners first conduct this probabilistic algorithm to generate the ciphertext set C for the set F. Then data owners generate multiple signatures Sig and index set I for ciphertext C. Then he sends the tuple to CSP.
(4):Given the keyword , the data user runs this algorithm to output trapdoor .
(5):Using the trapdoor as an input, the CSP matches it with the index set I, then returns the relevant ciphertext and signature set to PAS.
(6):PAS runs this algorithm by initiating interaction with CSP to check the correctness of the search result . If passes the result validation, PAS will return it to the data user. Otherwise, it will abort the algorithm.
3.4. Security Model
To protect the security and privacy of the scheme, we must satisfy the following requirements:
(1)Keyword ciphertext indistinguishability: When encrypted data is stored in CSP, it will attach the corresponding keywords . Even if keyword ciphertext is captured during transmission, no adversary can obtain keywords embedded in the ciphertext.
(2)Indistinguishability of trapdoor:Any adversary shall not obtain any information from the trapdoor.
Our scheme proves that trapdoors are indistinguishable and the keywords ciphertext are indistinguishable in the standard model. They are defined as follows:
ciphertext indistinguishability against chosen keyword ciphertext attack: We will define the definition of ciphertext indistinguishability against chosen keyword and ciphertext attack (CKCA-CIND). There are two types of adversaries: external adversaries (receivers) and internal adversaries (servers). and represent these two adversaries, and their attack methods are as follows:
: doesn’t know the master key, but can replace any user’s public key.
: knows the master key, but cannot replace any user’s public key.
Call them the adversary of type-1 and the adversary of type-2. There are two games to discuss the security of CKCA-CIND.
Game I. simulates malicious users and B is the challenger. B and play this game together.
Setup:B running SetUp() program to get public parameters and the public/secret key pair .B sends the public key to and keeps the master private key . Then B sets the key pair of and CSP, i.e., and .B sends the public key and to , while and are unknown to .
Phase 1. executes the User-Public-Key query using date user’s identity first and then executes other queries using the identity . Set up lists to store the above queries and answers. All lists are initially empty. makes the queries to the challenger B as following:
(1)User-Public-key query:When inputs the identity , B outputs the user’s public key .
(2)Replace - Public - Key query: inputs ,B replaces with .
(3)Secret-Value query:When inputs the identity , B returns the secret value corresponding to the . If is replaced, B refuses to answer.
(4)Partial-Private-Key-Extract query:When enters the , if ( is the challenge identity), B fails and stops. Otherwise, B returns the corresponding Partial Private Key.
(5)Keyword Ciphertext Query: asks B for the ciphertext of any keyword W it cares about. B runs the algorithm to answer W’s ciphertext .
(6)Keyword Trapdoor Query: sends a keyword to B. B runs the algorithm to answer ’s trapdoor .
(7)Test Query: selects and sends the ciphertext and trapdoor to B. B executes the algorithm to return the test result of whether the ciphertext and the trapdoor match.
Challenge: submits a tuple to B, where and are challenging keywords not asked in the previous trapdoor and ciphertext query. If , B aborts. Otherwise, B picks randomly computes keyword trapdoor , and returns the challenge ciphertexts to .
Phase 2. can perform many queries like Phase 1, but cannot query the ciphertext and trapdoor of and .
Guess: outputs . wins if . Otherwise, it fails.
Game 2. simulates the malicious server, and B is a challenger. B and play this game together.
Setup:It differs from Setup of Game 1 only in the following steps. B send spublic key and public/secret key pair to , and are unknown to .
Phase 1.The steps are the same as phase 1 of Game 1, except for Secret Value and Partial Key query. The changes in them are as follows:
Secret-Value query :When enters the , if ( is the challenge identity), B fails and stops. Otherwise, B returns the secret value corresponding to .
Partial-Private-Key-Extract query: When inputs the identity , B returns the partial private key corresponding to the .If is replaced, B refuses to answer.
Phase 2 :Same as Phase 2 of Game 1.
Definition 1(Security of CKCA-CIND) : If the probability that any adversary will win the above two games in polynomial time is negligible, then we state that the CLVPFCKS scheme is CKCA-CIND safe.
Indistinguishability of trapdoor (IND-KGA):No adversary can obtain valuable information from trapdoors. A sufficient condition for ensuring security against offline key-guessing attacks is that the trapdoors are indistinguishable. In the following, we define the concept of indiscernibility of CLVPFCKS against keyword guessing attacks. Specifically, IND-KGA ensures that adversaries (servers or the receivers) cannot observe the connection between the trapdoors and any keywords.
Game 3. simulates malicious users and B is the challenger. B and play this game together.
Setup: B running SetUp() program to get public parameters and the public/secret key pair . B sends the public key PK to and keeps the master private key SK. Then B sets the key pair of date user and CSP, i.e., and .The challenger B sends the public key and to , while and are unknown to .
Phase 1. executes the User-Public-Key query using data owner’s identity first and then executes other queries using the identity . Set up lists to store the above queries and answers. All lists are initially empty. makes the queries to the challenger B as following:
(1)User-Public-key query:When inputs the identity , B outputs the user’s public key .
(2)Replace-Public-Key query: same as that in Game 1.
(3)Secret-Value query:same as that in Game 1.
(4)Partial-Private-Key-Extract query:When enters the , if ( is the challenge identity), B fails and stops. Otherwise, B returns the corresponding Partial Private Key.
(5)Keyword Ciphertext Query:same as that in Game 1.
(6)Keyword Trapdoor Query:same as that in Game 1.
(7)Test Query: same as that in Game 1.
Challenge : submits a tuple to B, where and are challenging keywords not asked in the previous trapdoor and ciphertext query. If , B aborts. Otherwise, B picks randomly computes keyword trapdoor , and returns the challenge ciphertexts to the adversary .
Phase 2. can perform many queries like Phase 1, but cannot query the ciphertext and trapdoor of and .
Guess: outputs . Adversary wins if . Otherwise, it fails.
Game 4. simulates the malicious server, and B is a challenger. B and play this game together.
Setup:It differs from Setup of Game 3 only in the following steps. B send spublic key and public/secret key pair to , and are unknown to .
Phase 1. The steps are the same as phase 1 of Game 3, except for Secret Value and Partial Key query. The changes in them are as follows:
Secret-Value query: When enters the , if ( is the challenge identity), B fails and stops. Otherwise, B returns the secret value corresponding to .
Partial-Private-Key-Extract query: same as that in Game 2.
Phase 2. Same as Phase 2 of Game 3.
Definition 2 (Security of IND-KGA):If the probability that any adversary will win the above two games in polynomial time is negligible, then we state that the CLVPFCKS scheme is IND-KGA safe.
4. the proposed CLVPFCKS
To better understand about our proposed scheme, we explain the pre-defined notations used throughout this paper in Table 1.

Table 1.
Notation descriptions
| Notations | DESCRIPTIONS |
| x | Master key |
| system public key | |
| Data Owner Collection | |
| identity set for data owner | |
| identity set for CSP | |
| identity set for data user | |
| Public/secret key pair for CSP | |
| Public/secret key pair for data owner | |
| Public/secret key pair for data user | |
| File set F | |
| ciphertext set | |
| identity set for F | |
| Collection of keywords | |
| Data owner signature for | |
| Data owners’ multi-signatures for | |
| F’s multi-signature | |
| Index of | |
| Index set for F | |
| Search keyword set | |
| The trapdoor of | |
| Search results | |
| Identity set for |
4.1. Specific construction of CLVPFCKS
This system uses traditional public key encryption algorithm to encrypt files, which we will not discuss. Therefore, the following algorithms focus on indexing and signature.
SetUp :Given a security parameter k, this deterministic algorithm outputs the global public parameters and PKG’s master private key (MSK). Given k, PKG performs in the following way:
(1)Chooses a k bits prime number q and determine the tuple , where the point P is the generator of .
(2) Chooses the master key and computes the system public key . Let .
(3) Selects five hash functions ,,, , .
(4) Let .
KeyGen:Each EHR has a fixed number of data owners , then PKG generates the public/secret key pairs for CSP, data owner set O and data user U, respectively.
(1)Set-Secret-Value: The Participant with selects an element and generates the corresponding public key .
(2))Extract-Partial-Private-Key: To get the partial private key, the user sends to the PKG and then the PKG executes the following steps.
(a)Taking the participant’s as input, KGC selects a random number and calculates .
(b)PKG computes . The partial private key of the participant with is . The participant with can verify his partial private key by checking whether the equation holds, where . If the above equation is true, then the private key will accepted.
(3)Set-Private-Key: The partial private key of the participant with takes the pair as his full private key.
(4)Set-Public-Key: The participant with takes as his full public key.
Enc
Step 1: Given the EHR set with corresponding identities , it will be encrypted as the ciphertext set through the traditional public key encryption algorithm. To generate the multi-signature on the encrypted file , each signer does the following:
(1) chooses a number and computes .
(2) broadcasts to other members of the group.
(3)computes , , .
(4)computes and .
(5) computes , generates a signature for , and then sends to the designated clerk .
(6)Upon receiving , computes and outputs the signature . Let , where .
Step 2: All users specify a user to encrypt files, for example, . runs this algorithm to generate the index of file set F. Given the keyword set W, builds an index for each file . The index for each is generated based on the keyword field , where m is a fixed integer. randomly selects and calculates to through public key encryption. computes and sends it to through public key encryption. computes and sends it to through public key encryption. ⋯, computes and sends it to through public key encryption. calculates . Calculates in the same way as .
Let , , Construct an m-degree polynomial by the following equation: . is the root of equation , where .
Then selects and computes , set , ,
- , and the index set is , where . Finally send I to CSP.
TrapGen :
The Data user calculates the value of as follows , , . Given the queried keywords set , the data user U first selects an elements and sets ,, where , . Finally, he sent to CSP.
test : After gaining the search token , the CSP first computes , and verifies whether Eq.(1) holds.
If Eq (1) holds, the CSP returns the relevant ciphertext set and its corresponding identity set to PAS. Otherwise, it returns ⊥. The specific test process is shown in the Algorithm 1.
Algorithm 1 Search over encrypted data
Input: Trapdoor , indexes I, ciphertexts C, secret key and public parameters .
Output: Search results and corresponding identity set or ⊥.
(1)
(2),.
(3)
(4)
(5) If Eq.(1) holds, CSP returns the ciphertext ; otherwise, it returns ⊥;
(6)end for
(7)CSP returns the relevant results and corresponding identity set or ⊥ to PAS.
Verify:After receiving the search results , CSP computes the proof information through Eq.(2) and sends it to PAS. Finally, PAS verifies whether Eq.(3) holds.
Algorithm 2 results verification
Input: Search results with corresponding identity set , public keys , signature and public parameters , where .
Output: "Accept" or "Reject"
()1;
(2);
(3), ;
(4)compute , ;
(5)compute ,
(6)Check
(7)If Eq.(3) holds, output "Accept" and send to data user; otherwise, output "Reject".
5. Security of scheme
In this section, we will analyze the security and correctness of this scheme.
5.1. Correctness
Theorem 1. Our CLVPFCKS scheme is computationally consistent.
Proof: For the correctness of Our CLVPFCKS scheme, we do two things. First, We show that CSP can correctly test whether the index of ciphertext matches the trapdoor when the keyword set , where is a set of keywords searched by a specific user and W is the keyword set of ciphertext. Secondly, we will show that if the search results pass the result verification mechanism, data users can guarantee the correctness of the search results.
In the test phase, CSP obtains the index and trapdoor . The CSP first computes
.
If , then are the root of the equation , where . Thus
Equation (1) holds so CSP can correctly test whether the index of ciphertext matches the trapdoor.
In the test phase, PAS obtains signature and ciphertext , computing
getting the proof information , and then continuing to calculate
.
- If , then
Where . So we have . Eq. (3) in program 2 holds. We can also make sure that the ciphertext can not modified.
5.2. Security
Lemma 1. Assuming the adversary can win Game 1, then an algorithm B can be constructed to solve the ECDDDH problem.
Proof: Suppose that the tuple is an example of ECDDDH problem. To determine whether , B will play the part of the challenger.
Set up : B runs the setup program to get public parameters , where master private key and the public key . Then B sends parameter to , and the master private key SK is kept secret. B selects , randomly and set
,
, ,
.
B sends the public key and to , but and are unknown to .
Phase 1: Executed the user’s public key query before other queries using the identity . Set up multiple lists to store the queries and answers. All lists are initially empty.
User public key query: B keeps a list of the tuple and upon receiving an identity , performs the following steps.
Case1. . B picks at randomly , setting , and adds the tuple to the list , Where ◊ represents a null value.
Case2. . B picks at randomly , setting , and adds the tuple to the list .
Replace-Public-Key query: B maintains a list of tuple . When inputs , B replaces with , and adds to the list .
Secret-Value query: When asks the secret value for , B finds in the list and returns .If is replaced, B refuses to answer.
Partial-Private-Key query: B establishes a list of tuple when asks the partial private key of . If , B fails and stops. Otherwise, B finds in the list , running the Extract-Partial-Private-Key algorithm generating . B output and adds to the list .
Keyword Ciphertext Query: When asks for the ciphertext, B operates the algorithm to generate ciphertext .
Keyword Trapdoor Query: When asks for the trapdoor, B operates the algorithm to generate trapdoor .
Test Query: gives keyword ciphertext and keyword trapdoor , and B compares them using Algorithm 1.
Challenge: submits a tuple , where and are challenging keywords not requested in the previous trapdoor and ciphertext query. If , B aborts. Otherwise , B calculates and picks randomly. B computes
.
Let , which can get by combining similar terms. Then B selects and computes . Set , . Thus, the corresponding ciphertext of is . B returns the challenge ciphertexts to the adversary .
Phase 2: can continue to execute various queries, but there is a limitation that is not allowed to query the keyword ciphertext or trapdoor of or .
Guess: returns .
Solve CDH problem: If , B returns 1, otherwise 0. If , then
Therefore, is a valid ciphertext. Suppose that the advantage of wins in the above game is . So
.
If , then is an invalid ciphertext. has no advantage in distinguishing from . Hence
.
Probability: Let , and be the number of the User public key query, Replace-Public-Key query, and Partial-Private-Key query, respectively. The two events are as follows:
: did not replace of ’s public key and query the partial-private-key for .
: .
It’s not hard to get the following results.
,
,
.
If win Game 1 with an advantage of , then B has a probability greater than to determine whether .
Lemma 2. Assuming the adversary can win Game 2, an algorithm B can constructed to solve the ECDDDH problem by exploiting the adversary’s ability.
Proof: Suppose that the tuple is an example of an ECDDDH problem. To determine whether , B will play the part of the challenger.
Set up: B runs the setup program to get public parameters , where master private key and the public key . B selects , randomly and set
,
,,
,
B sends the public parameters , the public key and the public/secret key pair to , while are unknown to .
Phase 1: Executed the user’s public key query before other queries using the identity . Set up multiple lists to store the queries and answers. All lists are initially empty.
User public key query: B maintains a list containing the tuple and takes the following actions when receiving an identity :
Case1. . B chooses a number at random, sets , and adds the tuple to the list , Where ◊ represents a null value.
Case2. . B chooses at random, sets , and adds the tuple to the list .
Replace-Public-Key query: same as that in Lemma 1
Secret-Value query: B established a list of tuple . When asks the secret value for . If , B fails and stops. Otherwise, B finds in list , returns .
Partial-Private-Key query: When asks the partial private key of , B finds in list , running the Extract-Partial-Private-Key algorithm and returning .If is replaced, B refuses to answer.
Keyword Ciphertext Query: same as that in Lemma 1.
Keyword Trapdoor Query: same as that in Lemma 1.
Test Query: same as that in Lemma 1.
Challenge: submits a tuple that meets the requirements of Game 2, where and are challenging keywords not asked in the previous trapdoor query and ciphertext query. If , B aborts. Otherwise , B computes , and picks randomly. B computes
.
Let , which can get by combining similar terms. Then select at random and compute . Set , , and thus ’s ciphertext is . B returns the challenge ciphertexts to the adversary .
Phase 2:The attacker can continue to execute various queries, but there is a limitation that the attacker is not allowed to query the keyword ciphertext or trap of or .
Guess: returns .
Solve the ECDDDH problem. If , B returns 1. Otherwise 0. If , then
Therefore, is a valid ciphertext. Suppose that the advantage of wins in the above game is , so
.
If , then is an invalid ciphertext. has no advantage in distinguishing from . Hence
.
Probability. Let , , be the number of User public key query, Replace-Public-Key query, and Secret-Value query, respectively. The two events are as follows:
: did not replace of ’s public key nor perform the Secret-Value query for .
: .
It’s not hard to get the following results.
,
,
.
If has an advantage to win Game, then B has a probability greater than to determine whether .
Theorem 2. Our CLVPFCKS scheme is CKCA-CIND secure in standard model if the ECDDDH problem is hard.
Proof: Theorem 2 holds from Lemma 1 and Lemma 2.
Lemma 3. Assuming the adversary can win Game 3, then an algorithm B can be constructed to solve the ECDDDH problem.
Proof: Suppose that the tuple is an example of ECDDDH problem. To determine whether , B will play the part of the challenger.
Set up: B runs the setup program to obtain the public parameters , where master private key ,, then randomly selects ,and set
, , ,
,
.
B sends the public key and to , but and are unknown to .
Phase 1: Executed the user’s public key query before other queries using the identity . Set up multiple lists to store the queries and answers. All lists are initially empty.
User public key query: B keeps a list of the tuple and upon receiving an identity , performs the following steps.
Case1. , B picks at randomly , setting , and adds the tuple to the list ,Where ◊ represents a null value.
Case2. , B picks at randomly , setting , and adds the tuple to the list .
Replace-Public-Key query: same as that in Lemma 1.
Secret-Value query:same as that in Lemma 1.
Partial-Private-Key query: B establishes a list of tuple when asks the partial private key of . If , B fails and stops. Otherwise, B finds in the list , running the Extract-Partial-Private-Key algorithm generating . B output and adds to the list .
Keyword Ciphertext Query: same as that in Lemma 1.
Keyword Trapdoor Query: same as that in Lemma 1.
Test Query: same as that in Lemma 1.
Challenge: submits a tuple , where and are challenging keywords not requested in the previous trapdoor and ciphertext query. If , B aborts. Otherwise,without losing generality, it is better to set as . B calculates . B picks randomly, and computes
B selects an elements and sets ,
, where . Finally, B sent to the adversary .
Phase 2: The attacker can continue to execute various queries, but there is a limitation that the attacker is not allowed to query the keyword ciphertext or trapdoor of or .
Guess: returns .
Solve CDH problem: If , B returns 1, otherwise 0. If , then
.
Therefore, is a valid ciphertext. Suppose that the advantage of wins in the above game is . So
.
If , then is an invalid ciphertext. has no advantage in distinguishing from . Hence
.
Probability: Let , and be the number of the User public key query, Replace-Public-Key query, and Partial-Private-Key query, respectively. The two events are as follows:
: did not replace of ’s public key and query the partial-private-key for .
: .
It’s not hard to get the following results.
,
,
.
If win Game 1 with an advantage of , then B has a probability greater than to determine whether .
Lemma 4. Assuming the adversary can win Game 4, then an algorithm B can be constructed to solve the ECDDDH problem.
Proof: Suppose that the tuple is an example of ECDDDH problem. To determine whether , B will play the part of the challenger.
Set up : B runs the setup program to obtain the public parameters , where master private key ,, then randomly selects , and set
, , ,
,
B sends the public parameters , the public key , and the public/secret key pair to , while are unknown to .
Phase 1: Executed the user’s public key query before other queries using the identity . Set up multiple lists to store the queries and answers. All lists are initially empty.
User public key query: user public key query: B keeps a list of the tuple and upon receiving an identity , performs the following steps.
Case1. , B picks at randomly , setting , and adds the tuple to the list , Where ◊ represents a null value. .
Case2. , B picks at randomly , setting , and adds the tuple to the list .
Replace-Public-Key query: same as that in Lemma 1.
Secret-Value query:B established a list of tuple . When asks the secret value for . If , B fails and stops. Otherwise, B finds in list , returns .
Partial-Private-Key query: same as that in Lemma 2.
Keyword Ciphertext Query: same as that in Lemma 1.
Keyword Trapdoor Query: same as that in Lemma 1.
Test Query: same as that in Lemma 1.
Challenge: submits a tuple , where and are challenging keywords not requested in the previous trapdoor and ciphertext query. If , B aborts. Otherwise, without losing generality, it is better to set as . B calculates . B picks randomly, and computes
B selects an elements and sets ,
, where . Finally, B sent to the adversary .
Phase 2: The attacker can continue to execute various queries, but there is a limitation that the attacker is not allowed to query the keyword ciphertext or trapdoor of or .
Guess: returns .
Solve CDH problem: If , B returns 1, otherwise 0. If , then
.
Therefore, is a valid ciphertext. Suppose that the advantage of wins in the above game is . So
.
If , then is an invalid ciphertext. has no advantage in distinguishing from . Hence
.
Probability: Let , and be the number of User public key query, Replace-Public-Key query, and Secret-Value query, respectively. The two events are as follows:
: did not replace of ’s public key and query the secret value for .
: .
It’s not hard to get the following results.
,
,
.
If win Game 4 with an advantage of , then B has a probability greater than to determine whether .
Theorem 3. Our CLVPFCKS scheme is IND-KGA safe in the standard model if the ECDDDH problem is hard. Proof: Theorem 3 holds from Lemma 3 and Lemma 4.
Theorem 4. Under the ECDLP assumption, it is not computationally feasible for the CSP to forge valid proof information through the result verification mechanism.
Proof: The malicious CSP can’t forge a valid multi-signature on each returned record and pass the verification. Since it does not have the key of multiple data owners, it is computationally infeasible to forge a valid multi-signature. Therefore, the malicious CSP can only win the next security game by directly generating valid proof information according to the wrong search result instead of wining the next security game by forging multiple signatures. But after the following analysis, this is also impossible.
Assume that the correct ciphertext and its identity is and , where . The malicious CSP may forge wrong proof information on false search results , where
If the forged proof information can successfully pass the result verification mechanism, the malicious CSP will win the security game; Otherwise, it will fail. Suppose a malicious CSP wins the game. We then know that
where . The proof information of correct ciphertext C is , where
The signature of the correct ciphertext can pass the verification mechanism, so we have
Subtract Formula (4) from Formula (5) to get
Because is not equal to , so or . Set , , then or . Suppose is not zero, then . If the probability of is , then the probability that we can break the ECDLP problem is , where q is the length of . This means that if the malicious CSP can pass the verification, we can break the ECDLP problem.
6. Performance analysis
In this section, we compare our scheme with other certificateless or verifiable search schemes in terms of computational complexity, storage overhead and security.
First, let’s talk about security. Table 2 compares the security of the current scheme with other schemes. The CKCA-CIND, the IND-KGA, the insider KGA, the FIA, the SCF, and the VER are used to measure the scheme’s security. The CKCA-CIND means that the scheme is in differentiability of ciphertext for selected keyword ciphertext attacks, the IND-KGA means the indistinguishability of indiscernibility of trapdoors, the insider-KGA denotes that the scheme is secure against keyword-guessing attacks launched by malicious server, the FIA denotes that the scheme is resistant to file injection attack, the SCF means that the scheme has no secure channel, and the VER indicates that the scheme can prevent malicious CSP from returning wrong search results.
Table 2.
COMPARISON OF SAFETY
| scheme | CKCA-CIND | IND-KGA | insider-KGA | FIA | SCF | VER |
| VCKSM[18] | No proof | yes | no | no | yes | yes |
| VMKS[46] | yes | yes | No proof | No proof | yes | yes |
| VMKDO[33] | yes | yes | no | no | yes | yes |
| VCSE[46] | yes | No proof | no | no | yes | yes |
| CLPAEKS[12] | No proof | No proof | yes | yes | yes | No proof |
| CL-dPAEKS[11] | No proof | No proof | yes | yes | yes | No proof |
| our | yes | yes | yes | yes | yes | yes |
It is worth noting that no solution can simultaneously achieve result validation, conjunctive keyword search, and certificateless and bilinear pairings, as shown in Table 2. Our proposed solution can simultaneously perform four functions and is proven secure under the standard model.
Next, we compare the computational complexity. To compare the computational complexity, we use the operation time of He et al.’s scheme[47] as the benchmark. He et al. tested the time required for the relevant operations in the experimental environment of Samsung Galaxy S5 based on the Android 4.4.2 operating system, quad-core 2.45G processor, and 2G byte memory. Table 4 shows the exact running time and symbols of the various operations. The mapping is a bilinear pair where is an additive group of singular elliptic curves of order p defined on a finite field . The lengths of p and q are 512 bits and 160 bits, respectively. G is an additive group of non-sigular elliptic curve of order q defined on the prime finite field . The length of p and q is 160.
Table 3.
Symbol definition
| symbols | Definition |
| Running time required for a bilinear pairing operation, | |
| Running time required for a hash-to-operation, | |
| Running time required for a scalar multiplication operation in | |
| Running time required for an exponentiation operation in | |
| Running time required for a scalar multiplication operation in | |
| u | Number of data users |
| d | Number of data owners |
| m | Number of keywords in ciphertext |
| n | Number of ciphertext |
| s | Number of search keywords |
Table 4 shows the comparison results of the running time of the verifiable conjunctive keyword search encryption scheme. To be more intuitive and specific, we taking n=1000, m=100, d=100, u=50, s=50. Table 5 shows the calculation time of the three schemes. Except for the search algorithm, our scheme takes less time than the other two schemes, especially for the verification algorithm. Therefore, our scheme is the most efficient.
Table 4.
Comparison of running time of various schemes
| scheme | keyGen | Enc | Trap | search | verify |
| VCKSM[18] | [2nd + n(m + 2)] | ||||
| VMKS[46] | |||||
| our |
Table 5.
Comparison of running time of various schemes
| scheme | keyGen(ms) | Enc(ms) | Trap(ms) | search(ms) | verify(ms) | Total |
| VCKSM[18] | 2024.155 | 4151817 | 1380.715 | 3305426.428 | 3098.481 | 7463746.779 |
| VMKS[46] | 8043 | 1382126 | 737.275 | 130.852 | 2474.349 | 1393511.476 |
| our | 683.675 | 680340 | 353.51 | 336838.335 | 6.67 | 1018222.19 |
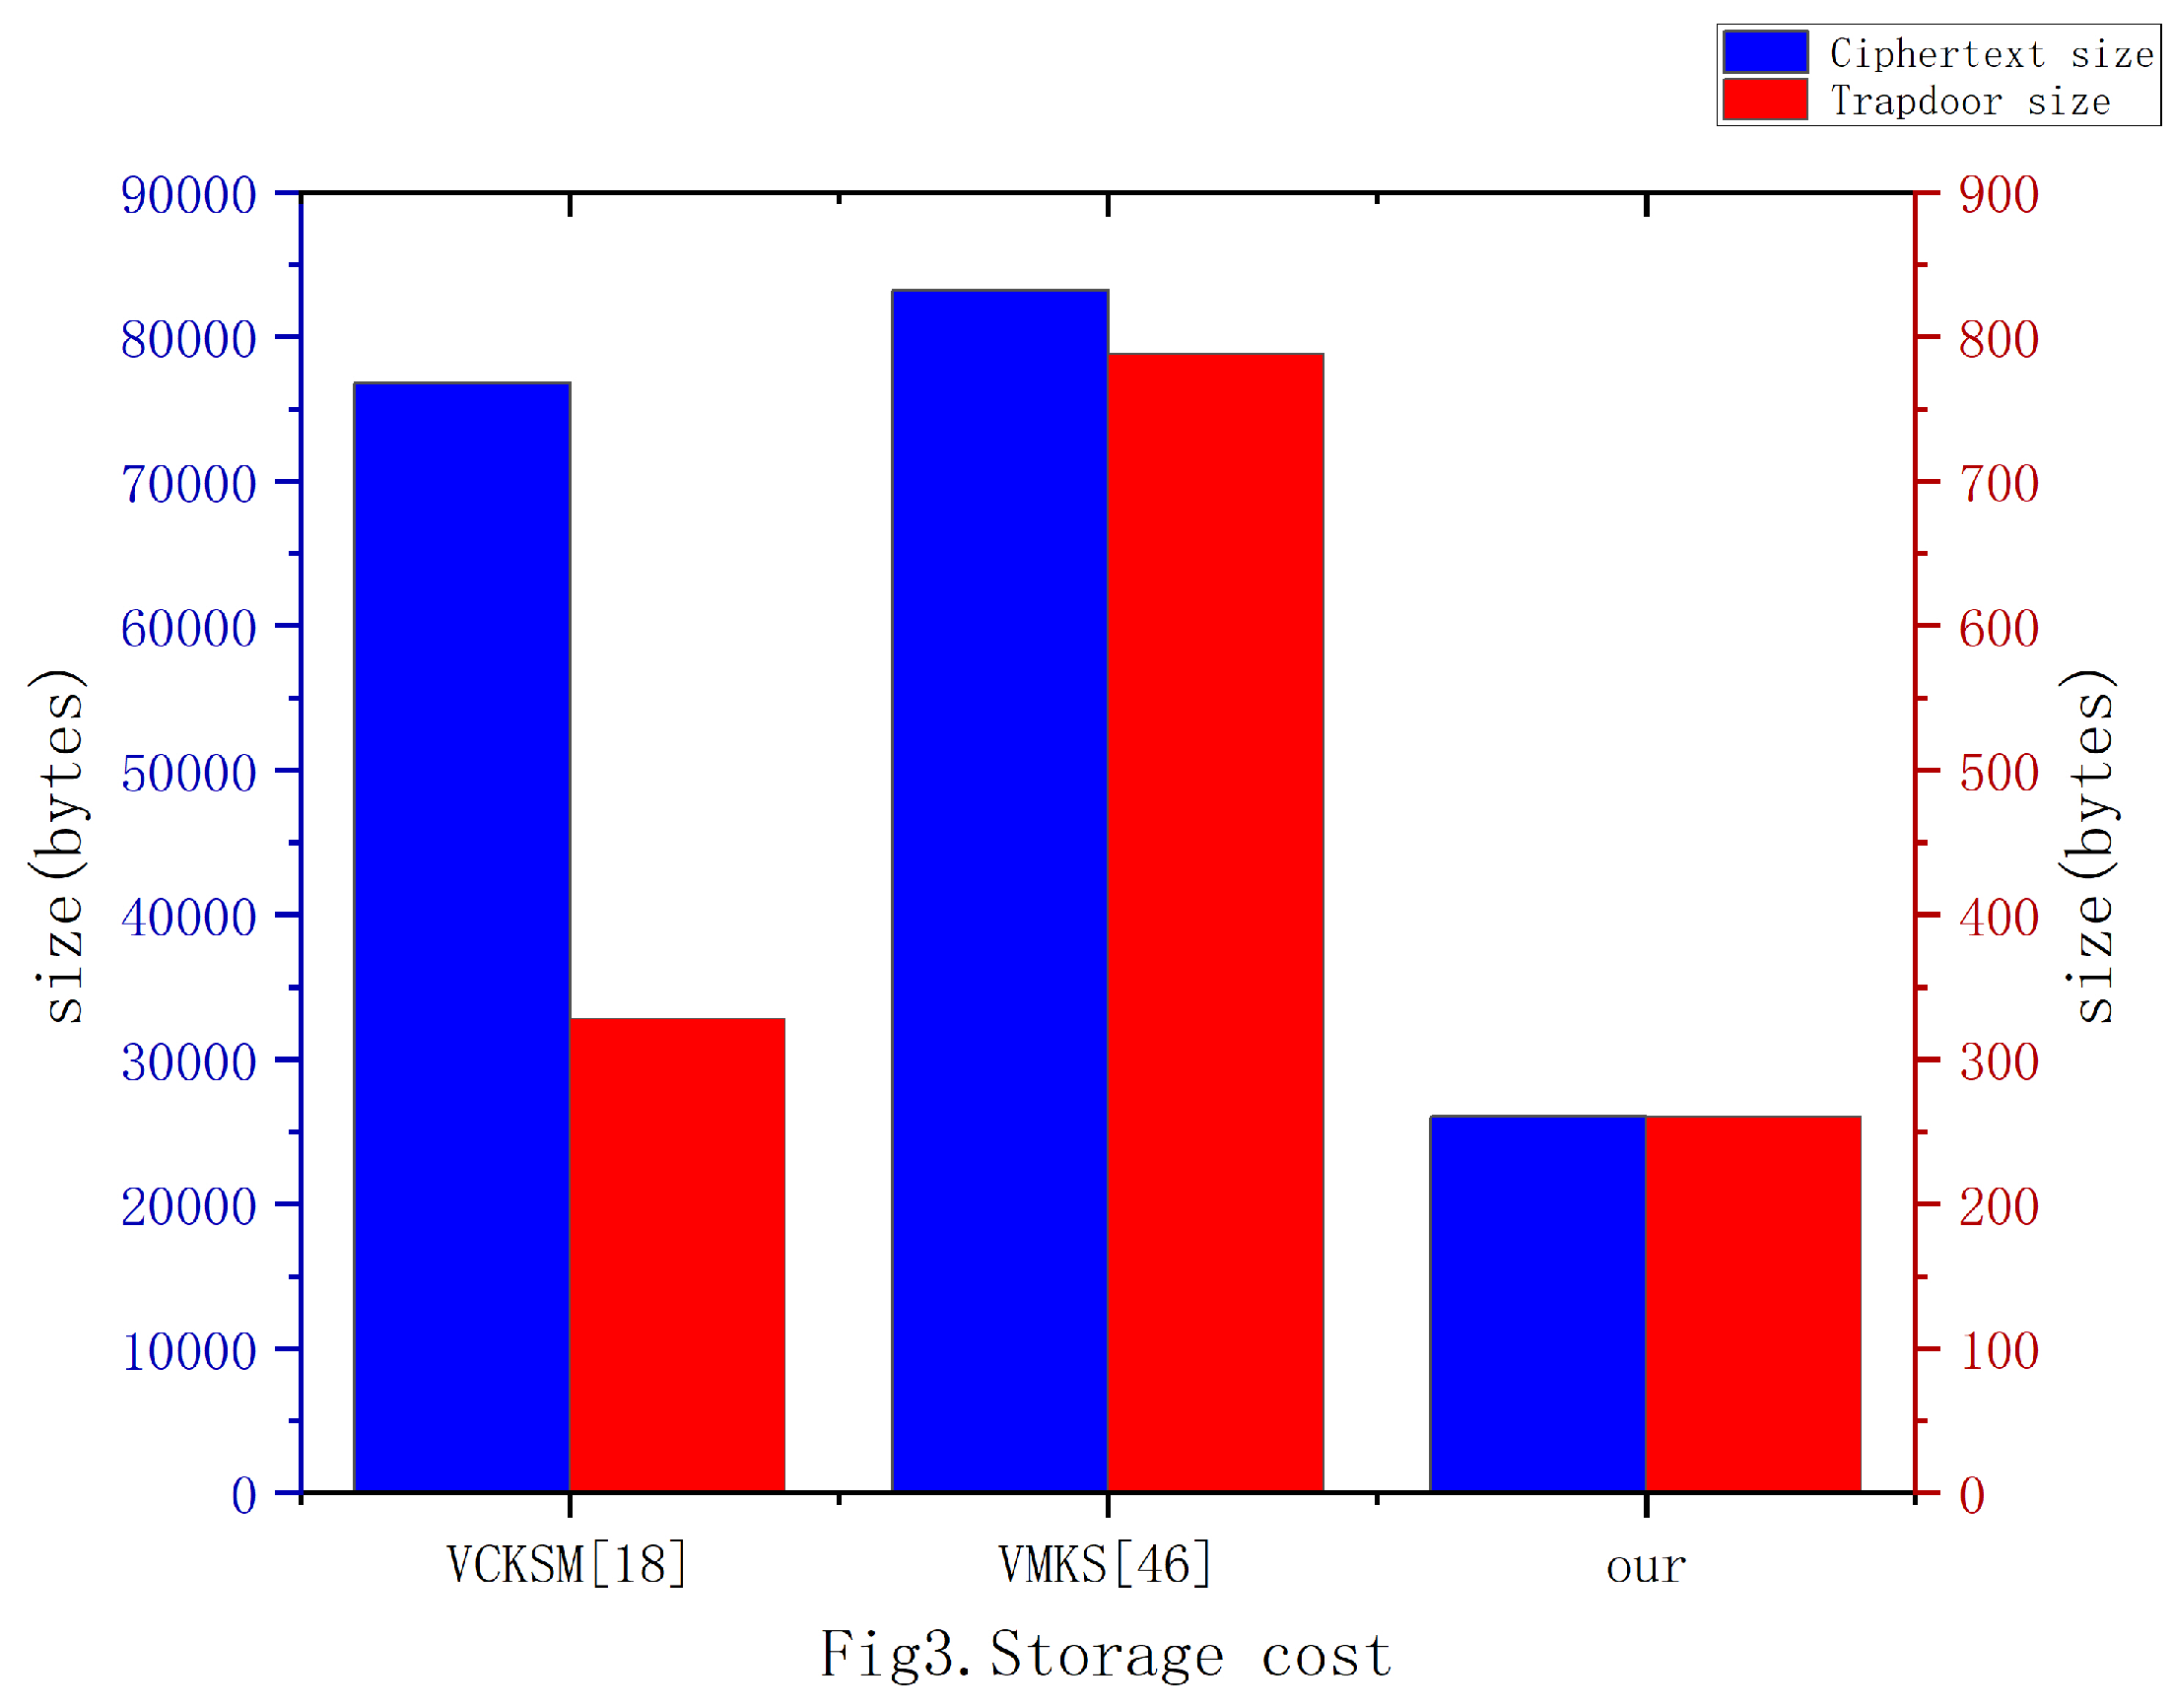
Let , , and denote the size of an element in , , G and , respectively. For more intuitive comparison of communication costs. Table 6 uses n=100, m=10 and s=10. As shown in Figure 3, our solution has the lowest storage cost.
Table 6.
Communication Comparison Of Various Schemes
| scheme | Ciphertext size(bytes) | Trapdoor size(bytes) |
| VCKSM[18] | ||
| VMKS[46] | ||
| our |
As stated in the summary, our scheme is more efficient than others in computing and communication costs. And it is also the best in security.
7. Conclusion
Searchable encryption is an essential technology for medical Internet of Things. We have constructed a certificateless verifiable bilinear pair-free conjunctive keyword search encryption scheme (CLVPFCKS) for the Internet of Medical. The performance analysis shows that the CLVPFCKS scheme proposed in this paper performs better than the verifiable conjunctive keyword searchable encryption scheme using bilinear pairing. We prove the new system can resist keyword guessing attacks, choose keyword attacks (CKA), and file injection attacks under the standard model.
References
- L. AtzoriA. Iera and G. Morabito, "The Internet of Things: A survey," Comput. Netw., vol. 54, no. 15, pp. 2787-2805, 2010. [CrossRef]
- A. Zanella, N. Bui, A. Castellani, L. Vangelista and M. Zorzi, "Internet of Things for Smart Cities," Ieee Internet of Things Journal, vol. 1, no. 1, pp. 22-32, 2014. [CrossRef]
- P. Bellavista, G. Cardone, A. Corradi and L. Foschini, "Convergence of MANET and WSN in IoT Urban Scenarios," Ieee Sens. J., vol. 13, no. 10, pp. 3558-3567, 2013. [CrossRef]
- V. Jagadeeswari, V. Subramaniyaswamy, R. Logesh and V. Vijayakumar, "A study on medical Internet of Things and Big Data in personalized healthcare system," Health Information Science and Systems, vol. 6, no. 1, 2018. [CrossRef]
- D.J. He, R. Ye, S. Chan, M. Guizani and Y.P. Xu, "Privacy in the Internet of Things for Smart Healthcare," Ieee Commun. Mag., vol. 56, no. 4, pp. 38-44, 2018. [CrossRef]
- Y.Y. ChenJ.C. Lu and J.K. Jan, "A Secure EHR System Based on Hybrid Clouds," J. Med. Syst., vol. 36, no. 5, pp. 3375-3384, 2012. [CrossRef]
- D.X. SongD. Wagner and A. Perrig, Practical Techniques for Searches on Encrypted Data, Proc. IEEE Symposium on Security & Privacy, 2002, pp. 44-55.
- D. Boneh, G.D. Crescenzo, R. Ostrovsky and G. Persiano, "Public Key Encryption with Keyword Search," Eurocrypt 2004, pp. 506-522, 2004. [CrossRef]
- J. BaekR. Safiavinaini and W. Susilo, Public Key Encryption with Keyword Search Revisited, Proc. International Conference on Computational Science and Its Applications (ICCSA 2008), 2008, pp. 1249-1259. [CrossRef]
- H.S. Rhee, J.H. Park, W. Susilo and D.H. Lee, Improved searchable public key encryption with designated tester, Proc. International Symposium on Information, 2009, pp. 376. [CrossRef]
- L. Wu, Y. Zhang, M. Ma, N. Kumar and D. He, "Certificateless searchable public key authenticated encryption with designated tester for cloud-assisted medical Internet of Things," Ann. Telecommun., vol. 74, no. 7-8, pp. 423-434, 2019. [CrossRef]
- D. He, M. Ma, S. Zeadall, N. Kumar and K. Liang, "Certificateless Public Key Authenticated Encryption with Keyword Search for Industrial Internet of Things," Ieee T. Ind. Inform., pp. 1, 2017. [CrossRef]
- M.M. A, D.H.B. C, M.K.K. D and J.C. A, "Certificateless searchable public key encryption scheme for mobile healthcare system," Comput. Electr. Eng., vol. 65, pp. 413-424, 2018. [CrossRef]
- M. Ma, D. He, S. Fan and D. Feng, "Certificateless searchable public key encryption scheme secure against keyword guessing attacks for smart healthcare," Journal of Information Security and Applications, vol. 50, 2020. [CrossRef]
- Y. Lu and J. Li, "Constructing pairing-free certificateless public key encryption with keyword search," Frontiers of Information Technology & Electronic Engineering, vol. 20, no. 8, pp. 1049-1060, 2019. [CrossRef]
- P. GolleJ. Stadon and B. Waters, Secure conjunctive keyword search over encrypted data,3089, M. Jakobsson, et al., eds., 2004, pp. 31-45. [CrossRef]
- Y.H. Hwang and P.J. Lee, Public key encryption with conjunctive keyword search and its extension to a multi-user system, Book Public key encryption with conjunctive keyword search and its extension to a multi-user system, Series Public key encryption with conjunctive keyword search and its extension to a multi-user system 4575,ed., Editor ed., 2007, pp. 2. [CrossRef]
- Y.B. Miao, et al., "VCKSM: Verifiable conjunctive keyword search over mobile e-health cloud in shared multi-owner settings," Pervasive Mob. Comput., vol. 40, pp. 205-219, 2017. [CrossRef]
- Y. Yang and M.D. Ma, "Conjunctive Keyword Search With Designated Tester and Timing Enabled Proxy Re-Encryption Function for E-Health Clouds," Ieee T. Inf. Foren. Sec., vol. 11, no. 4, pp. 746-759, 2016. [CrossRef]
- S.H. Heng and K. Kurosawa, k-resilient identity-based encryption in the standard model,2964, T. Okamoto, ed., 2004, pp. 67-80. [CrossRef]
- D. Khader, Public key encryption with keyword search based on K-resilient IBE,3982, M. Gavrilova, et al., eds., 2006, pp. 298-308.
- H.M. YangC.X. Xu and H.T. Zhao, An Efficient Public Key Encryption with Keyword Scheme Not Using Pairing, Proc. First International Conference on Instrumentation, 2011.
- T.F. Vallent and H. Kim, A Pairing-Free Public Key Encryption with Keyword Searching for Cloud Storage Services, Book A Pairing-Free Public Key Encryption with Keyword Searching for Cloud Storage Services, Series A Pairing-Free Public Key Encryption with Keyword Searching for Cloud Storage Services 135,ed., Editor ed., 2014, pp. 70.
- N.B. YangS.M. Xu and Z. Quan, "An Efficient Public Key Searchable Encryption Scheme for Mobile Smart Terminal," Ieee Access, vol. 8, pp. 77940-77950, 2020. [CrossRef]
- M. Ma, M. Luo, S. Fan and D. Feng, "An Efficient Pairing-Free Certificateless Searchable Public Key Encryption for Cloud-Based IIoT," Wirel. Commun. Mob. Com., vol. 2020, 2020. [CrossRef]
- M.R. Senouci, I. Benkhaddra, A. Senouci and F.G. Li, "A provably secure free-pairing certificateless searchable encryption scheme," Telecommun. Syst., vol. 80, no. 3, pp. 383-395, 2022. [CrossRef]
- Z.Y. Hu, L.Z. Deng, Y.Y. Wu, H.Y. Shi and Y. Gao, "Secure and Efficient Certificateless Searchable Authenticated Encryption Scheme Without Random Oracle for Industrial Internet of Things," Ieee Syst. J., vol. 17, no. 1, pp. 1304-1315, 2023. [CrossRef]
- J.W. Byun, H.S. Rhee, H.A. Park and D.H. Lee, Off-line keyword guessing attacks on recent keyword search schemes over encrypted data,4165, W. Jonker and M. Petkovic, eds., 2006, pp. 75-83.
- Y. LuG. Wang and J.G. Li, "Keyword guessing attacks on a public key encryption with keyword search scheme without random oracle and its improvement," Inform. Sciences, vol. 479, pp. 270-276, 2019. [CrossRef]
- M.S. HwangS.T. Hsu and C.C. Lee, "A New Public Key Encryption with Conjunctive Field Keyword Search Scheme," Inf. Technol. Control, vol. 43, no. 3, pp. 277-288, 2014. [CrossRef]
- Q. Chai and G. Gong, Verifiable symmetric searchable encryption for semi-honest-but-curious cloud servers, Proc. IEEE International Conference on Communications, 2012.
- W. Sun, X. Liu, W. Lou, Y.T. Hou and H. Li, Catch You If You Lie to Me: Efficient Verifiable Conjunctive Keyword Search over Large Dynamic Encrypted Cloud Data, Proc. 34th IEEE Conference on Computer Communications (INFOCOM), 2015.
- Y. Miao, J. Ma, X. Liu, Z. Liu and F. Wei, "VMKDO: Verifiable multi-keyword search over encrypted cloud data for dynamic data-owner," Peer Peer Netw. Appl., vol. 11, no. 2, pp. 287-297, 2018. [CrossRef]
- Y. Miao, J. Weng, X. Liu, K. Raymond Choo, Z. Liu and H. Li, "Enabling verifiable multiple keywords search over encrypted cloud data," Inform. Sciences, vol. 465, pp. 21-37, 2018. [CrossRef]
- L. Fang, W. Susilo, C. Ge and J. Wang, "Public key encryption with keyword search secure against keyword guessing attacks without random oracle," Inform. Sciences, vol. 238, pp. 221-241, 2013. [CrossRef]
- Z.Y. Shao and B. Yang, "On security against the server in designated tester public key encryption with keyword search," Inform. Process. Lett., vol. 115, no. 12, pp. 957-961, 2015. [CrossRef]
- C. Hu and P. Liu, "An Enhanced Searchable Public Key Encryption Scheme with a Designated Tester and Its Extensions," Journal of Computers, vol. 7, no. 3, 2012. [CrossRef]
- H.S. Rhee, J.H. Park, W. Susilo and D.H. Lee, "Trapdoor security in a searchable public-key encryption scheme with a designated tester," J. Syst. Software, vol. 83, no. 5, pp. 763-771, 2010. [CrossRef]
- Y. LuG. Wang and J. Li, "On Security of a Secure Channel Free Public Key Encryption with Conjunctive Field Keyword Search Scheme," Inf. Technol. Control, vol. 47, no. 1, pp. 56-62, 2018. [CrossRef]
- I.R. Jeong, J.O. Kwon, D. Hong and D.H. Lee, "Constructing PEKS schemes secure against keyword guessing attacks is possible?" Computer Communications, vol. 32, no. 2, pp. 394-396, 2009. [CrossRef]
- P. Xu, H. Jin, Q. Wu and W. Wang, "Public-Key Encryption with Fuzzy Keyword Search: A Provably Secure Scheme under Keyword Guessing Attack," Ieee T. Comput., vol. 62, no. 11, pp. 2266-2277, 2013. [CrossRef]
- X.J. Lin, L. Sun, H.P. Qu and D.X. Liu, "On the Security of Secure Server-Designation Public Key Encryption with Keyword Search," Comput. J., vol. 61, no. 12, pp. 1791-1793, 2018. [CrossRef]
- Q. Huang and H.B. Li, "An efficient public-key searchable encryption scheme secure against inside keyword guessing attacks," Inform. Sciences, vol. 403, pp. 1-14, 2017. [CrossRef]
- L. Wu, B. Chen, S. Zeadally and D. He, "An efficient and secure searchable public key encryption scheme with privacy protection for cloud storage," Soft Comput., vol. 22, no. 23, pp. 7685-7696, 2018. [CrossRef]
- S.S. Al-Riyami and K.G. Paterson, Certificateless public key cryptography,2894, C. S. Laih, ed., 2003, pp. 452-473.
- Y.M.J.W. Miao, "VCSE: Verifiable conjunctive keywords search over encrypted data without secure-channel," Peer-to-Peer Netw, pp. 995-1007, 2017.
- D.B. He, H.Q. Wang, L.N. Wang, J. Shen and X.Z. Yang, "Efficient certificateless anonymous multi-receiver encryption scheme for mobile devices," Soft Comput., vol. 21, no. 22, pp. 6801-6810, 2017. [CrossRef]
Figure 1.
Architecture of IoMT.
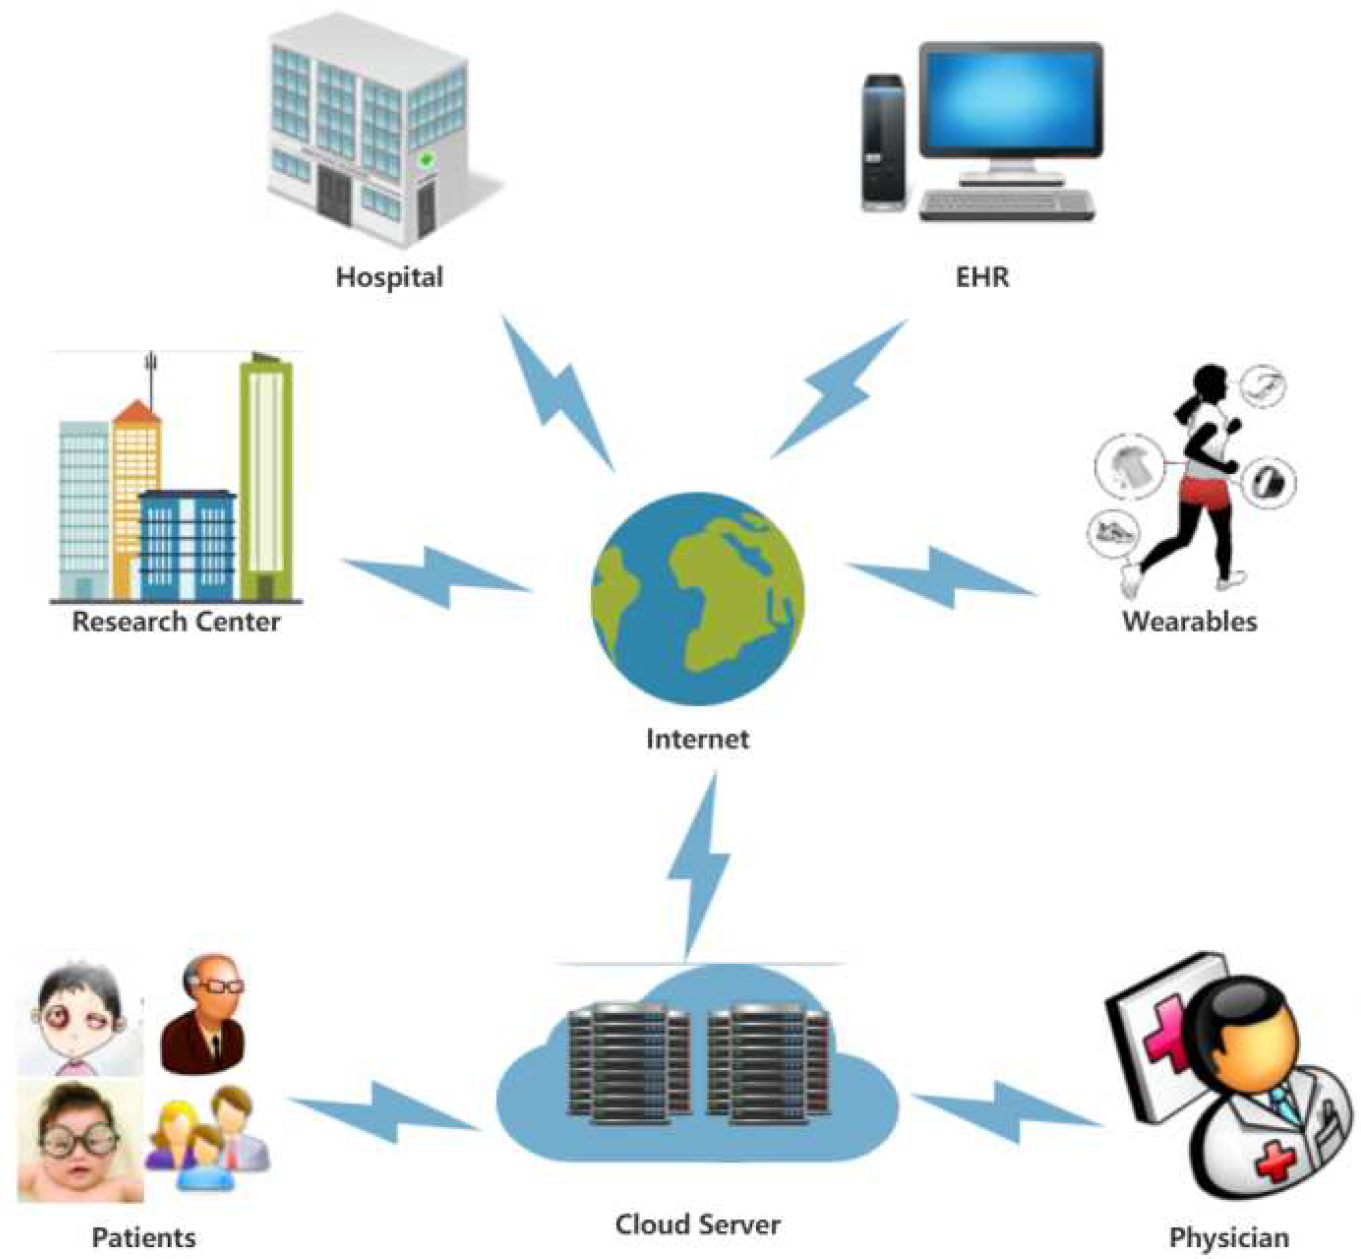
Figure 2.
System model of CLVPFCKS
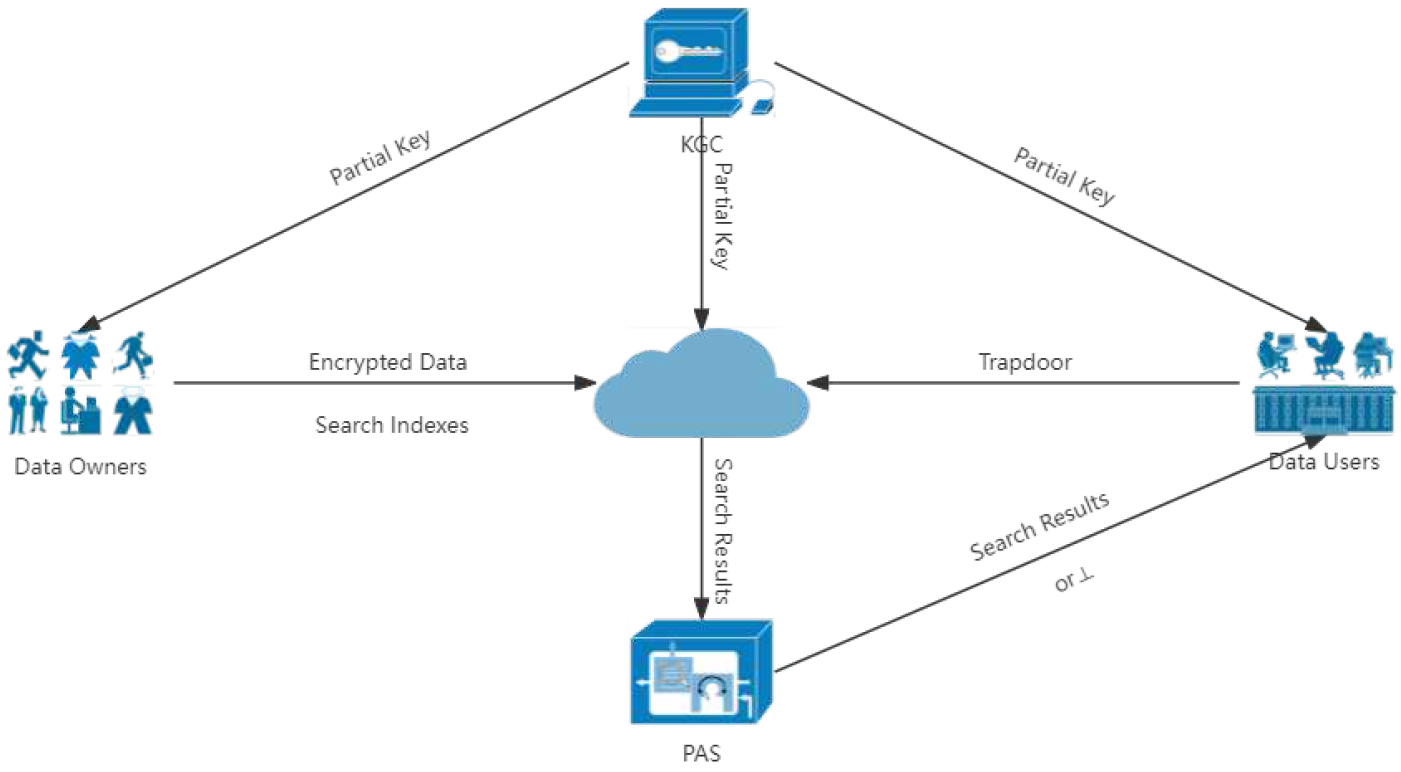
Figure 3.
System model of CLVPFCKS
Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2024 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (http://creativecommons.org/licenses/by/4.0/).
Copyright: This open access article is published under a Creative Commons CC BY 4.0 license, which permit the free download, distribution, and reuse, provided that the author and preprint are cited in any reuse.