
Submitted:
19 November 2026
Posted:
20 November 2026
You are already at the latest version
Abstract
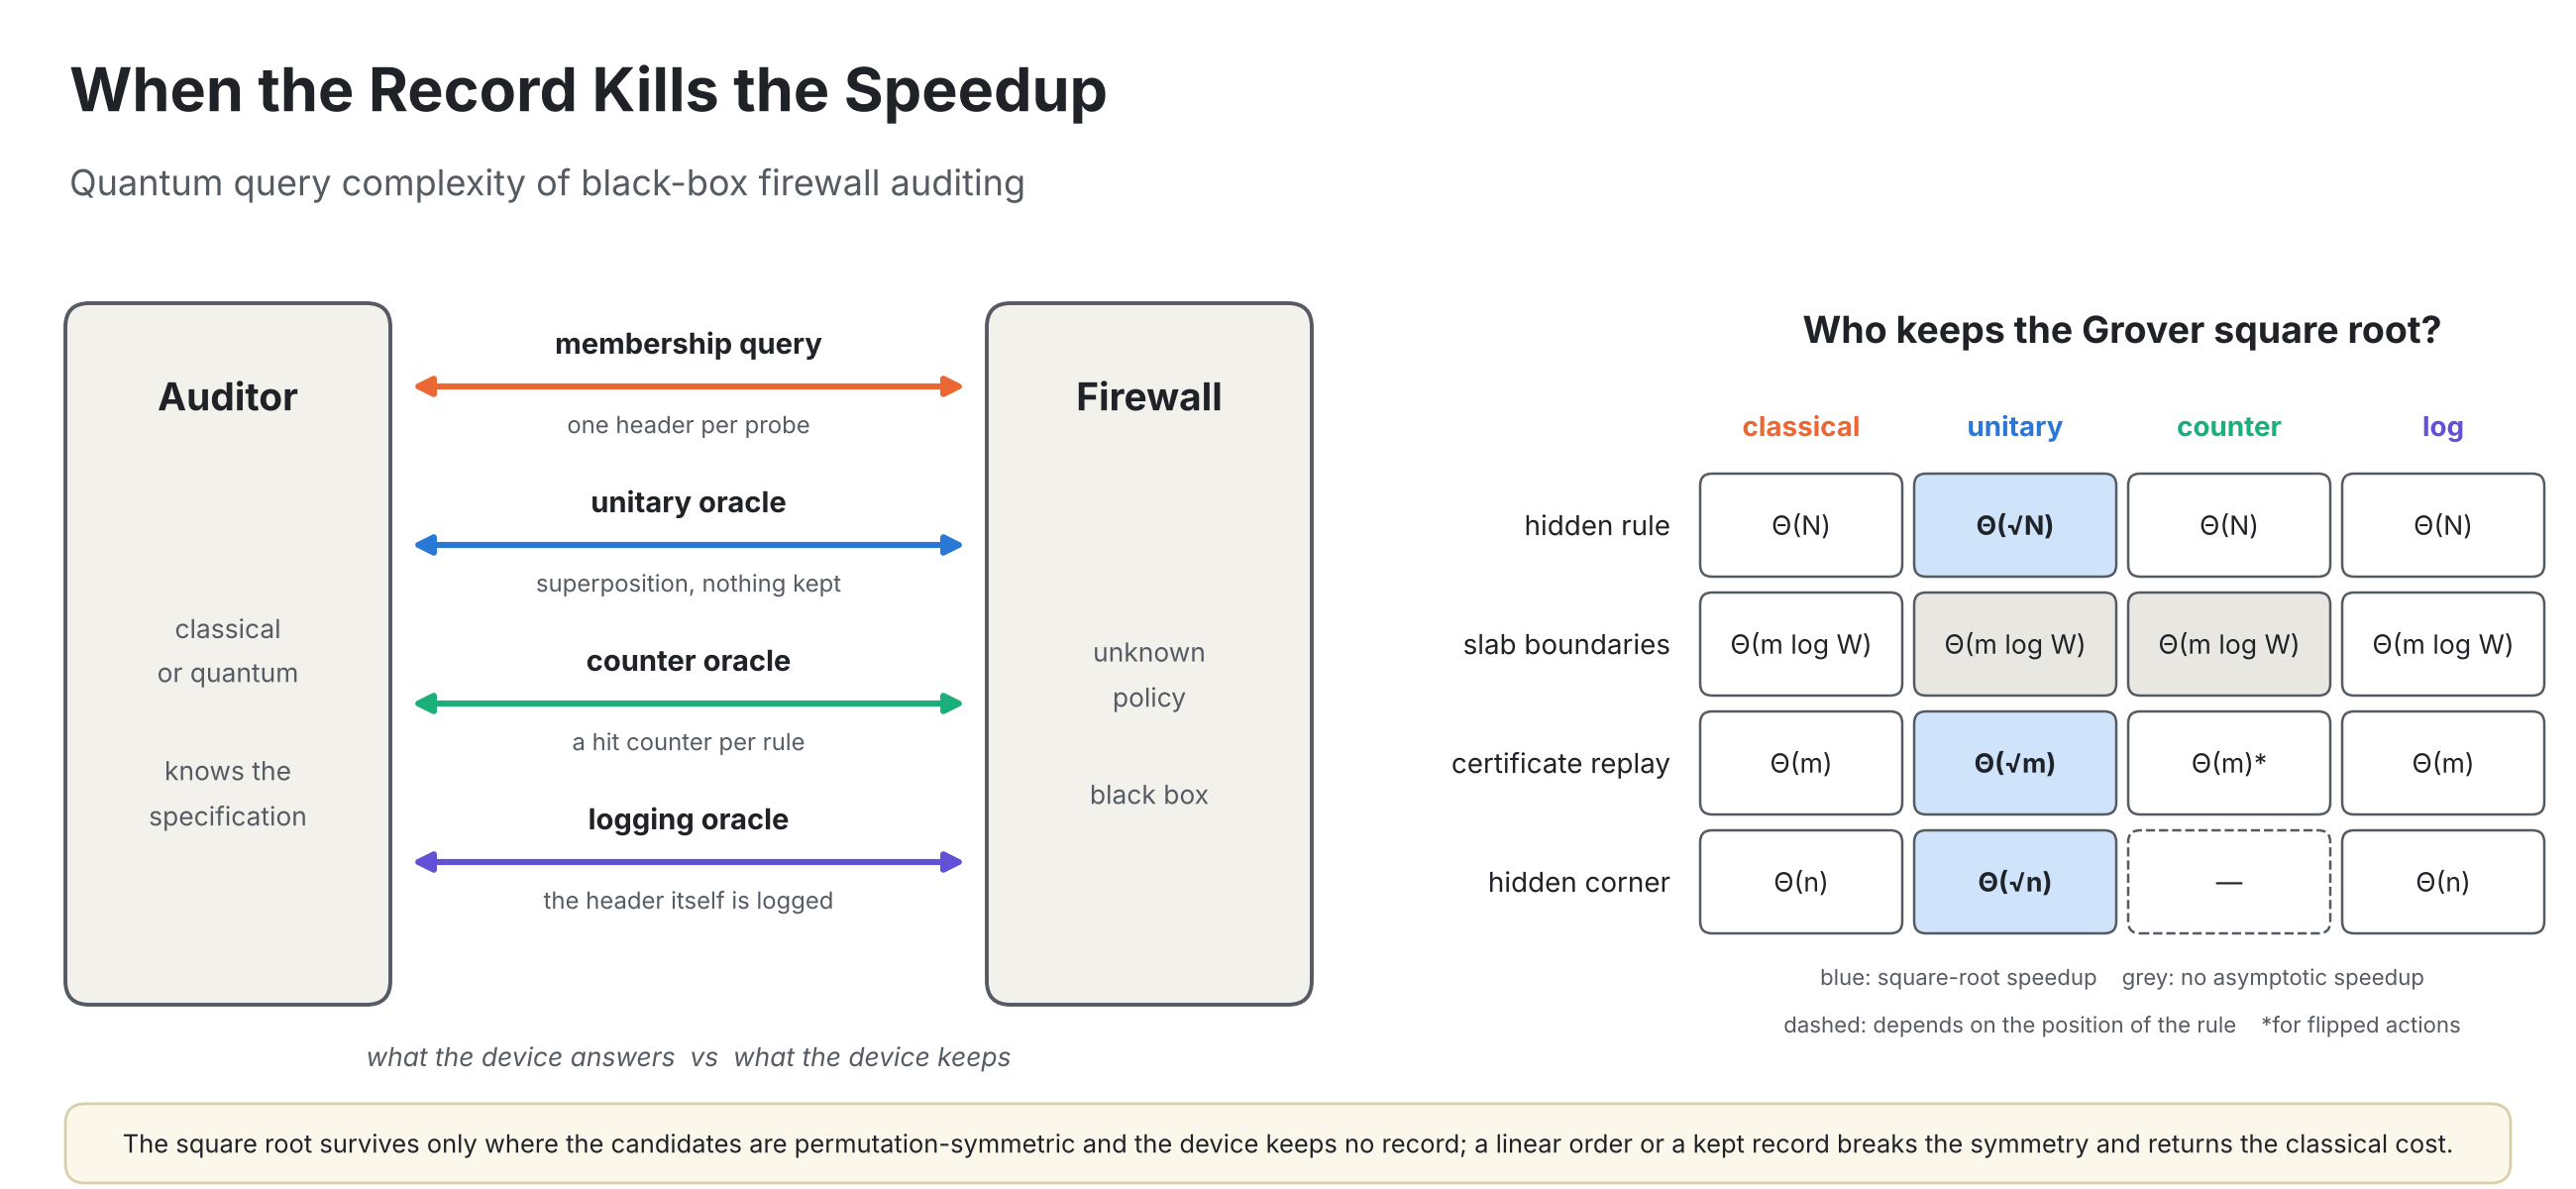
Black-box auditing of a firewall asks how many probe packets are needed to decide, from accept/deny answers, whether a device implements its policy. Classically, a hidden rule in a header space of N = 2104 headers forces N − 1 probes, whereas structured (tree-rule and disjoint listed-rule) policies are learned with a number of probes linear in the number of rules. We determine what changes for a quantum auditor, with Grover search and the adversary method. First, what the firewall records matters. A per-packet log makes every auditing task classical, and a per-rule hit counter restores the classical cost of finding a hidden rule and of replaying a certificate. Second, given a witness, structure admits no asymptotic speedup in localisation: finding the m boundaries of a slab family of tree-rule policies needs Ω(mlogW) queries for fields of width W, leaving only a constant factor. Third, for overlapping rule lists, re-localising one rule hidden behind an antichain of n candidate corners costs Ω(n) classically and \( \mathit{\Theta}(\sqrt{n})\ \)quantumly, against O(logW) for a tree boundary. For candidate families with a 2-transitive symmetry, the adversary bound depends only on how a probe separates the candidates; this explains where the Grover square root survives. Simulations agree with the bounds.
Keywords:
firewall auditing
; black-box verification
; quantum query complexity
; Grover search
; adversary method
; direct-sum theorem
; tree-rule firewall
; hit counter
; decoherence
; permutation symmetry
; symmetry breaking
Copyright: This open access article is published under a Creative Commons CC BY 4.0 license, which permit the free download, distribution, and reuse, provided that the author and preprint are cited in any reuse.