

Submitted:
05 October 2026
Posted:
09 October 2026
You are already at the latest version
Abstract
This paper investigates whether JA4+ fingerprint decomposition improves passive identification of Internet of Things (IoT) devices in encrypted network environments, without incorporating payload inspection or active probing techniques. As TLS encryption and privacy-preserving mechanisms such as Encrypted Client Hello reduce the visibility of application-layer metadata, traditional payload- and domain-based identification techniques become less effective. JA4+ fingerprints provide an alternative approach by extracting observable characteristics from TLS handshakes, certificates, and transport-layer metadata without requiring traffic decryption. The proposed methodology evaluates different JA4+ fingerprint combinations for IoT device identification using traffic traces from the CICIoT2023 dataset, with additional validation on the UNSW-IoTraffic dataset. Traffic traces were processed with Zeek to extract the JA4+ fingerprint family, which was evaluated using dictionary-based classification, Random Forest, and Categorical Boosting models. Compact fingerprint representations were compared with decomposed protocol-level features to determine whether feature decomposition improves classification performance or enhances interpretability. Experimental results show that JA4+ fingerprints enable accurate IoT device identification using only passive encrypted traffic metadata. On CICIoT2023, the complete JA4+* configuration achieved a Macro F1-score of 0.8095 with both RF and CatBoost, although this result was obtained on a smaller subset of connections due to fingerprint availability. On the independent UNSW-IoTraffic dataset, CatBoost achieved a Macro F1-score of 0.9995 with both compact and decomposed representations. Overall, decomposed representations did not provide a consistent predictive advantage over compact fingerprints, although they remained valuable for interpretability and feature-level analysis. These findings indicate that compact JA4+ fingerprints can preserve the discriminative information required for IoT device identification without requiring protocol-level decomposition when predictive performance is the primary objective. The results highlight the potential of JA4+ fingerprinting for scalable IoT security monitoring under increasingly encrypted network conditions.
Keywords:
IoT security
; JA4+ fingerprinting
; TLS fingerprinting
; encrypted traffic analysis
; device identification
; machine learning
; network traffic classification
; passive fingerprinting
; Random Forest
; Zeek
; CICIoT2023
; IoT networks
1. Introduction
The rapid proliferation of Internet of Things (IoT) devices has significantly transformed modern networked environments, enabling automation, monitoring, and smart services across industrial, residential, healthcare, and critical infrastructure domains [1]. However, the increasing number and heterogeneity of connected devices have also introduced major challenges in network visibility, device management, and cybersecurity [2]. Identifying devices operating within IoT networks is becoming progressively more difficult due to the widespread adoption of encrypted communication protocols and the growing complexity of network ecosystems.
Traditional network traffic inspection techniques used to rely heavily on payload analysis and deep packet inspection (DPI) to identify applications, services, or devices. Nevertheless, the evolution of transport security mechanisms, particularly the adoption of TLS 1.3 and Encrypted Client Hello (ECH), has substantially reduced the visibility available to network monitoring systems [3,4]. As encryption becomes the default mechanism for protecting communications, conventional inspection approaches lose effectiveness because relevant application-layer information is no longer accessible without decryption.
In this context, passive network traffic fingerprinting has emerged as a promising alternative for encrypted traffic analysis. Rather than inspecting payload contents, fingerprinting techniques leverage observable characteristics of network protocols, such as TLS handshake parameters or TCP metadata, to derive behavioral signatures associated with devices or applications. One of the most widely adopted approaches is JA3 fingerprinting, which generates signatures from TLS Client Hello parameters [5]. More recently, JA4+ fingerprinting has extended this concept by incorporating additional transport-layer and protocol-level characteristics designed to improve consistency, interpretability, and resilience against fingerprint randomization [6,7].
The use of JA4+ fingerprints is particularly attractive in IoT environments. Many IoT devices generate relatively stable communication patterns due to constrained hardware, embedded firmware, and specialized functionality, together with scarce software updates. These characteristics make transport-layer fingerprints suitable candidates for passive device identification and behavioral monitoring without requiring payload decryption. Furthermore, passive fingerprinting approaches align well with privacy-preserving and low-overhead monitoring architectures, which are increasingly important in modern security frameworks.
Previous studies have explored the use of TLS fingerprinting and machine learning techniques for encrypted traffic analysis, malicious traffic detection, and IoT device classification [8,9,10]. However, most existing approaches focus either on exact fingerprint matching or on fingerprint enrichment using additional metadata such as the Server Name Indication (SNI). As ECH adoption increases, relying on domain-related metadata may become progressively less viable for long-term encrypted traffic analysis methodologies.
This work investigates the use of JA4+ fingerprints for IoT device identification in encrypted network environments without relying on SNI-based information. In particular, the study evaluates multiple JA4+ fingerprint combinations extracted from encrypted traffic traces derived from the CICIoT2023 dataset [11]. The proposed methodology compares complete fingerprint representations with decomposed protocol-level features in order to evaluate whether feature decomposition improves classification performance or primarily provides interpretability and feature-level analytical capabilities. Unlike previous studies primarily focused on developing new traffic fingerprints or classification models, this work provides an empirical assessment of the JA4+ family for passive IoT device identification, systematically comparing individual and combined fingerprints in both compact and decomposed representations and analyzing the contribution of their underlying protocol-level attributes.
The experimental study was conducted using dictionary-based classification techniques, Random Forest (RF), and Categorical Boosting (CatBoost) models applied to JA4+, JA4S, JA4T, JA4TS, and JA4X fingerprints, extracted using the Zeek network monitoring framework [12] and custom scripts. The obtained results indicate that complete JA4+ fingerprint representations already provide strong discriminative capabilities for IoT device identification, while decomposed representations achieve comparable performance without consistently improving classification accuracy.
The main contributions of this paper are summarized as follows:
- Evaluation of JA4+ fingerprints for passive IoT device identification in encrypted network environments, without incorporating payload inspection or active probing techniques.
- Experimental evidence that protocol-level decomposition of JA4+ fingerprints does not provide consistent classification improvements over compact JA4+ representations for IoT device identification, while improving interpretability.
- Assessment of multiple JA4+ fingerprint combinations without relying on SNI-based metadata.
- Experimental validation using encrypted traffic traces derived from the CICIoT2023 and UNSW-IoTraffic datasets.
- Analysis of the interpretability and practical limitations of JA4+-based fingerprinting for scalable IoT security monitoring.
The remainder of this paper is organized as follows. Section 2 reviews related work on encrypted traffic analysis, IoT fingerprinting, and JA4+-based approaches. Section 3 provides background information on JA4+ fingerprinting and encrypted traffic characterization. Section 4 describes the experimental methodology, including dataset preparation, feature extraction, and machine learning methods. Section 5 presents the experimental results, comparative analysis, and study limitations. Section 6 validates the results with a second independent dataset. Section 7 discusses the implications and security considerations of the proposed approach. Finally, Section 8 concludes the paper and outlines future research directions.
2. Related Work
The analysis and classification of encrypted network traffic have become an increasingly relevant research topic due to the widespread adoption of TLS-based communication protocols in modern Internet and IoT environments. Traditional traffic inspection approaches based on payload analysis and DPI are progressively losing effectiveness because encryption mechanisms conceal most application-layer information from network monitoring systems. Consequently, passive fingerprinting and machine learning techniques have emerged as promising alternatives for encrypted traffic characterization and device identification. In the specific context of IoT device fingerprinting, recent approaches have explored different traffic-, hardware-, and software-based features for device identification [13,14,15].
One of the earliest and most influential approaches in TLS fingerprinting is JA3, which generates fingerprints from selected fields contained in the TLS Client Hello message [5]. JA3-based fingerprints have been widely adopted for malware detection, threat intelligence, and encrypted traffic analysis because they provide lightweight and passive identification capabilities without requiring payload decryption. However, JA3 also presents several limitations related to fingerprint instability, susceptibility to evasion techniques, and dependence on exact fingerprint matching.
To address some of these limitations, the JA4+ framework was introduced as an evolution of previous TLS fingerprinting methodologies [6,7]. JA4+ extends traditional TLS fingerprinting by incorporating additional protocol- and transport-layer metadata while improving fingerprint readability, consistency, and interpretability. The framework includes multiple complementary fingerprints associated with TLS, TCP, HTTP, SSH, and certificate-level information, including JA4, JA4S, JA4T, JA4TS, and JA4X, among others [16]. These fingerprints aim to provide more stable and semantically meaningful representations than previous hash-only approaches.
Several studies have explored the use of TLS fingerprinting and machine learning techniques for encrypted traffic analysis. Paracha et al. [8] analyzed TLS usage patterns in consumer IoT devices and demonstrated that encrypted traffic metadata still contains valuable information capable of revealing device-specific behaviors. Similarly, Siwakoti and Rawat [9] investigated the use of JA3 fingerprints combined with machine learning models for malicious traffic detection, showing that passive TLS fingerprints can support effective classification systems even in encrypted environments.
Recent research has also explored fingerprinting approaches specifically oriented toward IoT device identification and behavioral profiling. Llano-Miraval et al. [10] investigated the use of decomposed TLS handshake features for encrypted IoT traffic classification and analyzed defensive strategies against AI-driven traffic analysis. Their work demonstrated that protocol-level feature decomposition can support machine learning-based classification methodologies while improving interpretability of encrypted traffic representations. Other works have investigated machine learning-based approaches for IoT security enhancement using fingerprinting techniques and embedded device characteristics [17,18].
Recent works have also explored the practical use of JA4+ fingerprints for encrypted traffic analysis. For instance, Burgetová et al. [19] investigated the identification of network applications in encrypted TLS traffic by comparing several complementary approaches, including JA3/JA4 fingerprinting, SNI-based identification, and machine learning classifiers. Their study showed that the combination of JA4 and JA4S fingerprints provides better identification performance than the legacy JA3/JA3S approach, confirming the advantages of the newer fingerprinting methodology. Later, Fernández Terrasa et al. [20] explored the identification of encrypted mobile application traffic using fingerprint-based methodologies, emphasizing the applicability of passive traffic characterization techniques for encrypted communication analysis. Unlike these works, which focus on application identification and the comparison of multiple identification techniques, our study investigates the use of the complete JA4+ fingerprint family for IoT device identification and, in particular, analyzes whether decomposing JA4+ fingerprints into protocol-level attributes provides measurable benefits for machine-learning-based classification.
JA4+ fingerprints have also been successfully applied to cybersecurity tasks beyond device identification. Matoušek et al. [21] demonstrated the applicability of JA4+ fingerprints for malware detection, showing that protocol-level metadata can effectively distinguish malicious from benign communications without decrypting traffic. Similarly, Polo Peyres et al. [22] evaluated machine learning approaches for malware detection using statistical traffic features and fingerprinting information extracted from encrypted communications. Their work focuses on threat detection, whereas the present study investigates the use of JA4+ fingerprints for passive identification of IoT devices and evaluates the impact of decomposing JA4+ fingerprints into protocol-level features for machine learning-based classification.
In parallel, multiple datasets and benchmarking initiatives have been proposed to support research on IoT traffic analysis and intrusion detection. Among them, the CICIoT2023 dataset [11] has become a relevant benchmark for evaluating large-scale IoT security and encrypted traffic classification methodologies due to its diversity of devices, attack scenarios, and communication traces.
Despite the growing interest in JA4+ fingerprinting and encrypted traffic analysis, several challenges remain insufficiently explored. First, many existing approaches continue relying on exact fingerprint matching techniques or on metadata such as the SNI, whose long-term availability may be reduced by mechanisms such as ECH. Second, although feature decomposition approaches have been proposed in previous works, the practical impact of decomposed protocol-level representations on classification performance remains unclear.
In particular, it is still uncertain whether decomposed fingerprint representations provide substantial advantages over compact JA4+-based fingerprints for IoT device identification in encrypted environments. This paper addresses these questions by systematically evaluating multiple JA4+ fingerprint combinations and comparing complete fingerprint representations with decomposed protocol-level features using machine learning-based classification techniques.
3. Background on JA4+ Fingerprinting
Passive fingerprinting techniques aim to identify devices, applications, or communication patterns by analyzing observable network metadata without requiring payload inspection. In encrypted environments, where application-layer information becomes inaccessible due to the widespread adoption of TLS encryption, passive fingerprinting has emerged as an important mechanism for maintaining network visibility and supporting traffic characterization tasks.
One of the earliest and most influential approaches in TLS fingerprinting is JA3, which generates signatures from selected fields contained in the TLS Client Hello message [5]. JA3 fingerprints are constructed using ordered values such as TLS version, cipher suites, extensions, supported groups, and elliptic curve point formats. The resulting fingerprint is typically represented as an MD5 hash associated with a particular TLS client configuration.
Although JA3 gained widespread adoption due to its simplicity and effectiveness for malware detection and encrypted traffic analysis, several practical limitations have been identified. First, JA3 fingerprints are sensitive to protocol changes, extension ordering variations, software updates, and implementation differences. Second, exact fingerprint matching approaches may suffer from reduced robustness in heterogeneous environments. Finally, JA3 primarily focuses on TLS handshake metadata and does not incorporate additional transport-layer context.
To address some of these limitations, the JA4+ framework was introduced as an evolution of previous TLS fingerprinting methodologies [6,7]. Unlike JA3, JA4+ was designed to improve fingerprint consistency, readability, and interpretability while incorporating additional protocol- and transport-layer information. The framework defines multiple complementary fingerprint types associated with different protocol layers and communication stages.
The JA4+ ecosystem includes fingerprints associated with TLS, TCP, HTTP, SSH, and X.509 certificate information. Among them, JA4 focuses on TLS client fingerprinting, JA4S characterizes TLS server responses, JA4T and JA4TS extend fingerprinting to TCP-level communication patterns, and JA4X incorporates certificate-related information [16]. These fingerprints aim to provide semantically meaningful protocol representations suitable for passive encrypted traffic analysis.
Figure 1 illustrates the structure of a typical JA4 fingerprint and its decomposition into protocol-level components. Unlike traditional opaque hash-based representations, JA4+ fingerprints preserve part of the semantic structure of the underlying protocol metadata, enabling feature-level interpretation and analysis.
Table 1 summarizes the main differences between JA3 and JA4+ fingerprinting approaches. Compared with JA3, JA4+ incorporates additional metadata sources, improves interpretability, supports protocol-level feature decomposition, and includes more protocols apart from TLS.
The interpretability provided by JA4+ decomposition enables analysis of individual protocol-level characteristics used during encrypted communication. Such decomposition may facilitate feature-level inspection and machine learning-based analysis by exposing semantically meaningful protocol attributes instead of relying exclusively on exact fingerprint equality.
This capability is particularly relevant in IoT environments, where many devices exhibit relatively stable communication patterns determined by embedded firmware, constrained hardware resources, and specialized application behavior. Consequently, transport-layer metadata and TLS handshake characteristics can provide sufficiently distinctive signatures for passive device identification and monitoring purposes.
At the same time, evolving encryption standards continue reducing the amount of metadata exposed during encrypted communication. Mechanisms such as TLS 1.3 and ECH progressively conceal protocol information that was previously accessible during TLS negotiation [3,4]. In particular, ECH limits the visibility of metadata such as the SNI, which has traditionally been used in several encrypted traffic classification methodologies.
Under these conditions, passive fingerprinting techniques that rely exclusively on observable protocol and transport-layer characteristics become increasingly relevant for future encrypted traffic analysis systems. Consequently, understanding the discriminative capabilities and limitations of JA4+-based fingerprints without relying on SNI-related information represents an important research challenge.
In this work, JA4+, JA4S, JA4T, JA4TS, and JA4X fingerprints are analyzed both as complete identifiers and as decomposed protocol-level components in order to evaluate their suitability for machine learning-based IoT device identification. The study specifically investigates whether decomposed representations provide practical advantages over compact fingerprint-based approaches in encrypted environments where metadata visibility is progressively reduced.
4. Methodology
This section describes the experimental methodology used to evaluate the effectiveness of JA4+ fingerprints for passive IoT device identification in encrypted network environments. The proposed workflow includes dataset preparation, encrypted traffic processing, fingerprint extraction, feature representation generation, and machine learning-based classification.
4.1. Overview of the Experimental Pipeline
The experimental workflow was designed to evaluate multiple JA4+ fingerprint combinations under different representation strategies. In particular, the study compares complete fingerprint representations with decomposed protocol-level features in order to determine whether feature decomposition provides practical advantages for IoT device classification.
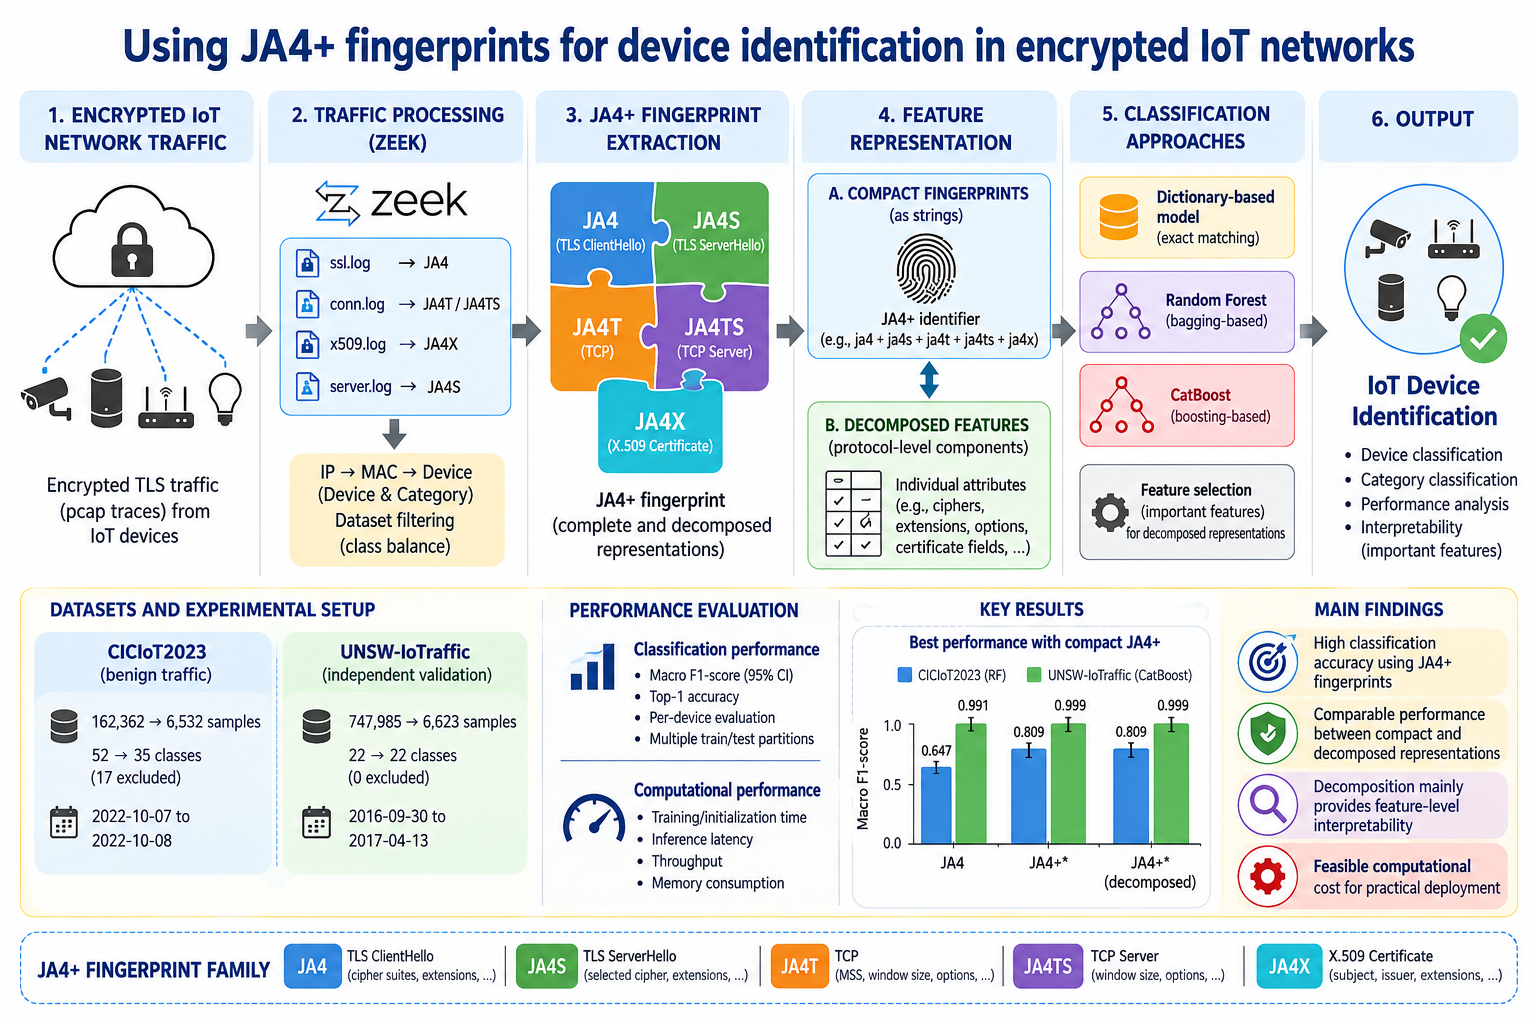
Figure 2 summarizes the overall processing pipeline adopted in this work.
The workflow begins with encrypted traffic traces extracted from the CICIoT2023 dataset [11]. Packet captures were processed using the Zeek network monitoring framework in order to extract JA4, JA4S, JA4X, JA4T, and JA4TS fingerprints together with associated TLS- and TCP-level metadata.
The extracted information was subsequently transformed into different feature representations suitable for classification analysis. Two primary representation strategies were considered during the experiments:
- Complete fingerprint representations based on exact JA4+ identifiers.
- Decomposed protocol-level representations derived from the semantic components of JA4+ fingerprints.
The resulting feature sets were evaluated using dictionary-based classification, RF, and CatBoost models.
4.2. Dataset Description
The experiments conducted in this work were initially based on the CICIoT2023 dataset [11], which provides large-scale network traffic captures generated from heterogeneous IoT environments under both benign and malicious conditions. The dataset includes multiple IoT device categories, communication protocols, and attack scenarios, making it suitable for evaluating encrypted traffic analysis methodologies.
The selected capture corresponds to benign IoT traffic from the CICIoT2023 dataset. The original PCAP file, BenignTraffic.pcap, has an approximate size of 1.90 GB and contains traffic generated by 55 IoT devices. Device labels were assigned using a MAC-to-device mapping file created for this study, which associates observed MAC addresses with IoT device names and broader device categories.
For this study, only traffic traces relevant to encrypted communication analysis were considered. Packet capture (PCAP) files containing TLS-based communication flows were processed in order to extract JA4+-related fingerprint information and associated metadata. The use of encrypted traffic traces enables evaluation of passive identification methodologies under realistic visibility constraints where payload inspection is not available.
Since not all fingerprint families are present in every connection, the number and composition of the samples available for classification may differ across fingerprint combinations. Consequently, comparisons between configurations should be interpreted as empirical observations rather than as strictly controlled evaluations of the incremental contribution of each fingerprint family.
Table 2 summarizes the main characteristics of the dataset and the extracted fingerprint representations used during the experiments.
As is common in IoT traffic datasets, the number of connections generated by each device was highly unbalanced. To mitigate the impact of class imbalance during model training and evaluation, classes with insufficient samples were excluded, while highly dominant classes were constrained through dataset filtering. The selected thresholds were manually adjusted according to the fingerprint distribution observed in the CICIoT2023 benign traffic capture, ensuring that all retained device classes contained sufficient samples for both training and testing.
To mitigate the effect of severe class imbalance while retaining a sufficient number of observations for per-device training and testing, explicit lower and upper sample thresholds were applied. Device classes containing fewer than 5 samples were excluded from the analysis, whereas classes containing more than 500 samples were limited to 500 samples. As detailed in Table 3, this filtering audit reports the exact breakdown across the different fingerprint combinations, showing that for the JA4+* experiment, 45 device classes were excluded (as listed individually in Table 4), reducing the dataset classes and sample sizes accordingly. Consequently, the reported classification metrics should be interpreted as performance over the subset of device classes retained after this filtering procedure.
4.3. Fingerprint Extraction and Preprocessing
JA4+ fingerprints were extracted from the network traces using Zeek [12]. Zeek was configured to process PCAP files and generate structured logs containing TLS- and TCP-related fingerprint metadata. Additional preprocessing scripts implemented in Python were used to consolidate extracted information and prepare feature representations for classification analysis.
JA4X fingerprints were generated only for connections in which X.509 certificate information was observable in the processed traces. No attempt was made to infer certificate-derived fingerprints for connections whose certificate messages were encrypted or otherwise unavailable. The resulting JA4X-based experiments therefore used a subset of the connections considered in the JA4-, JA4S-, and TCP-based configurations.
Two parallel feature-generation pipelines were therefore created. The first preserved each JA4+ fingerprint as a complete categorical identifier, whereas the second decomposed fingerprints into their constituent protocol-level attributes. This design enabled a direct comparison between compact fingerprint representations and feature-level representations while keeping the remaining stages of the classification workflow unchanged.
The preprocessing stage included cleaning incomplete records, normalizing categorical values, handling missing fields, and organizing extracted fingerprints according to device labels available in the dataset. Fingerprints were then transformed into two alternative representations:
- Complete fingerprint strings.
- Decomposed protocol-level components.
The decomposition process enabled analysis of individual protocol-level characteristics such as TLS versions, cipher suite counts, extension counts, ALPN (Application-Layer Protocol Negotiation) identifiers, transport protocols, and additional metadata components extracted from JA4+ fingerprints.
Table 5 summarizes the evaluated fingerprint representations considered during the experiments. Moreover, Table 6 summarizes the protocol-level characteristics extracted from each JA4+ fingerprint family and the number of features contributed by each one for the decomposed fingerprints. Together, these fingerprint families provide a structured representation of observable TLS, TCP, and X.509 certificate metadata that forms the basis for the classification experiments discussed later.
To complete the characterization of the dataset, Figure 3 summarizes the distribution of extracted JA4+JA4S fingerprints across the analyzed IoT devices, including both the total number of observed fingerprints and the number of distinct fingerprints per device. This characterization provides an overview of the variability present in the dataset prior to the classification experiments.
4.4. Classification Methodology
Three classification approaches were evaluated during the experiments: dictionary-based classification and two machine learning models: Random Forest (RF) and CatBoost.
The dictionary-based methodology relied on exact fingerprint matching between training and testing instances. During training, each fingerprint was represented as a tuple of its selected feature values (ja4, ja4s, ja4x, ja4t, ja4ts), and mapped to the most frequent device class among training instances with that exact fingerprint. Ties were broken by selecting the alphabetically earliest device class. During testing, each observed fingerprint was searched in this mapping and assigned the mapped device class. Fingerprints not observed during training were assigned the most frequent device class in the training set, with ties broken as previously mentioned, whereas fingerprints associated with multiple device classes were assigned the most frequent class for that fingerprint, again breaking ties in the same way. This approach therefore evaluates the discriminative capability of compact fingerprint representations under direct matching conditions, without learning an additional statistical classification model.
RF was initially selected due to its robustness with heterogeneous feature spaces and its ability to provide feature-importance estimates, which are useful for analyzing the contribution of decomposed JA4+ attributes. Since the primary objective is to compare fingerprint representations rather than classification algorithms, CatBoost was additionally considered as a complementary boosting-based model to assess whether the observed behavior depends on the learning strategy.
After class filtering, the dataset was partitioned independently for each device category in order to preserve the presence of every class in both training and testing subsets. For each retained device, 80% of the available samples were assigned to the training set and 20% to the testing set. This procedure ensured that all evaluated device categories were represented during both model training and evaluation.
The evaluated hyperparameters included the number of estimators, maximum tree depth, minimum samples per split, and minimum samples per leaf. The final configuration was selected according to Macro F1-score performance using a grid search algorithm to find the best suited hyperparameters with a cross validation of 5 subsets in the training dataset.
CatBoost was evaluated as a complementary boosting-based classifier using the same training and testing data as RF. The model was configured with 200 iterations, a maximum tree depth of 6, and a learning rate of 0.1. Multiclass classification was performed using the MultiClass loss function, with automatic class balancing enabled through auto_class_weights=Balanced.
For both RF and CatBoost, categorical fingerprint features were transformed into binary indicator variables using one-hot encoding prior to model training. The encoder was fitted using the training data and subsequently applied to the testing data. All experiments were initially executed using a fixed random seed (42) to ensure reproducibility of the obtained results. However, to assess the sensitivity of the classification results to the random train/test partition, the evaluation was additionally repeated using five random seeds (42, 123, 456, 789, and 2026). Performance was summarized as the mean and standard deviation across the resulting partitions.
The experiments evaluated multiple fingerprint combinations, including JA4, JA4S, JA4T, JA4TS, and JA4X representations, both independently and in combined configurations. In addition, decomposed protocol-level features were evaluated in order to compare their effectiveness against compact fingerprint representations.
4.5. Evaluation Metrics
Several evaluation metrics were considered to assess the effectiveness of JA4+-based IoT device identification. Accuracy was used as a general indicator of classification performance, whereas precision, recall, and Macro F1-score provided additional insight into class-level behavior and model robustness. In addition to point estimates, 95% confidence intervals (CIs) for the Macro F1-score were estimated using bootstrap resampling of the test predictions. This analysis was used to characterize the uncertainty associated with the reported classification performance. Specifically, 1 000 bootstrap samples were generated by resampling the test instances with replacement using a fixed random seed of 42. For each bootstrap sample, the Macro F1-score was computed, and samples containing fewer than two classes were discarded. The 95% confidence interval () was then obtained from the 2.5th and 97.5th percentiles of the resulting bootstrap distribution.
Moreover, Top-1, Top-3, and Top-5 accuracy metrics were evaluated in order to analyze the ranking capabilities of the classification methodologies. These metrics are particularly relevant in IoT identification scenarios where multiple candidate device categories may exhibit partially overlapping fingerprint characteristics.
Top-k metrics were included because several IoT device categories exhibit partially overlapping communication behaviors and similar protocol stacks. Under this evaluation strategy, a prediction is considered correct if the true device category appears within the k highest-ranked predictions generated by the classifier.
These metrics are particularly useful in passive IoT identification scenarios, where identifying a small set of likely candidate devices may already provide valuable operational information for network monitoring and security analysis.
Table 7 summarizes the evaluation metrics considered during the experiments.
Feature importance analysis was additionally performed using RF classifiers in order to identify the most discriminative protocol-level fingerprint characteristics. This analysis supports evaluation of the practical utility and interpretability of decomposed JA4+ representations.
4.6. Top-Feature Evaluation
In addition to the baseline classification experiments, an auxiliary analysis was conducted to evaluate the contribution of individual fingerprint components to the overall classification performance. This analysis aimed to determine whether a reduced subset of highly informative features could achieve results comparable to those obtained using the complete feature set. Feature rankings and reduced feature subsets were derived exclusively from the training data. The testing subset was not used during feature ranking, hyperparameter selection, or subset definition.
Feature importance was quantified using the Random Forest Mean Decrease in Impurity (MDI), which measures the total reduction in node impurity attributed to each feature across the trees in the ensemble. The resulting importance values were then aggregated according to their original JA4+ fingerprint components in order to identify the protocol-level attributes contributing most strongly to device classification.
Based on these rankings, additional classification models were trained using progressively smaller subsets of the highest-ranked features. The purpose of this analysis was to determine whether the discriminative information provided by the decomposed JA4+ representation was concentrated in a limited number of protocol-level attributes or distributed across the complete feature set. By comparing the performance of the reduced models with that obtained using all available features, we assessed the extent to which feature-space dimensionality could be reduced while preserving device-identification performance.
5. Results
This section presents the experimental results obtained from the evaluation of JA4+ fingerprints for passive IoT device identification in encrypted network environments. The analysis first compares the classification performance of compact fingerprint representations and decomposed protocol-level features using dictionary-based matching, Random Forest, and Categorical Boosting. The computational cost of the evaluated classification approaches is then analyzed in terms of training time, inference latency, throughput, and memory consumption. Next, the classification behavior is further examined through confusion matrix analysis, followed by an evaluation of feature importance to identify the protocol-level attributes contributing most strongly to device discrimination. An additional top-feature analysis investigates the impact of feature selection on classification performance. Finally, the main limitations of the experimental evaluation are outlined to provide the appropriate context for interpreting the reported results.
5.1. Classification Performance
The first stage of the evaluation analyzed the overall classification performance achieved using the different JA4+ fingerprint combinations and representation strategies. The experiments demonstrated that JA4+-based fingerprints provide strong discriminative capabilities for IoT device identification even when relying exclusively on observable encrypted traffic metadata.
Table 8 summarizes the main classification results obtained during the experiments. Overall, compact and decomposed representations produced broadly comparable results across the evaluated configurations, without a consistent advantage for either representation. The strong performance observed for the full JA4+* configuration should, however, be interpreted together with the support values reported in Table 8. The individual JA4+ fingerprint families are not uniformly available across all connections; therefore, requiring multiple fingerprints simultaneously reduces the number of observations for which a complete representation can be constructed. In particular, the JA4+* configuration was evaluated on 93 observations, compared with 6532 observations for JA4 alone. Consequently, the performance observed for JA4+* cannot be attributed exclusively to the addition of fingerprint families, since the different configurations may be evaluated on partially different traffic subsets. The results should therefore be interpreted under their corresponding fingerprint-availability conditions rather than as a controlled incremental comparison over an identical set of connections.
From a predictive-performance perspective, fingerprint decomposition did not provide a consistent advantage over compact representations. Compact and decomposed configurations produced broadly comparable results, with only small and non-systematic differences across the evaluated combinations. Consequently, although decomposition does not consistently improve predictive performance, its contribution to feature-level interpretability is further explored in SubSection 5.4.
CatBoost provides an additional comparison based on a boosting learning strategy, complementing the bagging-based RF classifier. The comparable compact-versus-decomposed behavior observed with both classifiers suggests that the main finding is not specific to the RF learning strategy.
To complement the point estimates, Table 8 reports 95% bootstrap confidence intervals for the Macro F1-score. The confidence intervals for the compact and decomposed representations substantially overlap for the evaluated classifiers, consistent with the small differences observed in their point estimates. Overall, these results do not show a systematic predictive advantage for the decomposed representation over its compact counterpart.
5.2. Computational Performance
In addition to predictive performance, the computational requirements of the evaluated classification approaches were measured in order to characterize their relative deployment cost. The analysis considered training time, inference latency per sample, throughput, and memory consumption. Measurements were obtained for dictionary-based matching, RF, and CatBoost using both compact and decomposed representations.
The hardware used for these measurements was a Lenovo ThinkPad L13 laptop with an Intel64 Family 6 Model 142 Stepping 12 (4 physical cores, 8 threads, maximum frequency of 2300 MHz), 16 GB RAM, running Windows 11, Python 3.13.14, scikit-learn 1.8.0 and CatBoost Version 1.2.10.
Table 9 summarizes the computational results obtained with CICIoT2023. To provide representative measurements without repeating the benchmark for every fingerprint combination, the computational analysis considered the JA4-only configuration and the complete JA4+* configuration, representing a single-fingerprint setting and the most comprehensive fingerprint combination, respectively. Because JA4-only and JA4+* experiments contain different numbers of available observations, computational measurements should primarily be compared across methods and representations within the same fingerprint configuration rather than directly across the two configurations.
Memory usage was measured using psutil as the increase in process-level resident set size (RSS) during training and inference. A conservative minimum floor was applied to avoid near-zero or negative measurements caused by garbage-collection and operating-system noise. Consequently, values close to this floor should be interpreted as order-of-magnitude upper-bound estimates rather than precise memory measurements.
Dictionary-based matching exhibited the lowest computational cost among the evaluated approaches. In the JA4-only experiment, its inference latency was 0.0067 ms per sample, corresponding to a throughput of approximately 149 388 samples/s. For the JA4+* experiment, dictionary-based matching required 0.0790 ms per sample, which remained lower than the inference latency of the corresponding machine-learning classifiers. Dictionary-based matching also required minimal initialization time and the lowest measured memory consumption.
Among the machine-learning approaches, CatBoost consistently provided lower inference latency than RF in the evaluated configurations. For the compact JA4 representation, CatBoost required 0.0260 ms per sample compared with 0.0924 ms for RF, whereas for the compact JA4+* representation the corresponding values were 0.3449 and 2.9354 ms per sample. A similar pattern was observed for the decomposed representations. CatBoost therefore provided higher inference throughput than RF, although it generally required more memory.
The computational effect of fingerprint decomposition was model- and configuration-dependent. Decomposition generally increased inference latency for both machine-learning classifiers, whereas its effect on training time was not uniform. For example, RF training time decreased from 10.714 to 2.317 s in the JA4-only experiment, while CatBoost training time increased from 13.497 to 40.210 s. These results indicate that the computational impact of decomposition cannot be characterized solely as an increase in feature-processing cost and also depends on the classifier and the resulting feature representation.
Overall, dictionary-based matching provides the most lightweight solution when exact matches with previously observed fingerprints are sufficient. Among the evaluated machine-learning approaches, CatBoost provides lower inference latency and higher throughput than RF, at the cost of greater memory consumption. These measurements quantify the computational trade-offs associated with the different classification strategies and show that the choice of representation and classifier affects computational requirements differently.
5.3. Confusion Matrix Analysis
To further evaluate classification behavior, confusion matrix analysis was performed in order to identify patterns of correct and incorrect predictions across device categories.
Figure 4 presents the confusion matrix obtained for the RF classifier using the decomposed JA4 representation.
The confusion matrix analysis showed that most IoT device categories could be accurately distinguished using JA4+-based features. Nevertheless, certain device classes exhibited partial overlap, which may reflect similarities in protocol implementations, communication libraries, or TLS configurations.
These misclassification patterns indicate that, although JA4+ fingerprints provide strong discriminative capabilities, limitations may arise when devices exhibit similar transport- and application-layer behaviors.
5.4. Feature Importance Analysis
Feature importance analysis was subsequently performed with the training dataset to identify the protocol-level attributes contributing most strongly to classification performance. Figure 5 presents the relative importance of the twenty most relevant features extracted during the experiments for the whole set of signatures. Feature importance was quantified using the Mean Decrease in Impurity (MDI), a built-in feature importance metric in Random Forest that measures the total reduction in node impurity attributed to each feature across the trees in the ensemble.
The analysis revealed that several JA4+* components provide particularly strong discriminative capabilities. The most relevant features were primarily associated with TLS negotiation behavior, extension-related metadata, ALPN identifiers, and transport-layer characteristics. These results indicate that several protocol-level attributes contribute more strongly than others to device differentiation.
Interestingly, several JA4X certificate-derived features also appear among the most informative attributes. In particular, the issuer, subject, and certificate extension hashes provide substantial discriminative power, indicating that X.509 certificate metadata contributes to distinguishing IoT devices when such information is available.
At the same time, the results indicate that many decomposed protocol-level components individually provide limited additional discriminative value when compared with compact fingerprint representations. This observation is consistent with the classification results presented in Table 8.
5.5. Top-Feature Analysis
To further investigate the discriminative information encoded within JA4+ fingerprints, an additional set of experiments was conducted using reduced feature subsets derived from the feature importance rankings obtained from the RF classifier.
Starting from the complete decomposed feature set, progressively smaller subsets containing only the most relevant features were selected and used to train new classification models. The objective was to evaluate the effect of reducing the feature-space dimensionality on classification performance.
Table 10 summarizes the performance obtained using different numbers of selected features. The effect of feature reduction varied across fingerprint combinations. The full evaluated combination retained the same performance using 15 of the 33 available features, whereas other configurations exhibited different degrees of degradation, particularly in Top-1 accuracy.
These findings suggest that reduced feature subsets may preserve competitive performance in some configurations, although this behavior is not consistent across all evaluated fingerprint combinations. Consequently, feature selection may represent a viable strategy for reducing input dimensionality while maintaining competitive classification performance.
5.6. Limitations
Several limitations associated with the conducted experiments should be considered when interpreting the obtained results.
First, the main evaluation was conducted using traffic traces derived from the CICIoT2023 dataset and two machine-learning classifiers, RF and CatBoost. Although this experimental design enables a systematic comparison between compact and decomposed fingerprint representations, the results obtained from a single dataset may not necessarily generalize to other IoT datasets, traffic conditions, or machine-learning approaches. To partially address this limitation, Section 6 presents an additional evaluation using an independently collected IoT dataset (UNSW-IoTraffic).
Additionally, since different JA4+ components are not necessarily available for every network connection, the evaluated fingerprint configurations may rely on partially different subsets of traffic. Therefore, comparisons between configurations should be interpreted as empirical observations rather than strictly controlled incremental evaluations.
Second, the effectiveness of fingerprint-based identification approaches depends on the stability of observable protocol characteristics. Firmware updates, protocol modifications, operating system changes, and implementation-specific behaviors may alter fingerprint representations over time and affect classification consistency. Furthermore, fingerprint collisions may occur among devices sharing similar firmware ecosystems, operating systems, or communication libraries, as partially observed during the confusion matrix analysis.
Third, the study focused exclusively on passive encrypted traffic analysis without incorporating payload inspection or active probing techniques. While this design choice aligns with privacy-preserving monitoring objectives, it may also limit the amount of information available for device differentiation in highly homogeneous communication environments. In addition, adversarial manipulation represents an important challenge, since attackers may attempt to imitate legitimate protocol behaviors in order to evade fingerprint-based monitoring systems.
Finally, evolving encryption mechanisms such as TLS 1.3 and ECH continue reducing the amount of metadata available for passive traffic analysis. Although the evaluated JA4+ fingerprints rely primarily on observable transport- and protocol-layer information, future protocol developments may further constrain passive fingerprinting capabilities.
A particular limitation concerns JA4X, which relies on X.509 certificate information. In TLS 1.3, the Certificate message is transmitted after handshake encryption has been established, preventing a purely passive observer without access to session secrets from directly extracting JA4X. Certificate-derived fingerprints may still be available for TLS 1.2 or earlier sessions, from decrypted TLS 1.3 traffic, or when certificate information is obtained at an endpoint or through another trusted source. Therefore, the contribution of JA4X reported in this study should be interpreted in the context of the TLS-version distribution, certificate visibility, and monitoring architecture of the analyzed CICIoT2023 traffic.
Despite these limitations, the results indicate that JA4+-based fingerprints provide a viable approach for passive IoT device identification under the encrypted traffic conditions evaluated in this study.
6. Validation on an Independent Dataset
To assess whether the main findings obtained with the CICIoT2023 dataset were specific to a single traffic collection, we performed an additional evaluation using the independently collected UNSW-IoTraffic dataset [23]. The purpose of this experiment was not to perform cross-dataset model transfer, but rather to determine whether the relative behavior of compact and decomposed JA4+ representations observed with CICIoT2023 was reproduced in a different IoT traffic environment.
In particular, the validation addresses two aspects of the original experimental setting. First, it evaluates JA4+-based device identification using traffic from an independent dataset. Second, it examines whether the main conclusion regarding fingerprint decomposition is preserved when the same representation comparison is performed outside CICIoT2023.
6.1. Independent Dataset and Experimental Setup
The UNSW-IoTraffic dataset was used as an independent dataset for the validation experiment. The dataset was collected independently by a different research team from CICIoT2023 and, therefore, it provides a separate traffic environment in which to evaluate the proposed methodology.
Specifically, the evaluation on UNSW-IoTraffic covers a capture period spanning from 2016-09-30 to 2017-04-13. The dataset initially comprises 747 985 total samples distributed across 22 device classes. As detailed in Table 11, the filtering audit across the various JA4+ fingerprint configurations demonstrates a robust presence of data traces, where no device classes were excluded from the analysis. Consequently, the final trained models leverage all 22 original device classes, with post-filter sample sizes ranging from 6 533 to 6 623 samples depending on the signature representation.
The same general processing and classification methodology described in Section 4 was applied to the UNSW-IoTraffic data. JA4+ information was represented using both compact fingerprints and their corresponding decomposed protocol-level attributes. The resulting representations were evaluated using dictionary-based matching, Random Forest, and CatBoost.
The experimental protocol followed the same train/test methodology used for the main experiments wherever applicable. Performance was evaluated using accuracy, precision, recall, and Macro F1-score. In addition to the point estimates, 95% bootstrap confidence intervals were computed for the Macro F1-score as described in Section 4.5.
6.2. Compact versus Decomposed Fingerprint Validation
Table 12 summarizes the classification performance obtained on the UNSW-IoTraffic dataset using compact and decomposed JA4+ representations. The purpose of this experiment was to assess whether the relative behavior observed with CICIoT2023 was reproduced in an independently collected IoT traffic dataset.
All evaluated approaches achieved high classification performance on the UNSW-IoTraffic dataset. More importantly for the purpose of this validation, decomposing the JA4+ representation did not provide a consistent predictive advantage over the corresponding compact representation.
For RF, the Macro F1-score increased from 0.9952 with the compact representation to 0.9987 with the decomposed representation. In contrast, CatBoost achieved the same Macro F1-score of 0.9995 with both representations. The bootstrap confidence intervals substantially overlap between the compact and decomposed configurations, indicating that the small differences in the point estimates should not be interpreted as evidence of a systematic improvement due to fingerprint decomposition.
These results reproduce the main qualitative observation obtained with CICIoT2023: decomposition does not consistently improve predictive performance over the compact JA4+ representation. Moreover, observing the same general behavior with both RF and CatBoost indicates that this finding is not restricted to the RF learning strategy. The independent-dataset experiment therefore provides additional evidence that the observed compact-versus-decomposed behavior is not specific to the CICIoT2023 traffic collection.
Nevertheless, the results should not be interpreted as demonstrating universal generalization across IoT environments, device versions, or protocol implementations, since the models were trained and evaluated independently within each dataset rather than transferred between datasets.
6.3. Stability Across Random Data Partitions
In addition to the single-split evaluation, we examined the sensitivity of classification performance to the random train/test partition. The evaluation was repeated using five random seeds (42, 123, 456, 789, and 2026), and the resulting performance was summarized using the mean and standard deviation across the five partitions.

Table 13.
Repeated train/test partition results comparing JA4 and JA4+* across classifiers and datasets. Results are reported as mean ± standard deviation.
Table 13.
Repeated train/test partition results comparing JA4 and JA4+* across classifiers and datasets. Results are reported as mean ± standard deviation.
| Experiment | Dataset | Representation | Macro F1 | Accuracy |
|---|---|---|---|---|
| Classifier: Random Forest | ||||
| JA4 | CICIoT2023 | Compact | ||
| JA4 | CICIoT2023 | Decomposed | ||
| JA4 | UNSW-IoTraffic | Compact | ||
| JA4 | UNSW-IoTraffic | Decomposed | ||
| JA4+* | CICIoT2023 | Compact | ||
| JA4+* | CICIoT2023 | Decomposed | ||
| JA4+* | UNSW-IoTraffic | Compact | ||
| JA4+* | UNSW-IoTraffic | Decomposed | ||
| Classifier: CatBoost | ||||
| JA4 | CICIoT2023 | Compact | ||
| JA4 | CICIoT2023 | Decomposed | ||
| JA4 | UNSW-IoTraffic | Compact | ||
| JA4 | UNSW-IoTraffic | Decomposed | ||
| JA4+* | CICIoT2023 | Compact | ||
| JA4+* | CICIoT2023 | Decomposed | ||
| JA4+* | UNSW-IoTraffic | Compact | ||
| JA4+* | UNSW-IoTraffic | Decomposed | ||
The repeated evaluation showed limited variability in Macro F1 across the evaluated random partitions. For the JA4 experiments, the standard deviation of Macro F1 ranged from 0.0042 to 0.0178 on CICIoT2023 and from 0.0007 to 0.0028 on UNSW-IoTraffic, depending on the classifier and representation. The JA4+* experiments exhibited no variability across the evaluated CICIoT2023 partitions for either classifier or representation, whereas the corresponding UNSW-IoTraffic experiments showed standard deviations below 0.003. Overall, the results indicate that the observed performance was reasonably stable across the five evaluated train/test partitions, with greater partition sensitivity for the JA4 experiments on CICIoT2023 than for the corresponding UNSW-IoTraffic experiments.
This repeated-partition analysis complements the bootstrap confidence intervals reported in Section 5.1 and Section 6.2. While the bootstrap analysis characterizes the uncertainty associated with performance estimates for a given test set, the multi-seed experiment evaluates the sensitivity of the results to changes in the train/test partition.
6.4. Validation Summary
The independent evaluation on UNSW-IoTraffic supports the main qualitative finding obtained with CICIoT2023. For both RF and CatBoost, decomposing the JA4+ representation did not yield a consistent improvement over the corresponding compact representation. Dictionary-based matching additionally provided a compact-representation baseline with high classification performance.
The repeated-partition analysis further indicates that the reported classification performance is reasonably stable across the evaluated random splits. Taken together, these experiments strengthen the empirical evidence supporting the use of compact JA4+ representations when predictive performance is the primary objective, while the decomposed representation remains useful for the feature-level interpretability analysis presented in Section 5.4.
Nevertheless, validation on two datasets does not establish robustness to firmware updates, operating-system changes, TLS-library evolution, or other forms of temporal device variation. These factors remain outside the scope of the present evaluation and are further discussed in Section 7.
7. Discussion
The experimental results obtained in this work demonstrate that JA4+-based fingerprinting provides an effective mechanism for passive IoT device identification in encrypted network environments. The evaluated fingerprint combinations achieved strong classification performance while relying exclusively on observable protocol- and transport-layer metadata, without requiring payload inspection or SNI-based information.
One of the main objectives of this study was to evaluate whether decomposed protocol-level fingerprint representations provide practical advantages over compact JA4+ fingerprints for encrypted IoT traffic classification. The results indicate that both representation strategies achieve broadly comparable predictive performance. Rather than improving classification accuracy, the main value of decomposition lies in exposing the protocol-level attributes that drive device discrimination and enabling a more interpretable analysis of encrypted traffic.
The comparable predictive performance of compact and decomposed representations can be explained by the fact that decomposition does not introduce new traffic information. The compact fingerprint already aggregates its constituent protocol-level characteristics into a distinctive representation, and when this representation is sufficiently discriminative, exposing the same characteristics as separate features does not necessarily provide additional information for classification. The value of decomposition is therefore primarily interpretative: individual attributes can be examined separately to determine which protocol characteristics contribute to device discrimination and which are shared across devices. This may be particularly useful for analyzing devices with similar protocol characteristics, since decomposition can reveal common components that would not be directly observable when comparing only complete compact fingerprints. Thus, compact representations may be preferable when feature-level interpretation is not required, whereas decomposed representations provide complementary insight into the protocol-level characteristics underlying device identification.
Another important implication of these findings concerns the evolution of encrypted communication protocols. Mechanisms such as TLS 1.3 and ECH continue reducing the amount of metadata exposed during encrypted communications [3,4]. For this reason, the experiments conducted in this work intentionally avoided relying on SNI-related information as a primary classification feature. Additionally, although several JA4X certificate-derived attributes contributed to device classification in the analyzed data, their operational availability depends on the TLS version and monitoring architecture. Consequently, the measured contribution of JA4X should be interpreted in the context of the analyzed traffic and extraction environment, as discussed above in the study limitations. In any case, the obtained results demonstrate that meaningful IoT device identification remains feasible using transport- and protocol-layer metadata that remain observable in the analyzed traffic traces. Thus, JA4+-based fingerprinting represents a practical approach for maintaining network visibility as encrypted protocols continue evolving.
From an operational perspective, the evaluated methodology presents several advantages for scalable IoT monitoring environments. Most of the evaluated JA4+ fingerprint families can be extracted passively without payload decryption and can be integrated into monitoring infrastructures using tools such as Zeek. Certificate-derived fingerprints constitute an exception when certificate messages are encrypted and no session keys are available. These characteristics make it suitable for asset inventory, continuous monitoring, anomaly detection, and Zero Trust architectures without compromising the confidentiality of application payloads.
However, the same characteristics that make passive fingerprinting attractive for network defense also raise important privacy concerns. Although JA4+ fingerprints do not expose application payloads or user data directly, they may still reveal the types of IoT devices operating within a monitored network. As a result, any entity capable of observing encrypted traffic—including Internet service providers, enterprise network administrators, or other monitoring entities—could potentially infer the composition of a user’s IoT ecosystem solely from protocol- and transport-layer metadata. This capability has a dual nature: it enables legitimate security and management applications, but it may also facilitate user profiling, reconnaissance activities, or targeted attacks against vulnerable device models. These observations highlight that improving confidentiality at the application layer does not necessarily eliminate information leakage through observable protocol metadata. In particular, ECH does not necessarily eliminate the possibility of fingerprint-based device inference based on other observable metadata [24]. Future protocol evolution should therefore seek an appropriate balance between preserving operational visibility for network defense and minimizing unintended metadata leakage.
An additional security consideration concerns the potential adversarial manipulation of JA4+ fingerprints. An attacker with sufficient control over the protocol and transport characteristics used to construct these fingerprints could attempt to reproduce fingerprints associated with legitimate IoT devices, thereby misleading fingerprint-based monitoring or identification systems. The present study considers non-adversarial traffic and does not evaluate the robustness of JA4+-based identification against such deliberate spoofing. Assessing this threat would require a dedicated adversarial model and controlled experiments evaluating the extent to which individual fingerprint components can be manipulated while preserving functional network communication.
A second, independently collected dataset was also analyzed using the same methodology. The same qualitative behavior was observed in both datasets: decomposed representations did not consistently outperform compact JA4+ fingerprints, providing additional evidence that the main observation is not specific to the CICIoT2023 traffic collection.
Overall, these results motivate further research on the robustness of JA4+-based identification against protocol evolution, fingerprint variability, and adversarial manipulation. In this context, the results indicate that compact JA4+ fingerprints already provide a practical balance between predictive performance, scalability, and deployment simplicity, while decomposed representations remain particularly valuable when interpretability and feature-level analysis are required.
8. Conclusions
This paper investigated the use of JA4+-based fingerprints for passive IoT device identification in encrypted network environments, where the progressive adoption of TLS 1.3, ECH, and other privacy-enhancing mechanisms continues reducing the availability of observable application-layer metadata.
The proposed methodology evaluated multiple JA4+ fingerprint combinations using dictionary-based matching, Random Forest, and CatBoost classifiers. Compact fingerprint representations were compared with decomposed protocol-level features using traffic derived from the CICIoT2023 dataset, and the main compact-versus-decomposed comparison was additionally evaluated using the independently collected UNSW-IoTraffic dataset.
The results show that JA4+-based fingerprints provide strong discriminative capabilities for IoT device identification without relying on payload inspection or SNI-related information. In the CICIoT2023 machine-learning experiments, the complete JA4+ fingerprint combination achieved the highest measured Macro F1-score, although this result must be interpreted together with its smaller support and the differing availability of the individual fingerprint families. Across the evaluated classifiers and datasets, decomposed protocol-level representations did not provide a consistent predictive advantage over compact fingerprints. Their main contribution instead lies in feature-level interpretability, since decomposition exposes the individual protocol attributes contributing to device discrimination.
The independent evaluation with the UNSW-IoTraffic dataset reproduced the same general compact-versus-decomposed behavior, while the repeated-partition experiments showed limited variability across the evaluated random train/test splits. The computational evaluation further showed that dictionary-based matching provides the lowest inference cost when exact matching is applicable, whereas CatBoost achieved lower inference latency than RF in the evaluated configurations. These additional experiments provide evidence that the main observations are not restricted to a single dataset, classifier, or data partition.
The main limitations concern the evaluation on only two IoT traffic datasets, the absence of cross-dataset model transfer and longitudinal experiments, and the dependence of some fingerprint families, particularly JA4X, on protocol version and metadata availability. The study also considers non-adversarial traffic and therefore does not evaluate deliberate fingerprint manipulation or device impersonation.
Future work should primarily investigate the temporal robustness of JA4+-based device identification under firmware updates, operating-system changes, and TLS-library evolution. Additional evaluation under malicious and adversarial traffic, as well as open-set scenarios involving previously unseen devices, would also help characterize the operational limits of the approach. Validation on further IoT datasets and additional classifier families could provide broader evidence regarding the generality of the observed behavior.
In conclusion, the results indicate that JA4+-based fingerprinting provides a promising approach for passive IoT device identification using observable transport- and protocol-layer metadata. As encrypted communications continue limiting network visibility, these techniques may contribute to IoT monitoring, asset identification, and security analysis under conditions where payload inspection is unavailable.
Author Contributions
Conceptualization, G.B.V. and J.E.L.d.V.; methodology, G.B.V. and J.E.L.d.V.; software, G.B.V.; validation, G.B.V. and J.E.L.d.V.; formal analysis, G.B.V.; investigation, G.B.V. and J.E.L.d.V.; resources, I.G., G.S. and L.d.P.; data curation, G.B.V.; writing—original draft preparation, G.B.V. and J.E.L.d.V.; writing—review and editing, I.G., G.S. and L.d.P.; visualization, G.B.V.; supervision, J.E.L.d.V.; project administration, J.E.L.d.V.; funding acquisition, J.E.L.d.V., I.G., G.S. and L.d.P. All authors have read and agreed to the published version of the manuscript.
Funding
This research was partially funded by an R&D activity program with reference TEC-2024/COM-504 and acronym RAMONES-CM, granted by the Comunidad de Madrid, Spain, through the Directorate General for Research and Technological Innovation via Order 5696/2024.
Data Availability Statement
Publicly available datasets were analyzed in this study. The CICIoT2023 dataset is available at: https://www.unb.ca/cic/datasets/iotdataset-2023.html . The UNSW-IoTraffic dataset is available at https://iotanalytics.unsw.edu.au/unsw-iotraffic.html . The software developed for the analysis is available at: https://github.com/gemmself/TFG_GemmaBeatrizVate .
Conflicts of Interest
The authors declare no conflicts of interest.
Abbreviations
The following abbreviations are used in this manuscript:
| AI | Artificial Intelligence |
| ALPN | Application-Layer Protocol Negotiation |
| CatBoost | Categorical Boosting |
| CI | Confidence Interval |
| CIC | Canadian Institute for Cybersecurity |
| DPI | Deep Packet Inspection |
| ECH | Encrypted Client Hello |
| HTTP | Hypertext Transfer Protocol |
| IoT | Internet of Things |
| JA3 | John Althouse, Jeff Atkinson, and Josh Atkins |
| JA4+ | John Althouse, Josh Atkins, Jeff Atkinson, and Joshua Alexander multiprotocol fingerprints |
| JA4 | JA4+ Client Hello fingerprint |
| JA4S | JA4+ Server Hello fingerprint |
| JA4T | JA4+ TCP fingerprint |
| JA4TS | JA4+ TCP Server fingerprint |
| JA4X | JA4+ X.509 certificate fingerprint |
| MD5 | Message Digest Algorithm 5 |
| MDI | Mean Decrease in Impurity |
| PCAP | Packet Capture |
| RF | Random Forest |
| RSS | Resident Set Size |
| SNI | Server Name Indication |
| SSH | Secure Shell |
| TCP | Transmission Control Protocol |
| TLS | Transport Layer Security |
| UNSW | University of New South Wales |
References
- IBM. What is the Internet of Things (IoT)? 2026. Available online: https://www.ibm.com/think/topics/internet-of-things (accessed on 15 May 2026).
- Solera-Cotanilla, S.; Álvarez Campana, M.; Sánchez-Zas, C.; Vega-Barbas, M. Proposal for a security and privacy enhancement system for private smart environments. Internet Things 2025, 31, 101585. [Google Scholar] [CrossRef]
- Internet Engineering Task Force (IETF). TLS Encrypted Client Hello (ECH). Available online: https://www.rfc-editor.org/info/rfc9849 (accessed on 15 May 2026).
- Cloudflare; Inc. What is Encrypted SNI (ESNI)? 2026. Available online: https://www.cloudflare.com/learning/ssl/what-is-encrypted-sni/ (accessed on 15 May 2026).
- Althouse, J.; Atkinson, J.; Atkins, J. TLS Fingerprinting with JA3 and JA3S. 2019. Available online: https://engineering.salesforce.com/tls-fingerprinting-with-ja3-and-ja3s-247362855967/ (accessed on 15 May 2026).
- FoxIO. ja4. 2024. Available online: https://github.com/FoxIO-LLC/ja4 (accessed on 12 April 2026).
- Althouse, J. JA4+ Network Fingerprinting. 2023. Available online: https://blog.foxio.io/ja4+-network-fingerprinting (accessed on 20 January 2025).
- Paracha, M.T.; Dubois, D.; Vallina-Rodriguez, N.; Choffnes, D. IoTLS: Understanding TLS Usage in Consumer IoT Devices. In Proceedings of the ACM Internet Measurement Conference, 2021. [Google Scholar]
- Siwakoti, Y.R.; Rawat, D.B. Detecting Malicious Traffic using JA3 Fingerprints Attributed ML Approach. In Proceedings of the 2024 IEEE 44th International Conference on Distributed Computing Systems Workshops (ICDCSW), 2024. [Google Scholar] [CrossRef]
- Llano-Miraval, J.D.; Campo, C.; Garcia-Rubio, C.; Moure-Garrido, M. AI Versus IoT Security: Fingerprinting and Defenses Against TLS Handshake-Based IoT Device Classification. IEEE Access, 2025. [Google Scholar]
- Neto, E.C.P.; Dadkhah, S.; Ferreira, R.; Zohourian, A.; Lu, R.; Ghorbani, A. CICIoT2023: A Real-Time Dataset and Benchmark for Large-Scale Attacks in IoT Environment. Sensors 2023, 23. [Google Scholar] [CrossRef]
- Zeek Project. Zeek Network Security Monitor. 2026. Available online: https://zeek.org/ (accessed on 15 May 2026).
- Fan, M.; Gao, J.; He, Y.; Shi, W.; Lu, Y. Traffic Fingerprints for Homogeneous IoT Traffic Based on Packet Payload Transition Patterns. Electronics 2024, 13, 930. [Google Scholar] [CrossRef]
- Amamra, A.; Anunwah, J.C.; Louafi, H. IoT Device Fingerprinting via Frequency Domain Analysis. Electronics 2025, 14, 3248. [Google Scholar] [CrossRef]
- Jiang, Y.; Dou, Y.; Hu, A. Identification of IoT Devices Based on Hardware and Software Fingerprint Features. Symmetry 2024, 16, 846. [Google Scholar] [CrossRef]
- FoxIO. JA4T: TCP Fingerprinting. 2024. Available online: https://blog.foxio.io/ja4t-tcp-fingerprinting (accessed on 1 February 2026).
- Adrović, H. Enhancing Smart Home Security through IoT Device Fingerprinting Using Machine Learning. PhD thesis, Mälardalen University, 2025. [Google Scholar]
- Hysi, S. IoT Device Fingerprinting using ESP32 System-on-Chip. Master’s Thesis, Vienna University of Technology, 2026. [Google Scholar]
- Burgetová, I.; Matoušek, P.; Ryšavý, O. Towards Identification of Network Applications in Encrypted Traffic. Ann. Telecommun. 2025, 80, 1015–1032. [Google Scholar] [CrossRef]
- Fernández-Terrasa, M.; López de Vergara, J.E.; Gómez-Arribas, F.J.; de Pedro, L.; González, I. Mobile Application Identification in Encrypted Traffic Using JA4+ Fingerprints. In Proceedings of the 4th International Conference on Computing, IoT and Data Analytics (ICCIDA 2025), Madrid, Spain, July 2025. [Google Scholar]
- Matoušek, P.; Ryšavý, O.; Burgetová, I. Experience Report: Using JA4+ Fingerprints for Malware Detection in Encrypted Traffic. In Proceedings of the 20th International Conference on Network and Service Management (CNSM), Prague, Czech Republic, 2024; pp. 1–5. [Google Scholar] [CrossRef]
- Polo-Peyres, E.; López de Vergara, J.E.; Sutter, G.; González, I.; de Pedro, L. Detecting Malware in Encrypted Network Traffic Using Machine Learning and TLS Fingerprints. In Proceedings of the 17th International Conference on Ubiquitous Computing and Ambient Intelligence (UCAmI 2025), Lecture Notes in Networks and Systems. Best paper award. Prato, Italy, November 2025; Vol. 1819. [Google Scholar] [CrossRef]
- Wannigama, S.; Sivanathan, A.; Gharakheili, H.H. Descriptor: UNSW IoT Traffic Data With Packets, Flows, and Protocols (UNSW-IoTraffic). IEEE Data Descr. 2025, 2, 311–323. [Google Scholar] [CrossRef]
- Rezaei, F.; López de Vergara, J.E.; de Pedro, L.; González, I. Encrypted but Not Private: Application Identification from Traffic Metadata at Scale. In Proceedings of the XI Jornadas Nacionales de Investigación en Ciberseguridad (JNIC 2026), Barcelona, Spain, 8 May 2026; 2026; pp. 52–55. 6. [Google Scholar] [CrossRef]
Short Biography of Authors
 |
Gemma B. VATE has been a data security engineer at GMV (Spain) since 2025, specializing in cybersecurity infrastructure through the deployment, configuration, migration, and management of core enterprise protection systems, including Web Application Firewalls (WAF) and Data Activity Monitoring (DAM) solutions. She received her B.Sc. in Computer Engineering (bilingual degree) in 2026 from Universidad Autónoma de Madrid (Spain). Her research interests include network and application security, threat detection, security monitoring, and the application of data-driven techniques to enhance network visibility and cybersecurity solutions. |
 |
Jorge E. LÓPEZ DE VERGARA has held various academic positions at Universidad Autónoma de Madrid (Spain) since 2003, becoming full professor in 2025. He was a founding partner of Naudit HPCN, a spin-off company devoted to high-performance traffic monitoring and analysis, from 2009 to 2023. He is currently a founding partner of Qarina HPC, another spin-off company focused on quantum computing and artificial intelligence. He received the M.Sc. (Hons.) and Ph.D. degrees in Telecommunication Engineering from Universidad Politécnica de Madrid (Spain) in 1998 and 2003, respectively, where he also held an FPU-MEC research grant. During his Ph.D., he spent six months at HP Labs in Bristol, U.K., in 2000. His research interests include network and service management and monitoring, and he has coauthored more than 200 scientific publications in these areas. |
 |
Iván GONZÁLEZ received his M.Sc. degree in Computer Engineering in 2000 and his Ph.D. in Computer Engineering in 2006, both from UAM, Spain. From October 2002 to October 2006, he was a teaching assistant at the Computer Engineering Department of UAM. From November 2006 to January 2008, he was a postdoctoral research scientist at the High-Performance Computing Laboratory (HPCL), Electrical & Computer Engineering Department, GeorgeWashington University (Washington, DC). He was a faculty member of the NSF Center of High-Performance Reconfigurable Computing (CHREC) at George Washington University. He is currently an associate professor at UAM, where he is teaching computer-architecture-related courses. He was also a partner of Naudit HPCN. His main research interests are heterogeneous computing (with GPUs, FPGAs, etc.), parallel algorithms, and performance tuning. Other interests include big data, machine learning and data analytics. |
 |
Gustavo SUTTER received an M.Sc. degree in Computer Science from State University UNCPBA of Tandil (Buenos Aires) Argentina, in 1997, and a Ph.D. degree from the Autonomous University of Madrid, Spain, in 2005. He was a professor at UNCPBA, Argentina, and is currently an associate professor at Universidad Autónoma de Madrid, Spain. His research interests include FPGA design, digital arithmetic, development of embedded systems and highperformance computing. He is the author of three books and more than a hundred international papers and communications. |
 |
Luis de PEDRO has been an associate professor at Universidad Autónoma de Madrid (Spain) since 1994. He was a Hewlett-Packard Executive from 1986 to 2019. He was also president and founding partner of Naudit HPCN from 2009 to 2023, a UAM spin-off devoted to high-performance traffic monitoring and analysis. He is currently a founding partner of Qarina HPC, another spinoff company devoted to quantum computing and artificial intelligence. He received his M.Sc. (Honors) and Ph.D. (Honors) degrees in Telecommunication Engineering from Universidad Politécnica de Madrid (Spain) in 1987 and 1992, respectively. His current research focuses on statistical models for network traffic. |
Figure 1.
Example of JA4 fingerprint structure and decomposition into protocol-level components for Amazon Alexa Echo Dot.
Figure 1.
Example of JA4 fingerprint structure and decomposition into protocol-level components for Amazon Alexa Echo Dot.
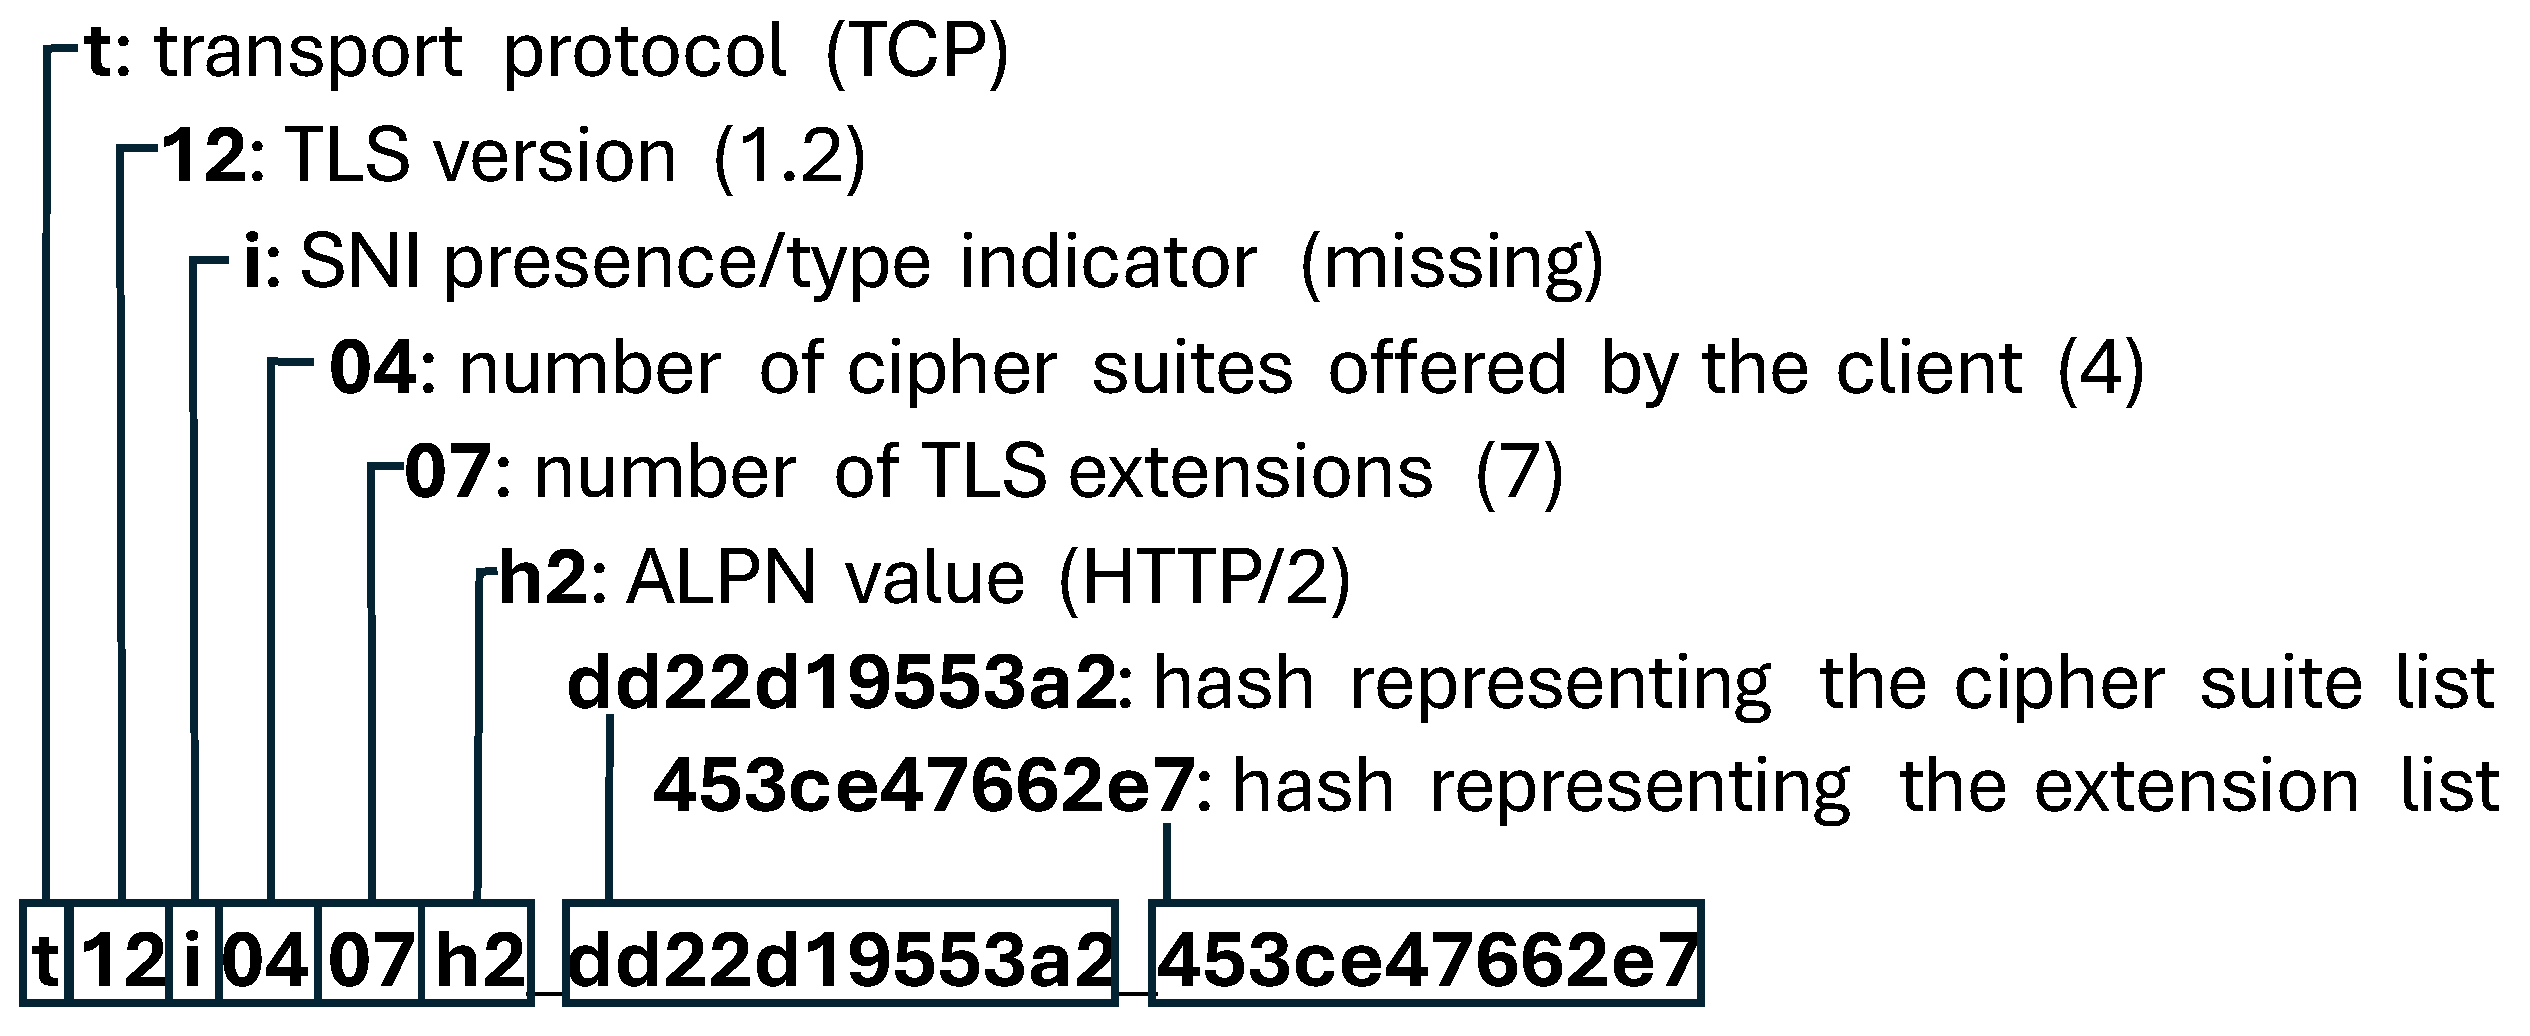
Figure 2.
Overview of the experimental pipeline used for encrypted IoT traffic classification.
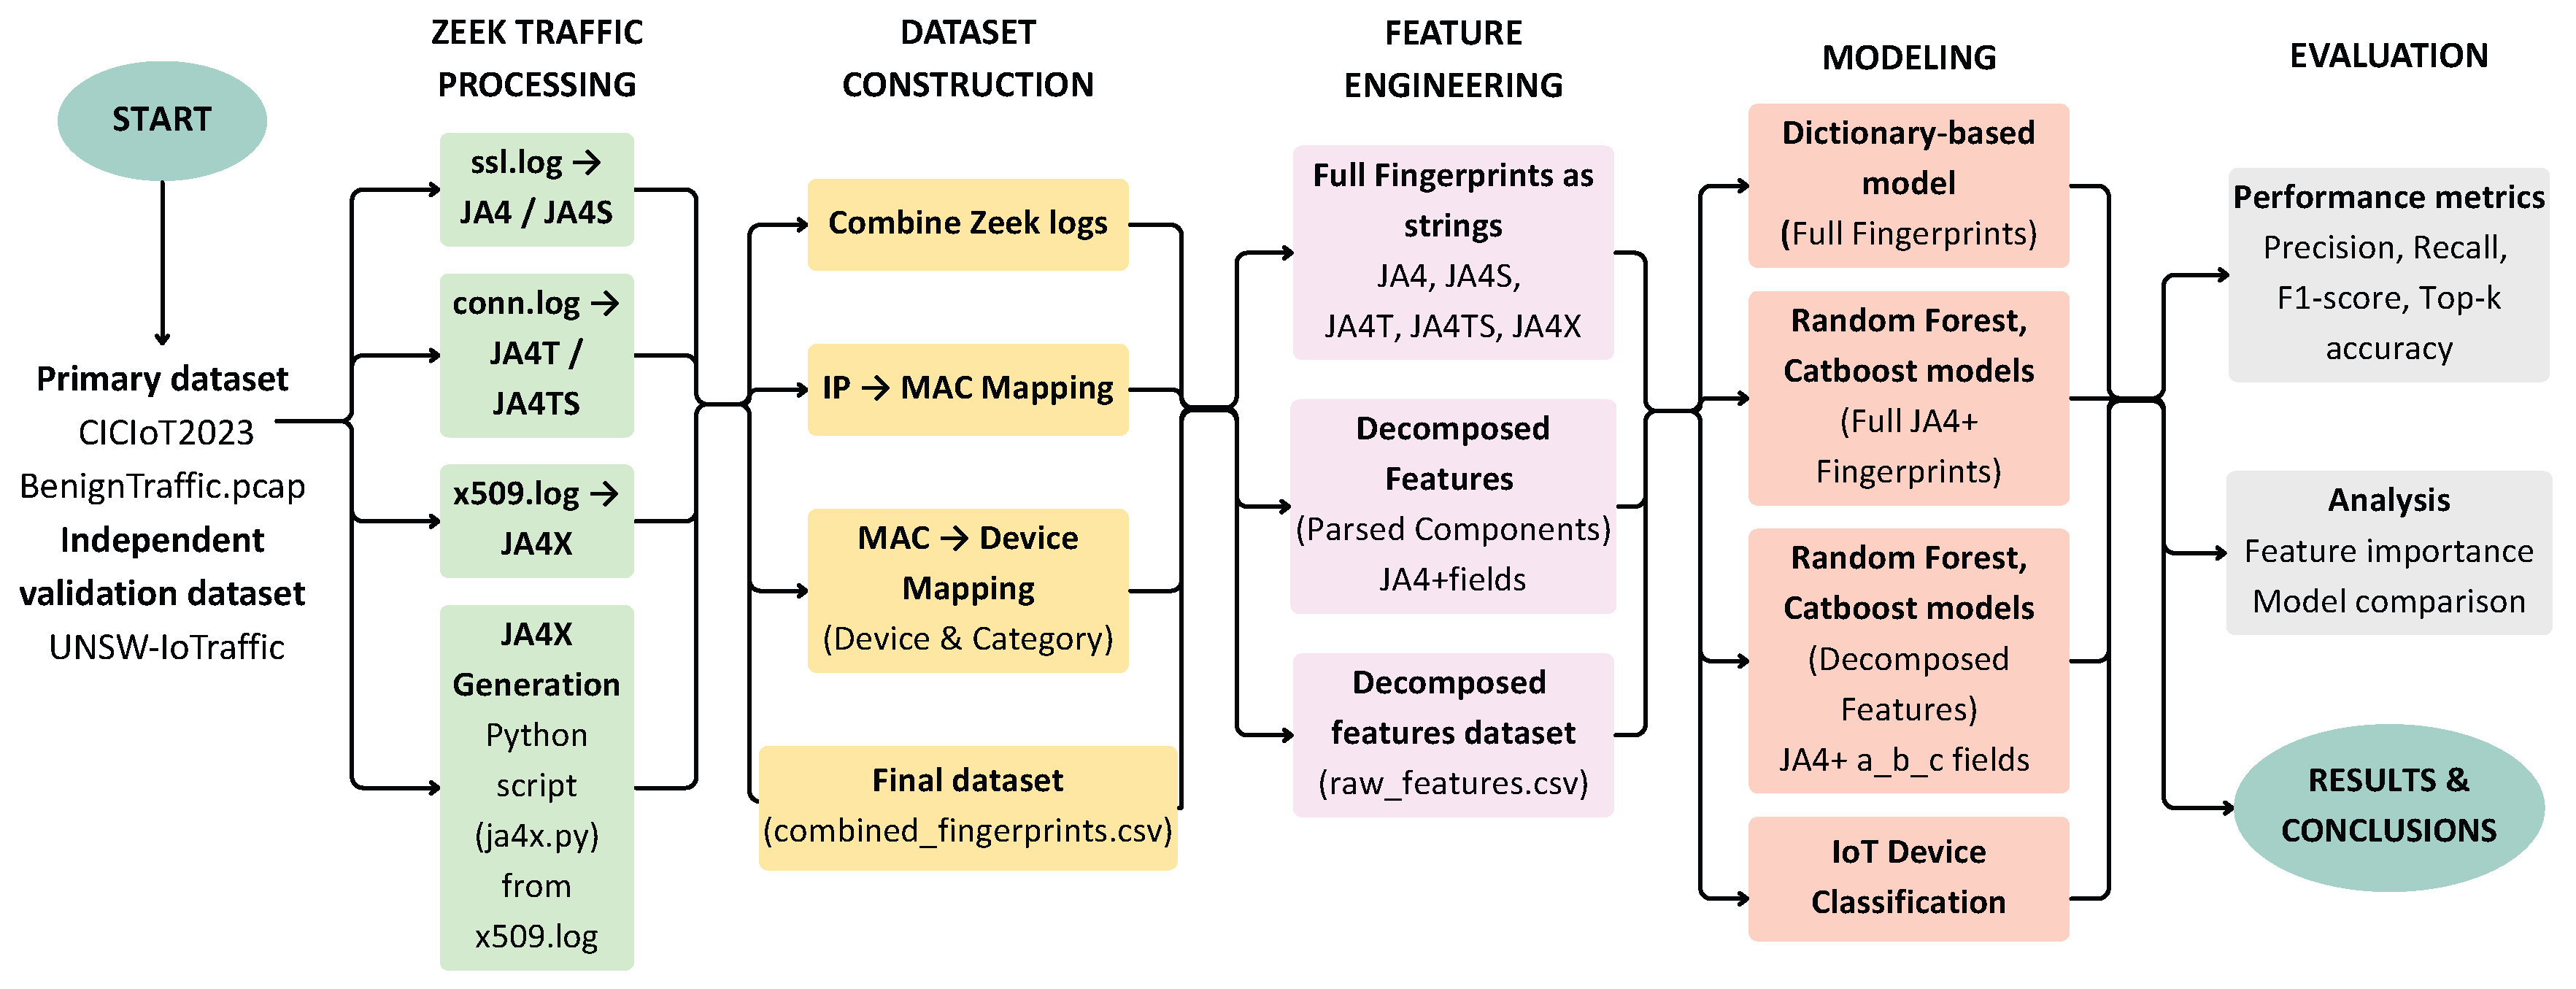
Figure 3.
Number of JA4+JA4S fingerprints across IoT device categories. Total number per device (above) and distinct fingerprints per device (below).
Figure 3.
Number of JA4+JA4S fingerprints across IoT device categories. Total number per device (above) and distinct fingerprints per device (below).
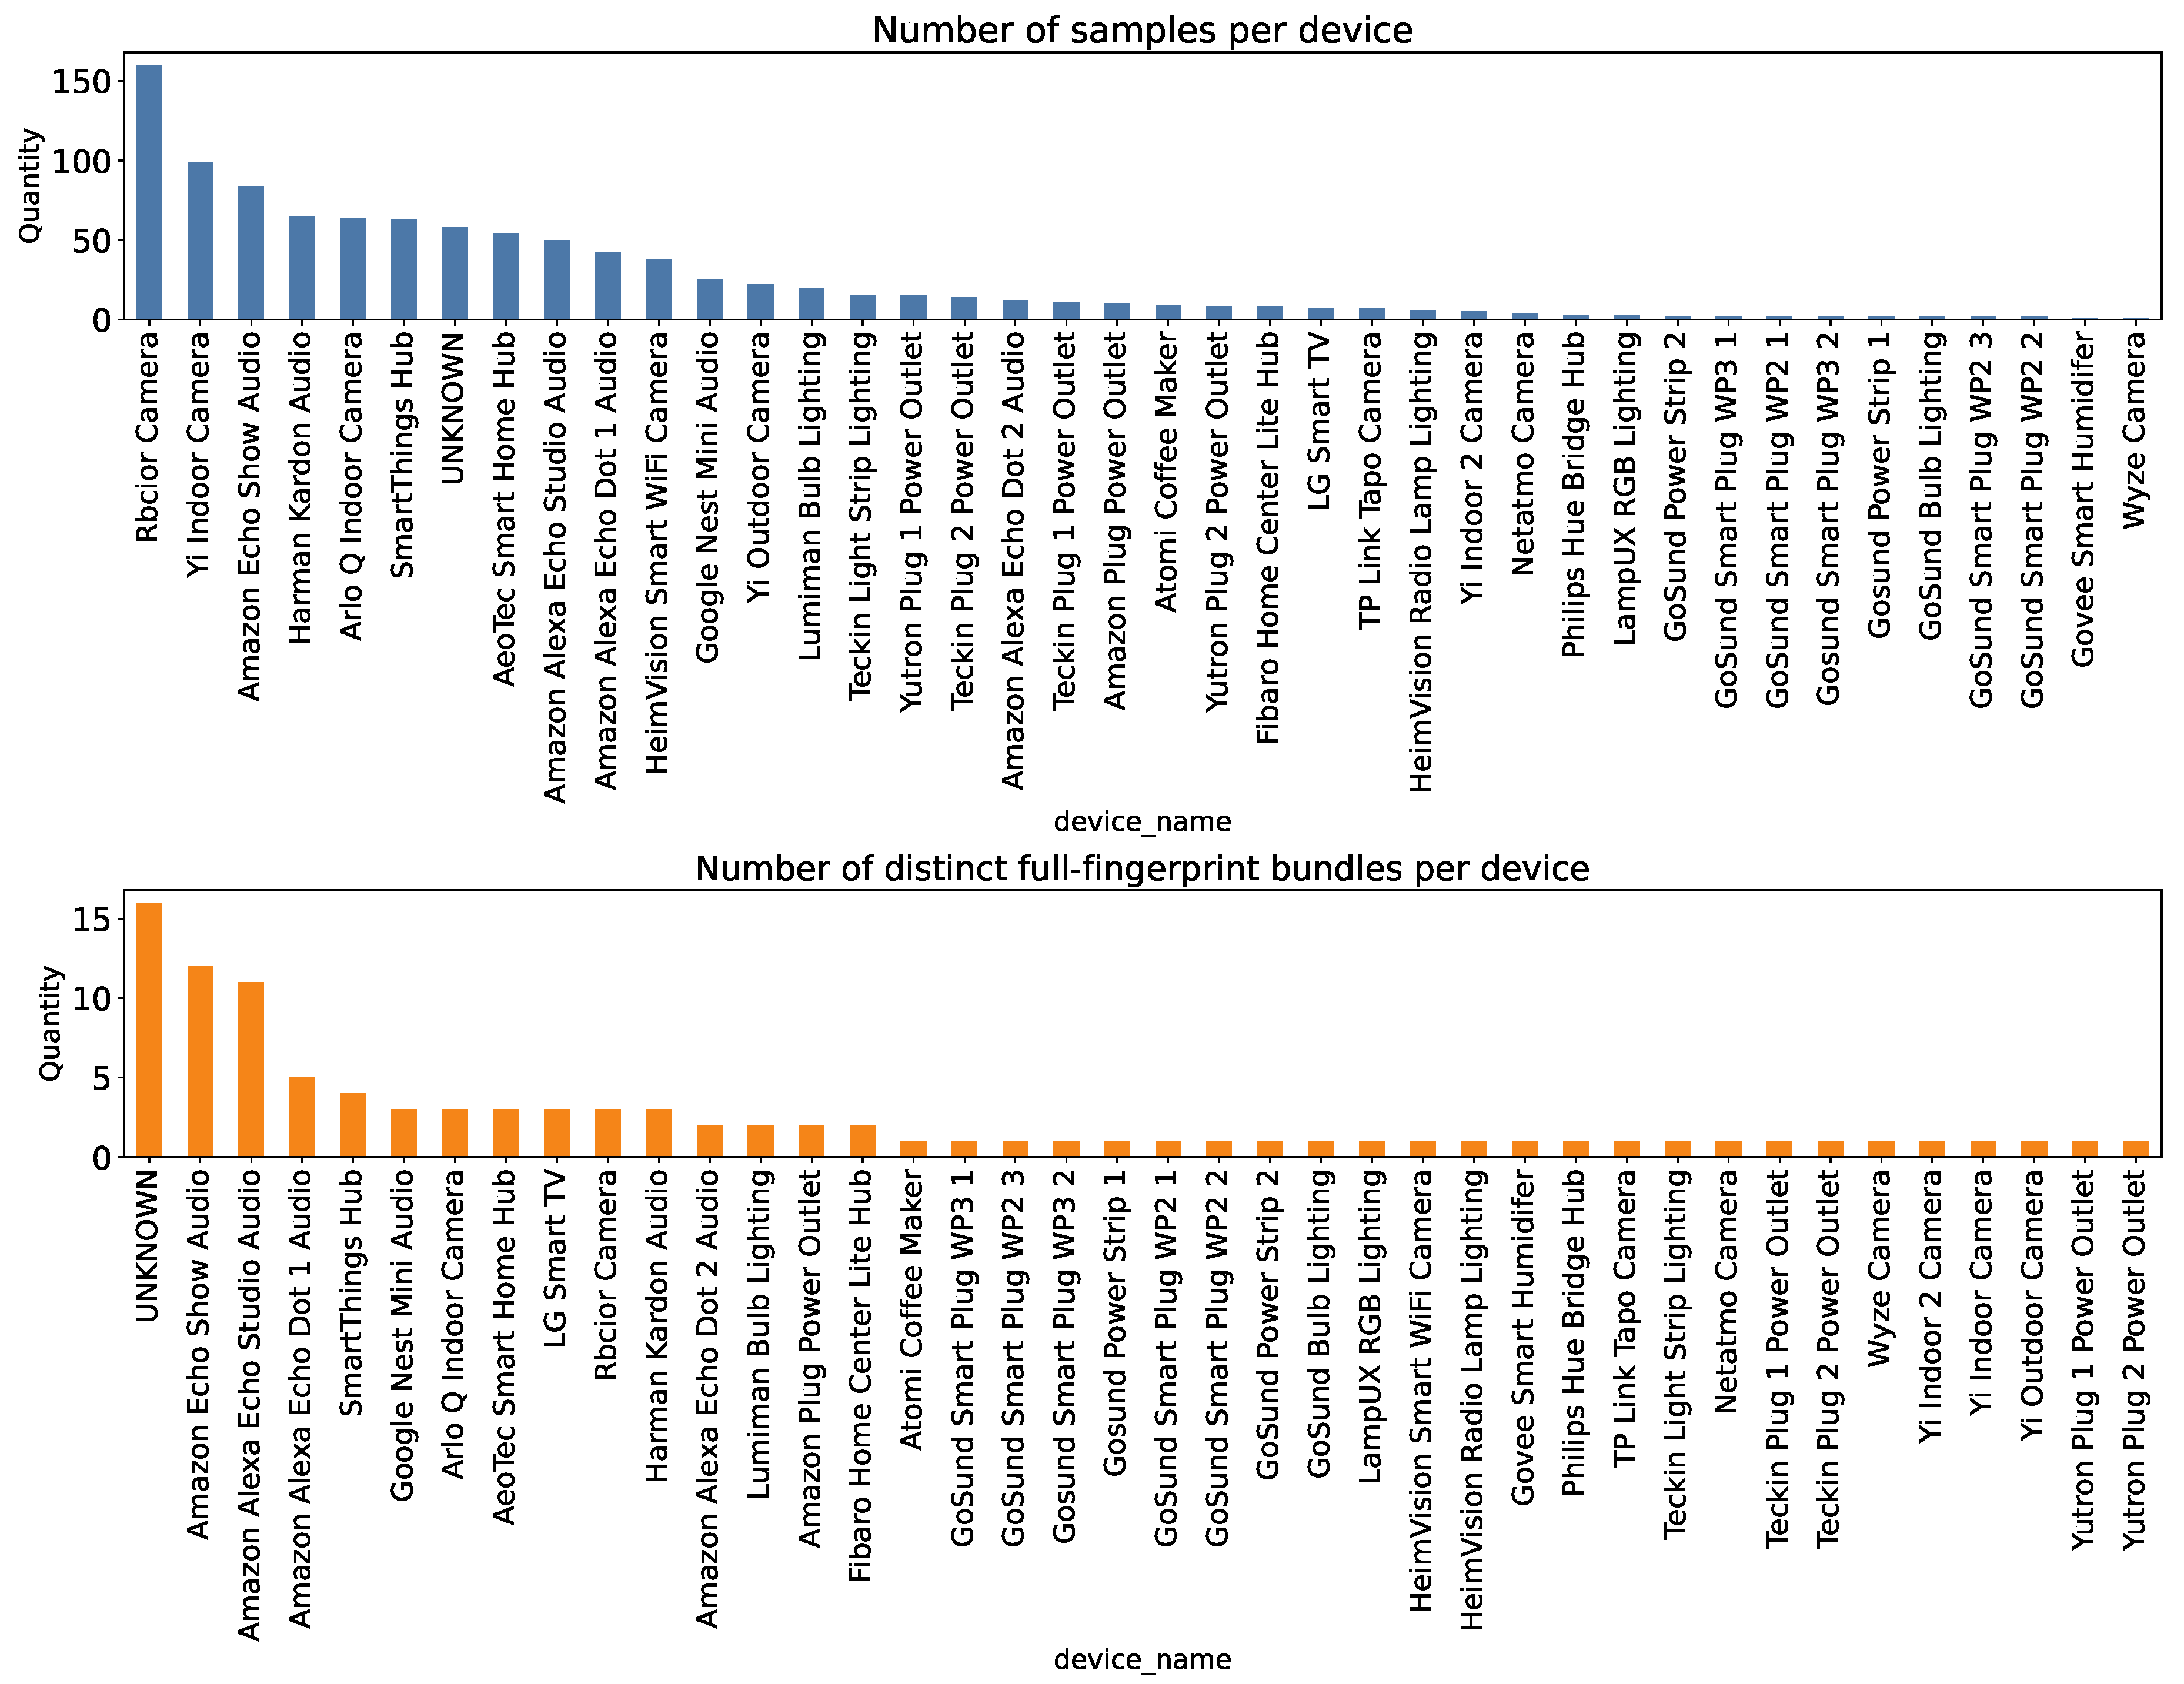
Figure 4.
Confusion matrix obtained for the evaluated Random Forest classifier with decomposed features.
Figure 4.
Confusion matrix obtained for the evaluated Random Forest classifier with decomposed features.
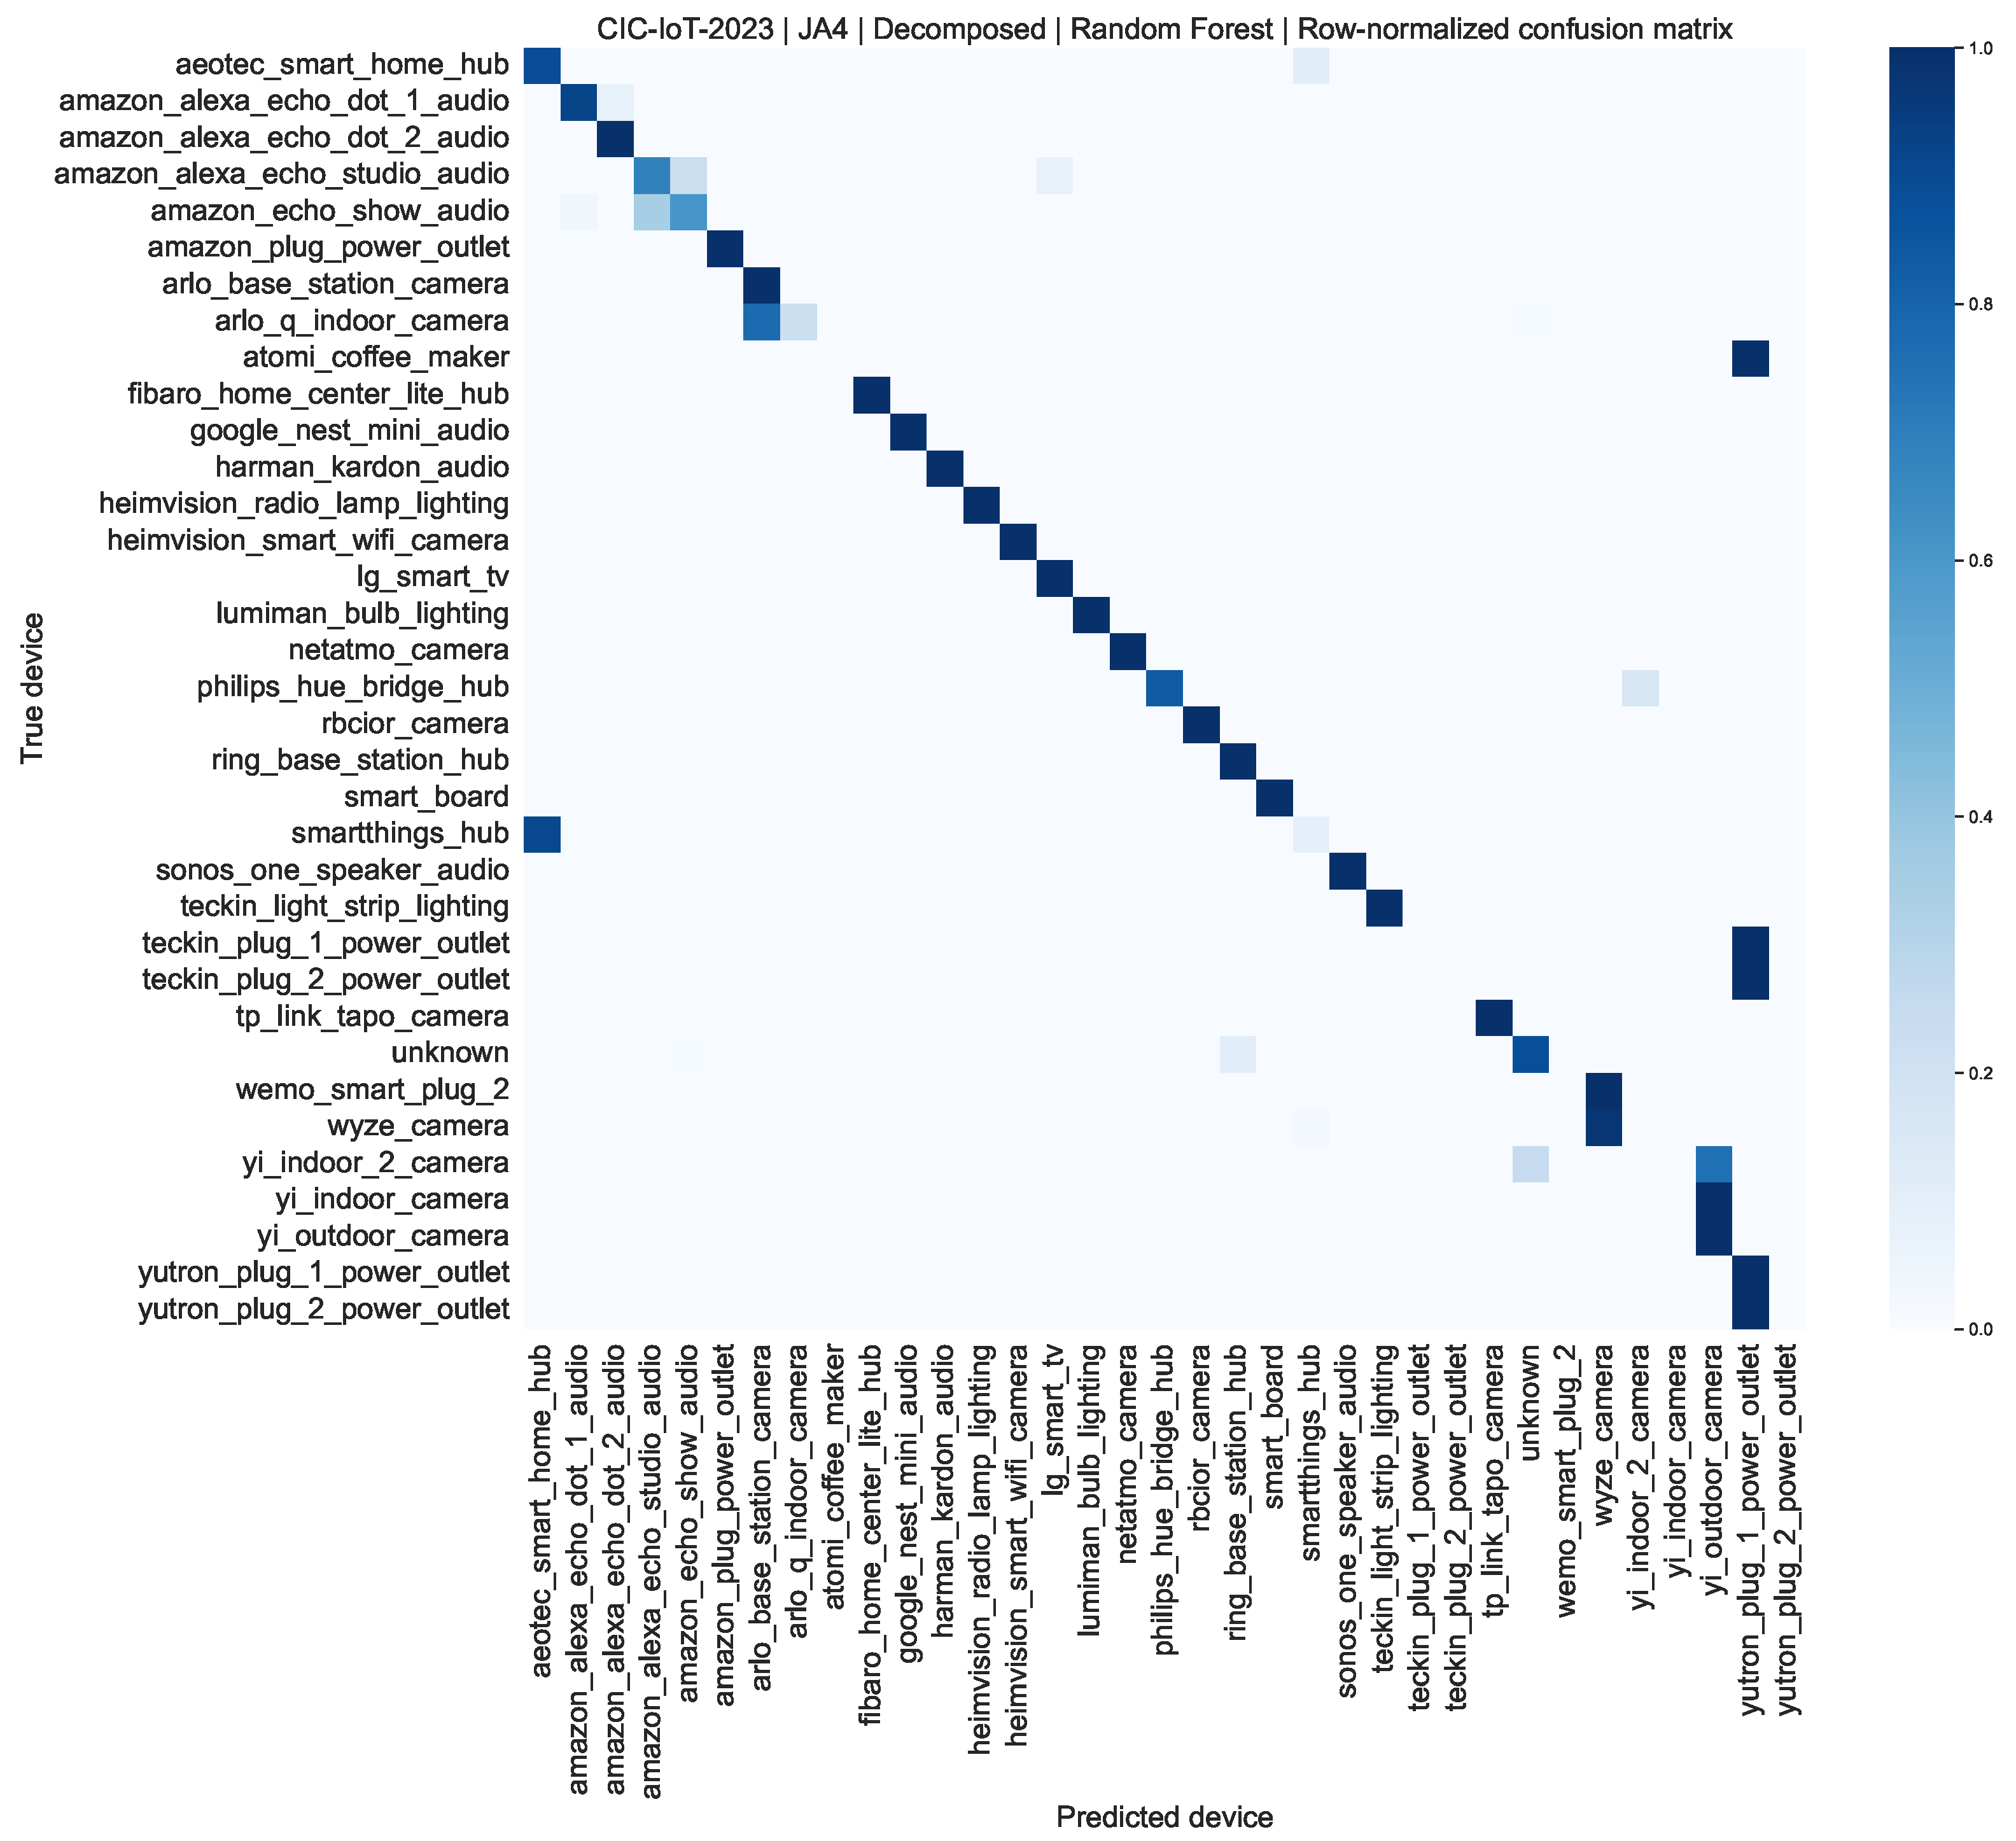
Figure 5.
Feature importance ranking obtained from the Random Forest classification model.
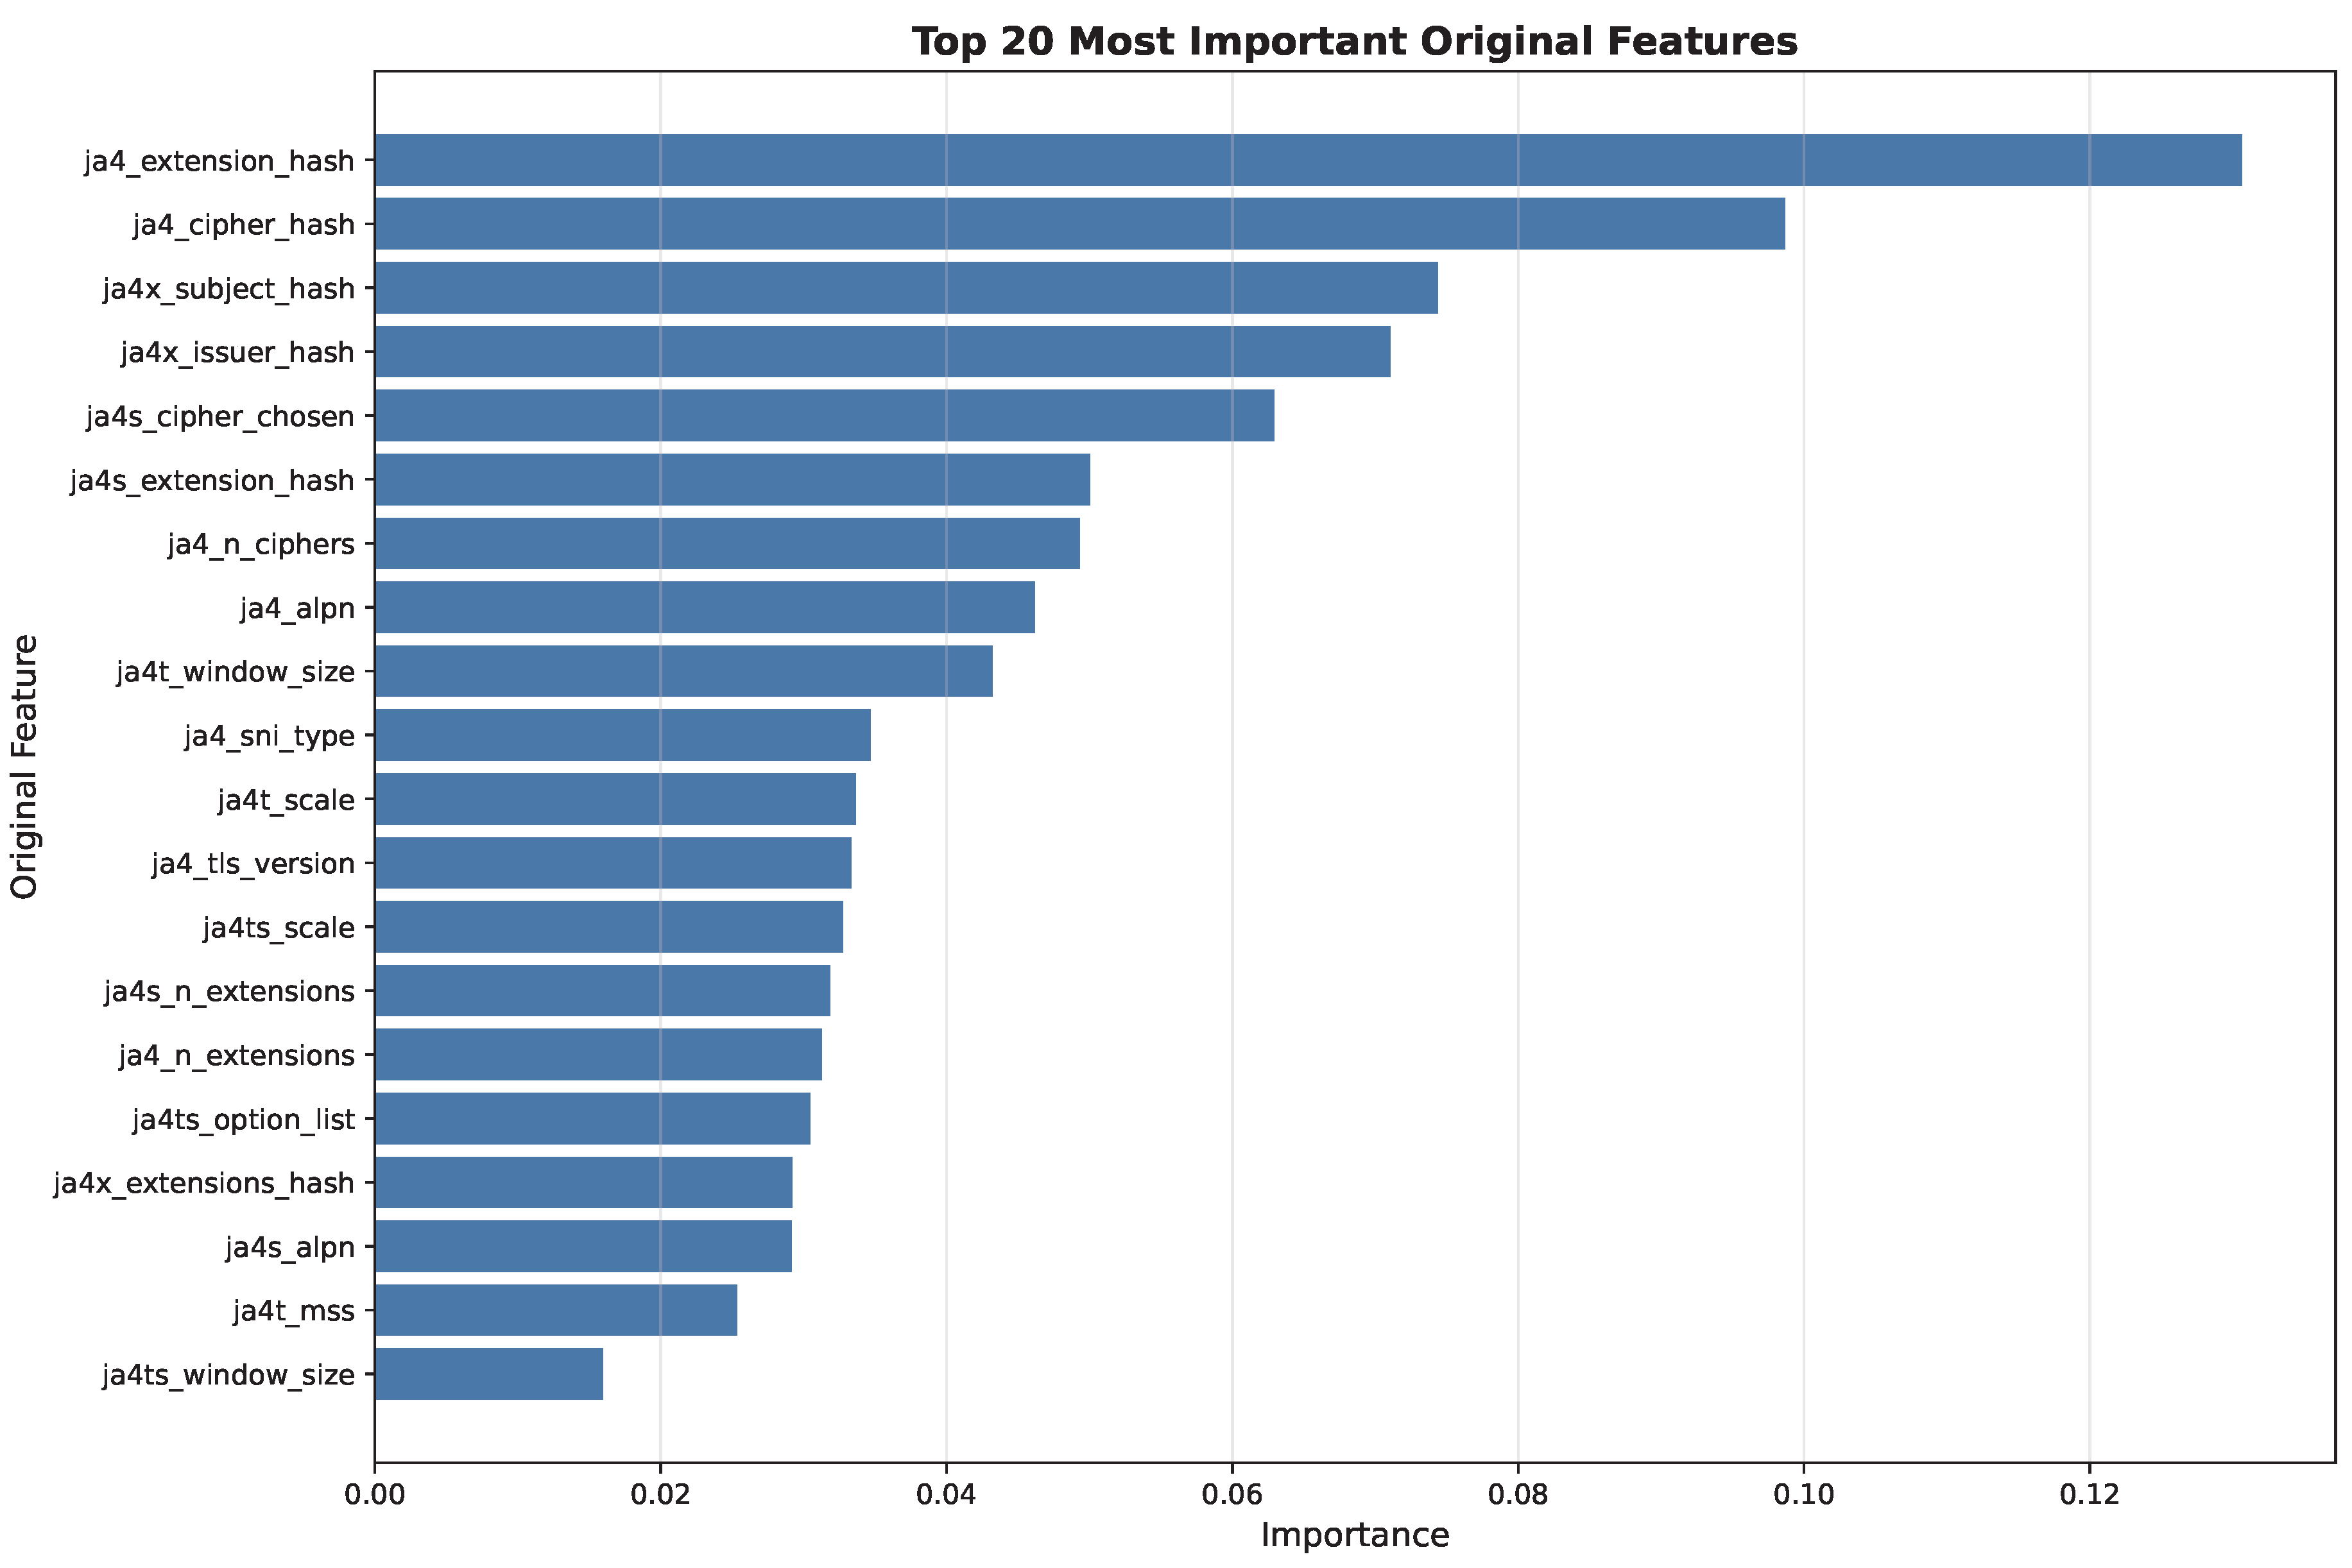
Table 1.
Comparison between JA3 and JA4+ fingerprinting approaches.
| Feature | JA3 | JA4+ |
|---|---|---|
| TLS metadata support | Yes | Yes |
| TCP metadata integration | No | Yes |
| Human-readable structure | Limited | Improved |
| Fingerprint decomposition | Limited | Supported |
| Resistance to randomization | Moderate | Improved |
| Interpretability | Low | Higher |
Table 2.
Summary of the dataset and extracted fingerprint information used during the experiments.
| Parameter | Description |
|---|---|
| Dataset | CICIoT2023 |
| Traffic type | Encrypted TLS traffic |
| Extraction tool | Zeek, Python scripts |
| Fingerprints | JA4+, JA4S, JA4T, JA4TS, JA4X |
| Classification methods | Dictionary, Random Forest, CatBoost |
| Feature strategies | Complete and decomposed |
Table 3.
Class-filtering audit for CIC-IoT-2023 (capture period: 2022-10-07 to 2022-10-08). Initial dataset samples = 162 362; initial classes = 52 for all experiments.
Table 3.
Class-filtering audit for CIC-IoT-2023 (capture period: 2022-10-07 to 2022-10-08). Initial dataset samples = 162 362; initial classes = 52 for all experiments.
| Experiment | Valid Samples | Samples After Filter | Trained Classes | Excluded Classes |
|---|---|---|---|---|
| JA4 | 24 722 | 6 532 | 35/52 | 17 |
| JA4+* | 103 | 93 | 7/52 | 45 |
| JA4S | 999 | 971 | 27/52 | 25 |
| JA4T | 401 | 376 | 18/52 | 34 |
| JA4TS | 401 | 376 | 18/52 | 34 |
| JA4X | 323 | 306 | 10/52 | 42 |
Table 4.
Excluded device classes (fewer than 5 samples) in the CIC-IoT-2023 dataset for the JA4+* experiment.
Table 4.
Excluded device classes (fewer than 5 samples) in the CIC-IoT-2023 dataset for the JA4+* experiment.
| Excluded Device Class | Valid Samples |
|---|---|
| Fibaro_Home_Center_Lite_Hub | 0 |
| Google_Nest_Mini_Audio | 0 |
| UNKNOWN | 2 |
| Yi_Indoor_2_Camera | 0 |
| AMCREST_WiFi_Camera | 0 |
| SmartThings_Hub | 3 |
| Wyze_Camera | 0 |
| Netatmo_Camera | 0 |
| Amazon_Alexa_Echo_Studio_Audio | 1 |
| AeoTec_Smart_Home_Hub | 1 |
| Sonos_One_Speaker_Audio | 0 |
| Arlo_Q_Indoor_Camera | 1 |
| TP_Link_Tapo_Camera | 0 |
| Eufy_HomeBase_2_Hub | 0 |
| Arlo_Base_Station_Camera | 0 |
| Philips_Hue_Bridge_Hub | 0 |
| Wemo_smart_plug_2 | 0 |
| Raspberry_Pi_4_8_GB_Attacker | 0 |
| Yutron_Plug_1_Power_Outlet | 0 |
| Amazon_Alexa_Echo_Dot_1_Audio | 1 |
| HeimVision_Radio_Lamp_Lighting | 0 |
| Raspberry_Pi_4_2_GB | 0 |
| Raspberry_Pi_NextGen | 0 |
| Yutron_Plug_2_Power_Outlet | 0 |
| Teckin_Plug_1_Power_Outlet | 0 |
| Lumiman_Bulb_Lighting | 0 |
| Atomi_Coffee_Maker | 0 |
| Teckin_Plug_2_Power_Outlet | 0 |
| Amazon_Plug_Power_Outlet | 0 |
| Teckin_Light_Strip_Lighting | 0 |
| Ring_Base_Station_Hub | 0 |
| DCS8000LHA1_D_Link_Mini_Camera | 0 |
| Govee_Smart_Humidifer | 1 |
| GoSund_Smart_Plug_WP2_3 | 0 |
| GoSund_Smart_Plug_WP3_1 | 0 |
| Gosund_Smart_Plug_WP3_2 | 0 |
| GoSund_Smart_Plug_WP2_2 | 0 |
| GoSund_Smart_Plug_WP2_1 | 0 |
| Gosund_Power_Strip_1 | 0 |
| Smart_Board | 0 |
| GoSund_Bulb_Lighting | 0 |
| LampUX_RGB_Lighting | 0 |
| GoSund_Power_Strip_2 | 0 |
| LG_Smart_TV | 0 |
| Nest_Indoor_Camera | 0 |
Table 5.
Evaluated fingerprint representations and associated feature extraction strategies.
| Representation | Description | Type |
|---|---|---|
| JA4 | TLS client fingerprint | Compact |
| JA4S | TLS server fingerprint | Compact |
| JA4T | TCP client fingerprint | Compact |
| JA4TS | TCP server fingerprint | Compact |
| JA4X | Certificate fingerprint | Compact |
| JA4+* | Combination of JA4+JA4S+JA4T+JA4TS+JA4X | Compact |
| Decomposed JA4+ | Protocol-level components | Decomposed |
Table 6.
Protocol-level characteristics extracted from each JA4+ fingerprint family.
| Fingerprint | No. of features | Extracted features |
|---|---|---|
| JA4 | 8 | Protocol, TLS version, SNI presence/type indicator, cipher count, extension count, ALPN, cipher hash, extension hash |
| JA4S | 6 | Protocol, TLS version, extension count, ALPN, selected cipher, extension hash |
| JA4X | 3 | Issuer hash, subject hash, extensions hash |
| JA4T/JA4TS | 8 | Window size, TCP option list, MSS, window scale, number of options, timestamp flag, SACK flag, window scale flag |
Table 7.
Evaluation metrics used during the experimental analysis.
| Metric | Description |
|---|---|
| Accuracy | Overall classification accuracy |
| Precision | Positive prediction reliability |
| Recall | Detection capability |
| Macro F1-score | Balanced precision-recall evaluation |
| Top-1 Accuracy | Correct first prediction rate |
| Top-3 Accuracy | Correct prediction within top 3 candidates |
| Top-5 Accuracy | Correct prediction within top 5 candidates |
Table 8.
Classification results obtained using different JA4+ fingerprint representations and classification methodologies. The 95% confidence interval (CI) for the Macro F1-score was estimated using bootstrap resampling.
Table 8.
Classification results obtained using different JA4+ fingerprint representations and classification methodologies. The 95% confidence interval (CI) for the Macro F1-score was estimated using bootstrap resampling.
| Model | Features | Macro F1 [95% CI] | Top-1 | Top-3 | Top-5 | Support |
|---|---|---|---|---|---|---|
| Dictionary | JA4 | 0.6461 [0.6309, 0.6749] | 0.8189 | 0.8289 | 0.8395 | 6 532 |
| Dictionary | JA4 + JA4S | 0.6520 [0.5883, 0.7290] | 0.8020 | 0.8119 | 0.8416 | 971 |
| Dictionary | JA4 + JA4X | 0.6508 [0.4848, 0.8236] | 0.8095 | 0.9048 | 0.9048 | 306 |
| Dictionary | JA4 + JA4S + JA4TS | 0.5536 [0.4583, 0.6710] | 0.7952 | 0.8554 | 0.8795 | 376 |
| Dictionary | JA4 + JA4S + JA4T + JA4TS | 0.5536 [0.4583, 0.6710] | 0.7952 | 0.8554 | 0.8795 | 376 |
| Dictionary | JA4+* | 0.6508 [0.4848, 0.8236] | 0.8095 | 0.9048 | 0.9048 | 93 |
| RF (Compact) | JA4 | 0.6122 [0.5921, 0.6298] | 0.6722 | 0.9681 | 0.9772 | 6 532 |
| RF (Compact) | JA4 + JA4S | 0.6506 [0.5916, 0.7141] | 0.8069 | 0.9703 | 0.9950 | 971 |
| RF (Compact) | JA4 + JA4X | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 306 |
| RF (Compact) | JA4 + JA4S + JA4TS | 0.6528 [0.5764, 0.7671] | 0.8675 | 0.9518 | 0.9880 | 376 |
| RF (Compact) | JA4 + JA4S + JA4T + JA4TS | 0.6577 [0.5867, 0.7661] | 0.8675 | 0.9639 | 1.0000 | 376 |
| RF (Compact) | JA4+* | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 93 |
| CatBoost (Compact) | JA4 | 0.6201 [0.5998, 0.6374] | 0.6821 | 0.9871 | 0.9970 | 6 532 |
| CatBoost (Compact) | JA4 + JA4S | 0.6480 [0.5919, 0.7105] | 0.8020 | 0.9653 | 0.9950 | 971 |
| CatBoost (Compact) | JA4 + JA4X | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 306 |
| CatBoost (Compact) | JA4 + JA4S + JA4TS | 0.6429 [0.5556, 0.7502] | 0.8554 | 0.9518 | 0.9880 | 376 |
| CatBoost (Compact) | JA4 + JA4S + JA4T + JA4TS | 0.6478 [0.5666, 0.7519] | 0.8554 | 0.9639 | 1.0000 | 376 |
| CatBoost (Compact) | JA4+* | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 93 |
| RF (Decomposed) | JA4 | 0.6486 [0.6306, 0.6783] | 0.7407 | 0.9894 | 0.9970 | 6 532 |
| RF (Decomposed) | JA4 + JA4S | 0.6481 [0.5889, 0.7120] | 0.8020 | 0.9703 | 1.0000 | 971 |
| RF (Decomposed) | JA4 + JA4X | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 306 |
| RF (Decomposed) | JA4 + JA4S + JA4TS | 0.6231 [0.5231, 0.7500] | 0.8554 | 0.9398 | 0.9759 | 376 |
| RF (Decomposed) | JA4 + JA4S + JA4T + JA4TS | 0.6263 [0.5262, 0.7500] | 0.8554 | 0.9398 | 0.9880 | 376 |
| RF (Decomposed) | JA4+* | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 93 |
| CatBoost (Decomposed) | JA4 | 0.6094 [0.5830, 0.6295] | 0.6852 | 0.9871 | 0.9977 | 6 532 |
| CatBoost (Decomposed) | JA4 + JA4S | 0.6475 [0.5894, 0.7102] | 0.8020 | 0.9653 | 1.0000 | 971 |
| CatBoost (Decomposed) | JA4 + JA4X | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 306 |
| CatBoost (Decomposed) | JA4 + JA4S + JA4TS | 0.6243 [0.5277, 0.7337] | 0.8434 | 0.9398 | 0.9759 | 376 |
| CatBoost (Decomposed) | JA4 + JA4S + JA4T + JA4TS | 0.6164 [0.5130, 0.7314] | 0.8434 | 0.9398 | 0.9759 | 376 |
| CatBoost (Decomposed) | JA4+* | 0.8095 [0.6667, 1.0000] | 0.9048 | 1.0000 | 1.0000 | 93 |
Table 9.
Computational performance of the evaluated classification approaches on CICIoT2023 for the JA4-only and JA4+* fingerprint configurations.
Table 9.
Computational performance of the evaluated classification approaches on CICIoT2023 for the JA4-only and JA4+* fingerprint configurations.
| Representation | Method | Training (s) | Inference (ms/sample) | Throughput (samples/s) | Memory (MB) |
|---|---|---|---|---|---|
| JA4-only experiment | |||||
| Compact | Dictionary | 0.090 | 0.0067 | 149 387.68 | 1.000 |
| Compact | RF | 10.714 | 0.0924 | 10 826.41 | 12.941 |
| Compact | CatBoost | 13.497 | 0.0260 | 38 456.25 | 37.297 |
| Decomposed | RF | 2.317 | 0.1145 | 8 736.21 | 12.000 |
| Decomposed | CatBoost | 40.210 | 0.0752 | 13 294.95 | 36.937 |
| JA4+* experiment | |||||
| Compact | Dictionary | 0.015 | 0.0790 | 12 656.70 | 1.000 |
| Compact | RF | 5.299 | 2.9354 | 340.67 | 5.000 |
| Compact | CatBoost | 0.686 | 0.3449 | 2 899.27 | 8.430 |
| Decomposed | RF | 1.608 | 4.5542 | 219.57 | 5.000 |
| Decomposed | CatBoost | 1.581 | 0.3797 | 2 633.49 | 9.879 |
Table 10.
Classification performance obtained applying Random Forest to a reduced feature subsets of the CICIoT2023 dataset.
Table 10.
Classification performance obtained applying Random Forest to a reduced feature subsets of the CICIoT2023 dataset.
| Combination | Available Features |
Selected Features |
Macro F1 | Top-1 Accuracy |
|---|---|---|---|---|
| JA4 | 8 | 5 | 0.6469 | 0.7407 |
| JA4 + JA4S | 14 | 8 | 0.6778 | 0.8119 |
| JA4 + JA4X | 11 | 8 | 0.6524 | 0.8154 |
| JA4 + JA4S + JA4T | 22 | 13 | 0.5912 | 0.7074 |
| JA4 + JA4S + JA4T + JA4TS | 30 | 15 | 0.6263 | 0.8554 |
| JA4+* | 33 | 15 | 0.8095 | 0.9048 |
Table 11.
Class-filtering audit for UNSW-IoTraffic (capture period: 2016-09-30 to 2017-04-13). Initial dataset samples = 747 985; initial classes = 22 for all experiments.
Table 11.
Class-filtering audit for UNSW-IoTraffic (capture period: 2016-09-30 to 2017-04-13). Initial dataset samples = 747 985; initial classes = 22 for all experiments.
| Fingerprint | Valid Samples | Samples After Filter | Trained Classes | Excluded Classes |
|---|---|---|---|---|
| JA4 | 747 985 | 6 623 | 22/22 | 0 |
| JA4S | 746 989 | 6 619 | 22/22 | 0 |
| JA4T | 746 479 | 6 601 | 22/22 | 0 |
| JA4TS | 746 479 | 6 601 | 22/22 | 0 |
| JA4X | 746 433 | 6 551 | 22/22 | 0 |
| JA4+* | 745 924 | 6 533 | 22/22 | 0 |
Table 12.
Classification performance on the JA4+* experiment using the independent UNSW-IoTraffic dataset. CI denotes the bootstrap 95% confidence interval for Macro F1.
Table 12.
Classification performance on the JA4+* experiment using the independent UNSW-IoTraffic dataset. CI denotes the bootstrap 95% confidence interval for Macro F1.
| Features | Classifier | Accuracy | Precision | Recall | Macro F1 | 95% CI |
|---|---|---|---|---|---|---|
| Compact | Dictionary | 0.9977 | 0.9987 | 0.9941 | 0.9963 | [0.9908, 1.0000] |
| Compact | RF | 0.9962 | 0.9933 | 0.9977 | 0.9952 | [0.9905, 0.9990] |
| Compact | CatBoost | 0.9992 | 0.9995 | 0.9995 | 0.9995 | [0.9985, 1.0000] |
| Decomposed | RF | 0.9992 | 0.9979 | 0.9995 | 0.9987 | [0.9954, 1.0000] |
| Decomposed | CatBoost | 0.9992 | 0.9995 | 0.9995 | 0.9995 | [0.9985, 1.0000] |
Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (http://creativecommons.org/licenses/by/4.0/).
Copyright: This open access article is published under a Creative Commons CC BY 4.0 license, which permit the free download, distribution, and reuse, provided that the author and preprint are cited in any reuse.